Author: Mike Vizard

  • CloudBolt Software Aims to Bridge DevOps and IT Divide

    CloudBolt Software Aims to Bridge DevOps and IT Divide

    CloudBolt Software today released a Winter update to its cloud management platform that aims to bridge the divide between DevOps teams and traditional IT administrators.

    IT administrators can now employ the CloudBolt platform to invoke the open source Ansible framework for automating IT processes and workflows using a graphical user interface (GUI) surfaced via a OneFuse Ansible Tower module.

    Additionally, the OneFuse Scripting module will now make it possible to automate script creation for anyone who creates a script using, for example, Terraform, and package that script in a way that IT administrators can invoke via a graphical tool.

    Jeff Kukowski, CEO of CloudBolt Software, said the goal is to make it easier for IT teams across the organization to reuse code created by a DevOps team. OneFuse provides IT with a codeless integration tool. In addition to the core cloud management platform, CloudBolt Software also provides access to a Kumolus service that enables IT teams to optimize cloud costs and provides additional governance capabilities such a generating an audit trail.

    Other capabilities added in the Winter release include deeper cost optimization analysis for VMware vCenter and Microsoft Azure environments, support for the latest release of VMware vRealize and additional C-level dashboards and reports.

    As the number of workloads deployed in production environments increases, there is going to be a greater need for some form of détente between DevOps teams and traditional IT administrators. Site reliability engineers (SREs) can typically manage a much wider range of workloads than an IT administrator. However, SREs are both expensive and hard to find and retain. IT organizations will need to find a way for IT administrators that, at best, have limited programming skills, to pick up some of the slack.

    Those IT administrators can play a critical role in minimizing the number of misconfigurations arising from provisioning IT infrastructure as code. Misconfigurations as a result of developer mistakes are rife across the cloud, and IT administrators are more inclined to check for these than are developers who are racing to deliver their next application.

    The truth is, there are a wide range of tasks that DevOps teams would just as soon see managed by IT administrators, especially if a script or runbook that addresses common issues has already been created. The trick is making that script or runbook easily accessible.

    In the meantime, IT organizations are racing to keep up with complexity in IT environments, often by applying automation at scale in a way that is both repeatable and well-documented. Whether IT professionals like it or not, the days of writing automation scripts and failing to document them are coming to an end. The real issue is ensuring that what does get automated actually works as expected, each and every time a script is applied.

  • AppDynamics Partners With Cisco to Secure Application Runtimes

    AppDynamics Partners With Cisco to Secure Application Runtimes

    AppDynamics today announced its agent software, which it provides as part of its observability platform, now has the ability to enforce application security policies.

    Developed in collaboration with the security business unit of parent company Cisco, the Cisco Secure Application offering, available from AppDynamics, can detect attacks, identify deviations in application behavior and block attacks automatically.

    Gregg Ostrowski, a regional CTO for AppDynamics, said the goal is to make it simpler for IT teams that employ AppDynamics for monitoring and observing their IT environments to also embrace DevSecOps best practices. In effect, IT teams can now piggyback security for application runtimes on their existing investment in AppDynamics, Ostrowski said.

    The AppDynamics approach provides the added benefit of easy integration with the Cisco security tools to improve collaboration between DevOps and cybersecurity teams, Ostrowski said. Security details correlated with the application topology make it easier to share context in a way that identifies the actual business relevance of any security event, he added.

    As organizations accelerate digital business transformation initiatives, Ostrowski said the need to embrace DevSecOps best practices is becoming more urgent. The level of risk attached to these types of projects is significantly higher than with previous generations of applications, Ostrowski said.

    While most organizations appreciate the need for greater application security, there’s a debate about how best to achieve that goal. There’s general agreement that developers need to be more involved. However, shifting responsibility for application security to the proverbial left often comes at the expense of developer productivity. AppDynamics is making a case for enabling IT teams, that may already rely on its application performance management (APM) platform, to enforce policies defined by the cybersecurity team.

    Of course, there’s still a need to provide developers with the tools required to write more secure code in the first place. The debate is over how involved in the cybersecurity management process developers need to be after applications are deployed in a production environment.

    Arguably, the goal should be to enable both teams to accomplish their respective tasks in a way that doesn’t require a constant stream of meetings and updates. In the event a vulnerability is discovered, it’s critical for security teams to determine the threat level that vulnerability represents. Otherwise, remediation of that vulnerability will be just one more item in a long list of patches that developers are already working on.

    Regardless of approach, there are now myriad ways to improve overall application security. In effect, the same defense-in-depth approach that IT organizations have relied on to secure network perimeters can now be applied to application security as applications are both constructed and deployed. The most significant challenge is not so much finding the tools required to improve application security, as defining the processes through which best practices can be consistently applied.

  • Oracle Includes GraalVM Support in Java SE Subscription

    Oracle Includes GraalVM Support in Java SE Subscription

    Oracle announced today it is adding a GraalVM Enterprise virtual machine for building Java applications to Java SE Subscription at no additional cost.

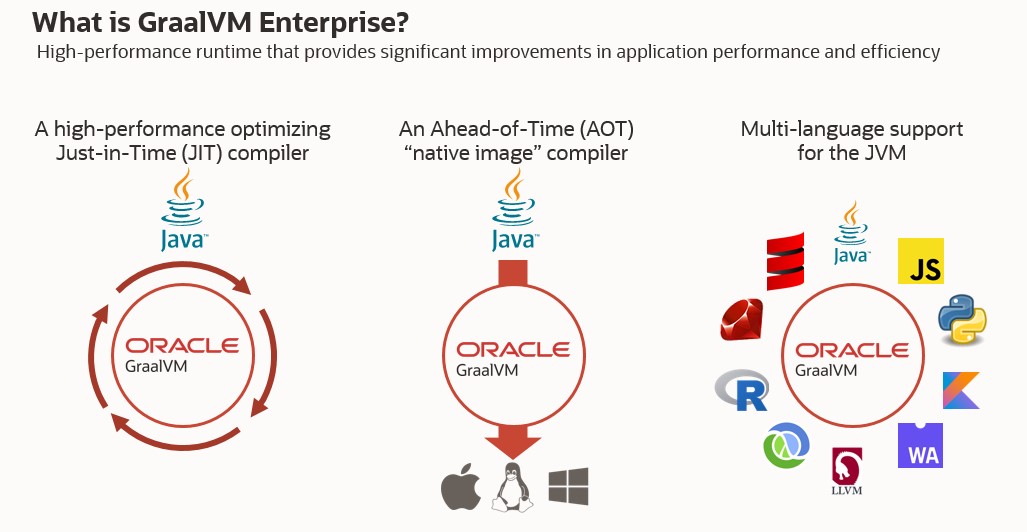
    Donald Smith, senior director of product management from the Java Platform Group at Oracle, said GraalVM Enterprise provides developers with a high-performance application runtime, built on Oracle Java SE, that includes a compiler that accelerates Java application execution. That’s critical as developers look to build microservices-based applications employing microservices that tend to be latency sensitive, Smith said.

    The first stable release of GraalVM arrived last fall. It consumes less memory, and enables Java applications to spin up faster by taking advantage of capabilities such as a just-in-time compiler. GraalVM Enterprise adds a native image utility that compiles Java and JVM-based applications ahead-of-time (AOT) into self-contained native executables. That approach only includes the classes and libraries needed to run the application, which reduces the size of the binary that gets generated.
    Including GraalVM Enterprise in the Java SE Subscription make it easier for Java developers to switch to that Java virtual machine (JVM) to build microservices rather than having to learn another language, Smith said.

    Smith said most organizations will continue to build monolithic applications at the same time they’re attempting to construct microservices. The Java SE Subscription makes it possible for developers to employ different JVMs depending on the type of application being constructed or updated, Smith said. A survey of 560 developers conducted by Oracle last month finds nearly half (48%) are already employing GraalVM to build microservices using Java.

    How much will organizations rely on Java to build microservices, given all the other programming language options available? That’s up for debate. However, being employed in the enterprise for more than 25 years, the number of developers that know Java well is substantial. Rather than waiting for those developers to become proficient in another programming language, there’s a natural tendency for organizations to want to stick with a familiar language. Each additional language introduced to build applications also tends to complicate DevOps processes in a way that can increase the total cost of IT.

    At the same time, however, the number of developers that know how to develop applications using everything from JavaScript to Go is also increasing. Oracle, via ongoing investments made in the OpenJDK project, is moving to make sure Java stays relevant at a time when the number of programming languages being employed has never been greater. For what it’s worth, GraalVM is designed to support multiple programming languages, including JavaScript.

    It’s unlikely Java will fade into obscurity any time soon. IT organizations have a vested interest in embracing next-generation JVMs, if for no other reason than making Java applications more efficient, regardless of how they are built.

    It’s also worth mentioning that frameworks – such as Quarkus from Red Hat – that enable Java-based microservices to run natively on Kubernetes clusters already rely on GraalVM. In some cases, developers may wind up employing such a framework without realizing it relies on GraalVM. In other cases, the challenge will be getting developers to opt for GraalVM as their JVM of choice when so many of them have routinely used the same JVM for more years than they care to admit.

  • CloudBees Appoints New CEO to Drive Next Level of DevOps Growth

    CloudBees Appoints New CEO to Drive Next Level of DevOps Growth

    CloudBees announced today the appointment of Stephen DeWitt as its new CEO, taking over from Sacha Labourey, who will become chief strategy officer.

    Labrourey said after leading the company for the past 10 years, and after a banner year that saw the company generate more than $100 million in revenue, the time was right to appoint a new CEO to take the company to next level. The move also allows Labourey more time to focus on product development.

    Stephen DeWitt
    Stephen DeWitt, CloudBees CEO

    DeWitt most recently served as chief strategy officer for Automation Anywhere, a provider of a robotic process automation (RPA) platform. DeWitt previously served as the CEO of WorkMarket, a labor automation platform for enterprises, Azul Systems, a provider of platform for running Java applications and Cobalt Networks, a provider of Linux servers.

    Without committing to a specific initial public offering (IPO) date, DeWitt said the ultimate goal is to put the processes in place that will enable CloudBees to grow to $200 million in revenues and beyond.

    Achieving that goal will also require tighter integration across what has become a diverse portfolio of DevOps platforms, DeWitt said. The challenge is providing IT organizations with all the benefits of that integration without locking them into any specific component, DeWitt added.

    Going forward, DeWitt said IT teams should expect to see CloudBees invest more in artificial intelligence (AI) to further automate DevOps processes. There are many low-level DevOps tasks that could be automated using machine learning algorithms to reduce the level of friction DevOps teams often encounter.

    Becoming a $200 million company, however, is more difficult than becoming a $100 million company, DeWitt said. Not only does the company have to put the processes in place to grow, but CloudBees today faces more viable competition than it did when it first pioneered the adoption of DevOps best practices.

    The number of organizations adopting DevOps best practices is not only increasing, but organizations that have implemented continuous integration/continuous delivery (CI/CD) platforms also are employing them more widely. Instead of only being employed by pockets of development teams, entire enterprises are now using DevOps best practices and standardizing on a CI/CD platform. Many of those decisions are being driven by the need to accelerate digital business transformation initiatives in the wake of the economic downturn brought on by the COVID-19 pandemic.

    As the application development stakes rise, C-level executives are also getting more involved in application development and deployment decisions, DeWitt said. Those executives not only want to accelerate the rate at which applications are built and deployed, they also want greater visibility into processes that now have a direct impact on revenue streams, DeWitt said.

    It remains to be seen just how quickly DevOps platform providers, as a whole, will grow, but with more venture capital pouring into the sector by the day, there is no shortage of fuel to throw on the proverbial DevOps fire.

  • HashiCorp Expands Managed Services Offerings

    HashiCorp Expands Managed Services Offerings

    HashiCorp today announced the general availability of its Consul service mesh as a managed service on the HashiCorp Cloud Platform (HCP) along with a beta release of a managed instance of HCP Vault, a secrets management platform, on HCP.

    HCP is currently hosted on the Amazon Web Services (AWS) platform, on which the company is making available its complete portfolio as a managed service. In the longer term, HashiCorp plans to make its managed services available on all the major cloud platforms.

    Chris Kent, director of product marketing for HashiCorp, said despite the growing number of open source service mesh alternatives, many organizations would prefer to employ a service mesh provided by a single vendor that they didn’t have to provision and maintain. HashiCorp’s Consul service mesh provides a lightweight alternative that enables service-to-service networking and security via connection authorization and encryption and spans both Kubernetes clusters and virtual machine platforms using the mutual Transport Layer Security (mTLS) protocol.

    Applications can then employ sidecar proxies in a service mesh configuration to establish TLS connections for inbound and outbound connections without ever having to directly interface with Consul itself.

    HashiCorp is making the case for Consul at a time when internecine warfare is raging between proponents of open source service mesh platforms such as Istio, Linkerd and Kuma. The Consul service mesh provides an alternative that is simpler for developers to incorporate across both microservices-based applications running on a Kubernetes cluster and legacy monolithic applications running on virtual machines, Kent said. In contrast, Istio and Linkerd are designed solely for use in Kubernetes environments.

    It’s still the early days of service mesh adoption. In addition to simplifying application traffic routing between services, one of the other benefits of service mesh is that it provides a layer of abstraction above lower-level network application programming interfaces (APIs) and protocols that is more accessible to developers. As developers become more familiar with service meshes, the ability to programmatically include network and security operations within a DevOps workflow will grow. HashiCorp is collectively positioning Consul and Vault as foundational components for creating a zero-trust architecture.

    In the meantime, each IT organization will need to determine which type of service mesh makes the most sense for their environment. In many cases, organizations may find themselves employing multiple service meshes to address different use cases. Regardless of which they choose, service meshes will soon become a permanent fixture in the proverbial solar system around which IT services revolve.

    HashiCorp claims that more than 2,000 organizations signed up to participate in the HCP Consul and HCP Vault beta programs. That level of interest suggests interest is growing in consuming IT as a service rather than as a platform that requires deployment by an internal IT team. It remains to be seen the degree to which organizations will prefer to consume those services directly from a vendor, versus a cloud service provider or third-party IT services provider.

  • Atlassian’s Shift to the Cloud Gets Underway

    Atlassian’s Shift to the Cloud Gets Underway

    Atlassian today announced the general availability of Cloud Enterprise, a cloud-based service through which organizations can mix and match the company’s various offerings under a single subscription.

    The company has signaled its intention to shift toward cloud services for months; now, the initial Cloud Enterprise subscription will cover the company’s Jira Software, Confluence and Jira Service Management offerings.

    Bala Venkatrao, head of product for Enterprise Cloud at Atlassian, said the goal is to make it more cost efficient for organizations to consume the company’s software versus merely acquiring a license to deploy software in an on-premises IT environment.

    The company is also making controls available that enable governance of user and change management via a centralized admin hub. Administrators can assign users to instances, configure security policies and monitor usage trends through the hub. There are also built-in integrations with third-party identity-as-a-service providers, to enable administrators to automate provisioning and de-provisioning.

    Administrators can also set up and customize multiple application instances; they can keep data pinned to different regions to customize those instances with specific marketplace applications or configurations for compliance purposes.

    Finally, a marketplace will allow IT organizations to expand the number of applications they consume from Atlassian and its partners. A smart links and app switcher capability for Jira and Confluence Cloud enable easy collaboration across different instances of Atlassian applications.

    Atlassian currently has more than 194,000 customers, so it may take some time to transition the existing installed base to this model. In the meantime, Atlassian is pushing as many new customers as possible toward a cloud platform that makes it easier for Atlassian to keep customers current on the latest release of its software. Atlassian plans to support up to 20,000 users per application instance by later this year.

    Venkatrao said while the Atlassian portfolio is frequently consumed by individual end users, the Cloud Enterprise offering is designed to appeal to CIOs, and other senior level executives, that want to centralize billing for application services now accessed via the cloud. That approach will make it easier for large organizations to take advantage of discounts they may qualify for as overall usage increases, Venkatrao said.

    While Atlassian may be a little late to the software-as-a-service (SaaS) application game, Venkatrao noted that the Cloud Enterprise platform will make it simpler for Atlassian to apply AI to the metadata it will collect. Atlassian has already leveraged AI to improve document search within Confluence and Jira, in addition to employing predictive analytics to surface recommendations for including personnel on a project.

    It may be a slow transition to the cloud for Atlassian, but that transition is clearly underway.

  • Tidelift Secures Open Source Software Supply Chains

    Tidelift Secures Open Source Software Supply Chains

    Tidelift today announced the general availability of a platform dubbed Tidelift catalogs, through which enterprise IT organizations can more effectively manage their open source supply chains.

    Donald Fischer, Tidelift’s CEO, says the Tidelift catalogs platform enables IT teams to curate, track and manage open source components that have been vetted and adhere to compliance requirements by Tidelift. The company is working directly with the maintainers of those open source projects to compensate them for making that additional effort, said Fischer.

    Developers can reliably pull components spanning common language frameworks like JavaScript, Python, Java, Ruby, PHP, .NET and Rust, with more programming environments to follow, added Fischer. Those components are made available via a Tidelift Subscription service.

    Fischer said Tidelift is going beyond merely scanning open source components for vulnerabilities. The company is ensuring that when developers access versions of open source components, those versions comply with specific sets of policies, said Fischer. As a part of that subscription service, Tidelift monitors components for vulnerabilities as they are discovered, and works with maintainers to implement updates as needed.

    While many organizations are starting to employ DevSecOps best processes, Fischer said the discovery of an issue involving open source components often comes far too late in the process. The Tidelift catalog approach ensures there are no last-minute surprise that are only discovered just before an application is about to be deployed in a production environment.

    Securing software supply chains has become a higher priority since it was revealed that cybercriminals successfully inserted malware into an application update made to network monitoring software provided by SolarWinds. That malware subsequently rippled across IT environments involving multiple corporate entities, as well as several Federal agencies.

    Of course, securing a software supply chain doesn’t happen overnight. Most IT organizations don’t have the processes and platforms required to vet open source components and frameworks. Tidelift is betting most of those organizations would prefer to subscribe to a service, rather than set up that infrastructure themselves. However, for organizations that require in-house monitoring of all the elements of their application development platform, Tidelift will make an on-premises edition of its platform available.

    As organizations become more dependent on software, the potential impact malware can have on their operations can be extensive. Organizations of all sizes should expect to be fielding inquiries from customers, suppliers and partners concerning the level of rigor being applied to their software development processes. In effect, they are going to demand to know the provenance of the software they are being asked to implicitly trust. In many cases, those inquiries will provide the incentive to accelerate adoption of DevScOps best practices.

    The days when organizations blindly used software with little regard to its origins are coming to a close. That doesn’t mean reliance on open source software is necessarily going to decline; however, it does mean application development teams will be held more accountable for the open source components they rely on.

  • vFunction Automates Conversion of Java Apps to Microservices

    vFunction Automates Conversion of Java Apps to Microservices

    vFunction has developed an eponymous platform capable of automatically converting a monolithic application written in Java into a set of microservices. The startup is emerging from stealth mode today.

    Fresh from raising $12.2 million in seed funding, vFunction CEO Moti Rafalin said the company’s platform employs dynamic analysis, static analysis, data science and automation to enable IT teams to reengineer, in a repeatable fashion, the source code used to create monolithic Java applications.

    As part of that process, vFunction also detects and eliminates code that is no longer executed to reduce the footprint of an application, minimize security risks and overall maintenance tasks.

    The vFunction platform is deployed as a server that communicates with agent software injected into the legacy monolithic application. The server then creates a microservice that is scanned by additional tools to determine how best to optimize it to run on, for example, a Kubernetes cluster based on the Red Hat OpenShift platform, said Rafalin.

    IT teams can also employ vFunction to determine which monolithic applications are better suited to being converted into a set of microservices that can be automatically extracted into separate compilable projects. Each project comes with an estimated timetable for completion that can be accessed via a Modernization Factory Dashboard and Application Complexity Assessment tool provided by the platform.

    Rafalin said most monolithic applications are made up of large amounts of ‘spaghetti code’ that was added over multiple generations by different development teams. Manually analyzing that code as part of an effort to refactor a legacy application would require weeks of effort, Rafalin said. As such, the rate at which most organizations are re-engineering applications is extremely slow, he said.

    In fact, it’s not unheard of for IT organizations to to start, but quickly abandon such because the time and effort required proved too costly. vFunction claims its automated, domain-driven processes accelerate manual refactoring by a factor of ten, resulting in a savings of anywhere from $300,000 to $500,000 per application.

    Pricing for vFunction is based on a per-application model. The company has also established alliances with system integrators such as HCL Technologies, Tata Consulting Services and Wipro that are regularly contracted by IT organizations to refactor their applications.

    Of course, not every monolithic application needs to be converted into a set of microservices. However, most monolithic applications have components that would be easier to maintain and support as a distinct microservice. Organizations, in general, are embracing microservices to build applications that are more resilient. In the event a microservice becomes unavailable, requests for services are rerouted to another microservice to make sure the application degrades gracefully, rather than crashes altogether. The challenge is that, over time, the dependencies that can exist between hundreds of microservices can be more challenging to manage than those of the monolithic application being replaced.

  • OpenTelemetry Project Gains Log Agent Software from observIQ

    OpenTelemetry Project Gains Log Agent Software from observIQ

    Stanza, an open source log agent developed by observIQ, a provider of an observability platform, has become part of the OpenTelemetry Project for collecting telemetry data.

    Mike Kelly, CTO and co-founder, observIQ, said Stanza will make it possible to collect log data alongside other telemetry data using a common application programming interface (API) and software development kit (SDK).

    OpenTelemetry is currently a sandbox-level project being developed under the auspices of the Cloud Native Computing Foundation (CNCF); it provides a set of open source libraries, agents and other components for collecting the telemetry data consumed by observability and IT monitoring tools.

    Contributors to the OpenTelemetry Project include Amazon Web Services (AWS), Elastic, Google, Honeycomb, Lightstep, New Relic and Splunk. After Kubernetes, Kelly said the OpenTelemetry Project is now the most popular open source initiative being advanced by the CNCF.

    The OpenTelemetry Project is still a long way from delivering agent software that will be widely employed on an IT production environment. However, the potential implications of the project are already being widely noticed. Rather than having to deploy, manage and update agent software for individual IT management tools, it will soon be possible to deploy a single set of agent software to generate data that can be consumed by multiple platforms.

    That shift will enable providers of these platforms to focus more of their effort on enhancing their analytics capabilities rather than developing proprietary agent software that typically doesn’t provide much differentiated value, Kelly said.

    Stanza is part of an IT observability platform developed by observIQ when it was previously known as Blue Medora. After selling its platform for integrating monitoring tools to VMware, Blue Medora changed its name to observIQ. Now, it is making an effort to advance adoption of an observability platform that it makes available as a software-as-a-service (SaaS) application.

    Will DevOps teams roll out elements of OpenTelemetry themselves, or wait for the observability and monitoring tool and platform providers to support open source agents that would automatically be deployed? That remains to be seen. Regardless, the total cost of observability should decline, as open source agent software replaces the proprietary agent software strewn across enterprise IT environments today. The expectation for vendors is that more applications will be consuming analytics data surfaced by the observability and monitoring platforms they provide.

    Of course, it will be a while before that dream is fully realized. In the meantime, IT organizations will need to carefully evaluate the total cost of observability against the business value of the application deployed. Cost is one of the reasons application performance management (APM) tools are not widely employed today. Of course, as IT environments become more complex, thanks to the rise of microservices and serverless computing frameworks, it’s also become increasingly apparent that observability will soon be a capability IT teams can’t afford to do without.

  • ARMO Aims to Simplify Microservices Security

    ARMO Aims to Simplify Microservices Security

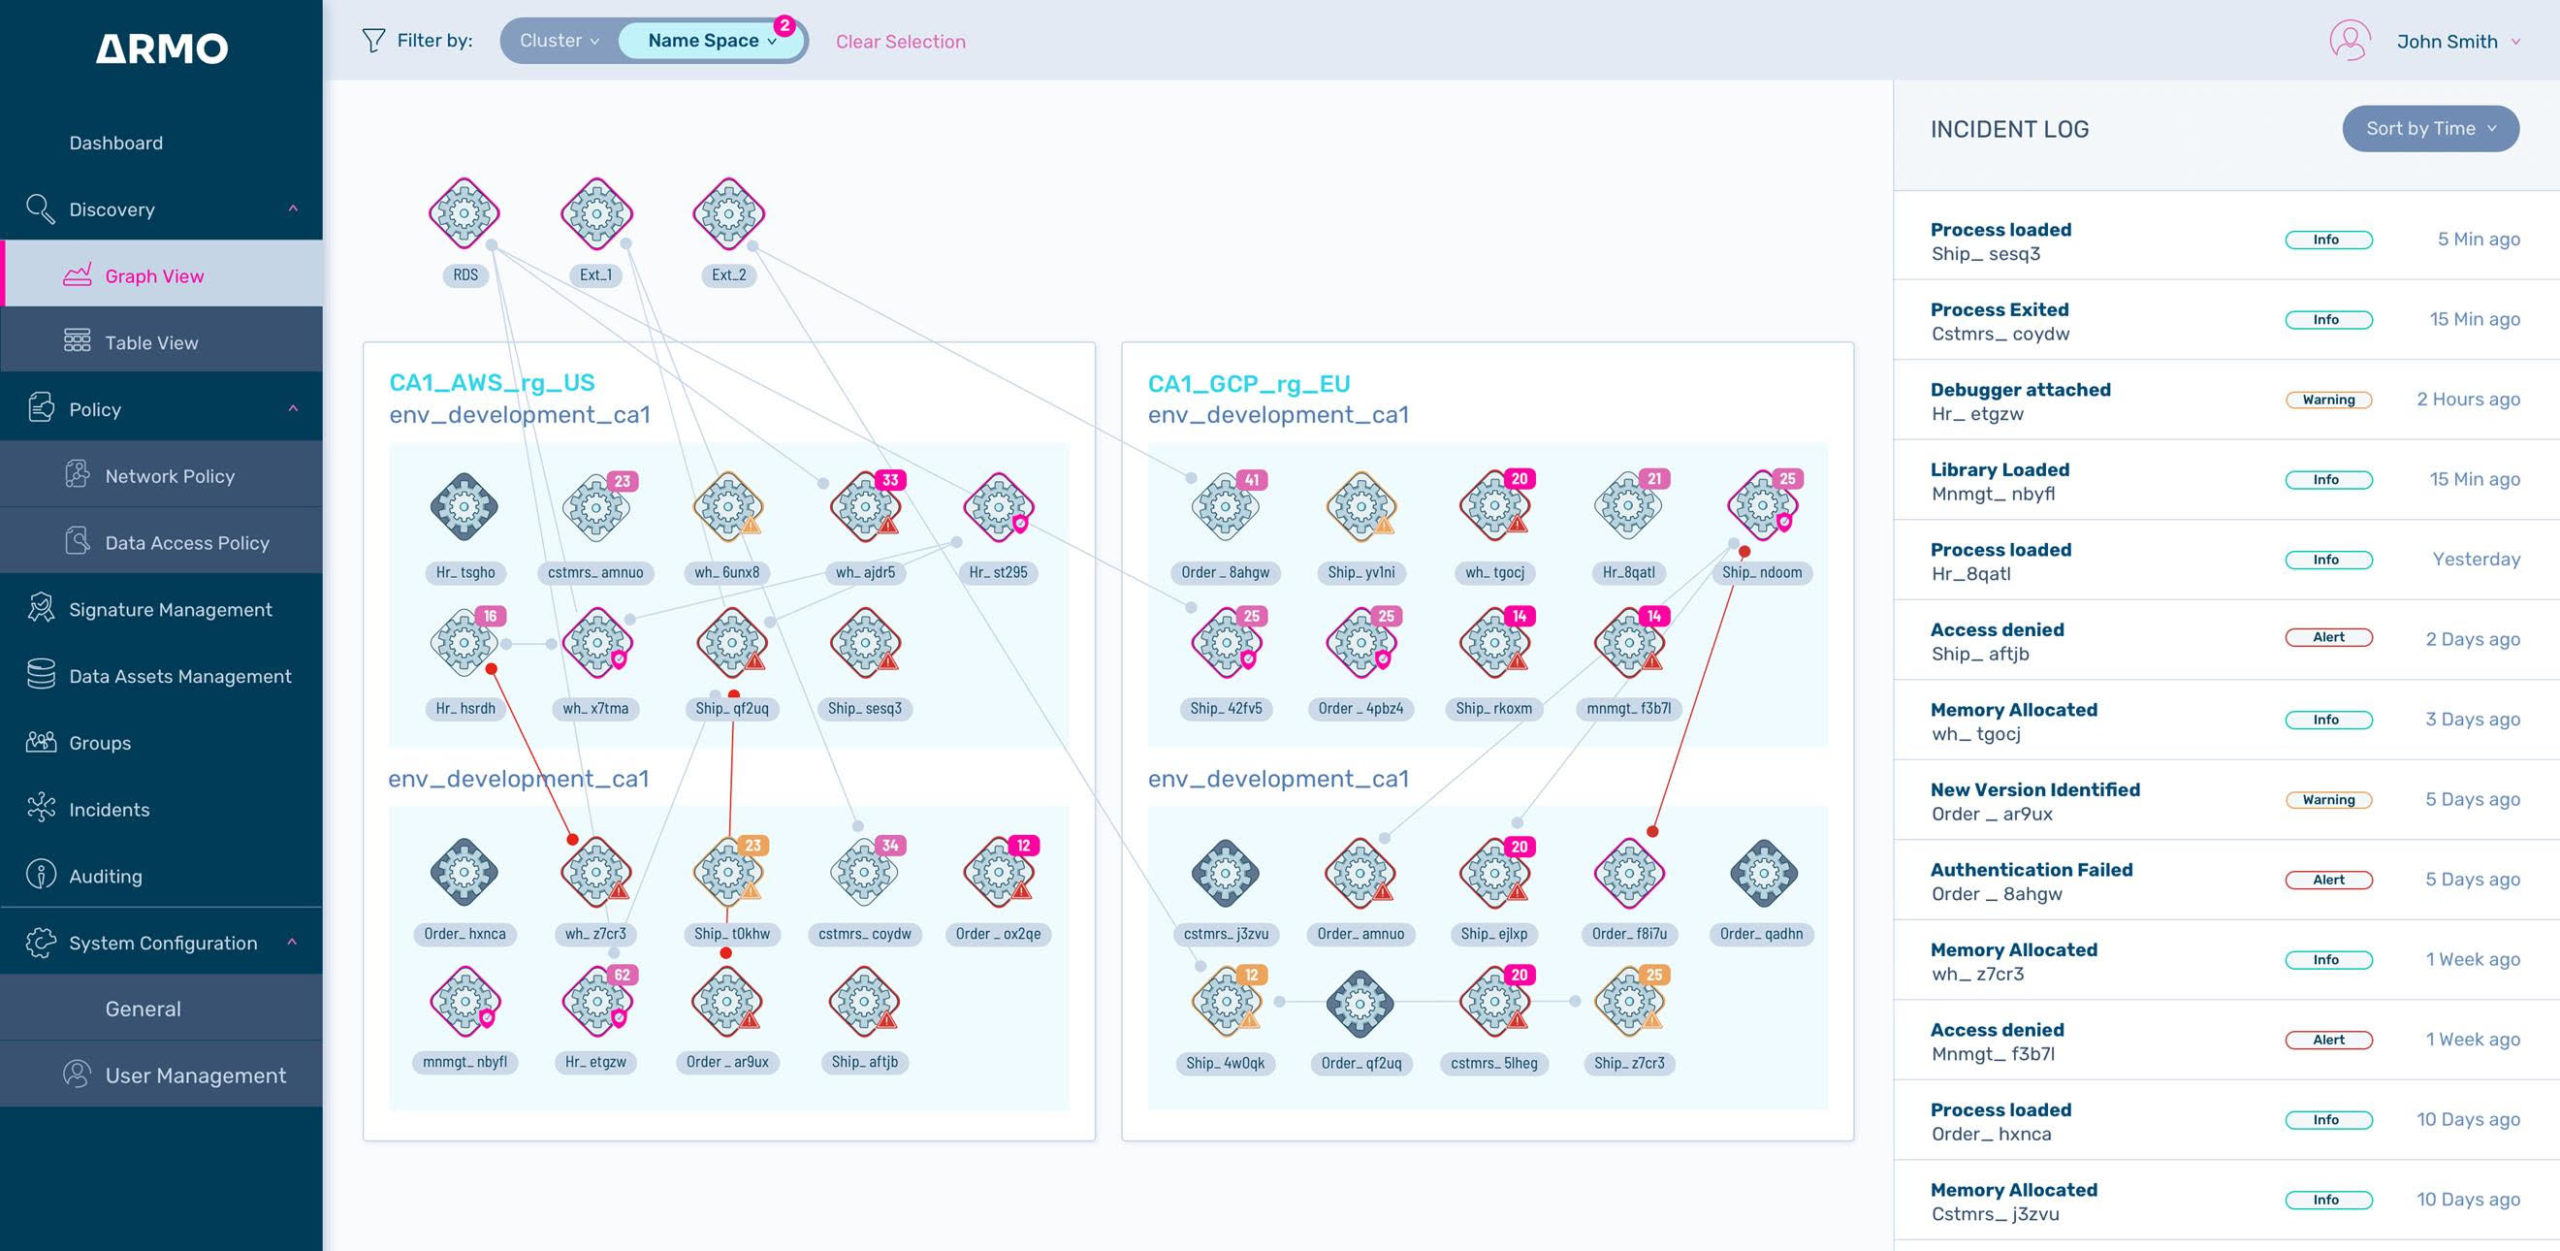
    ARMO this week emerged from stealth to launch a platform to secure cloud-native workloads and improve visibility. The ARMO Workload Fabric technology attaches code within the memory invoked by a microservice to enable cybersecurity policies to be applied via a cloud service.

    Company CEO Shauli Rozen said the ARMO Workload Fabric is designed to enable IT organizations to implement a zero-trust architecture more easily within the context of a DevSecOps workflow.

    Fresh from raising $4.5 million in seed funding, Rozen said ARMO’s approach eliminates the need to deploy and manage agent software, container sidecars or runtime application self-protection (RASP) software to enforce security policies across what inevitably will become thousands of microservices distributed across an enterprise IT environment.

    That leaner approach then allows for a centralized management platform that can be deployed on a cloud or on-premises IT environment to apply policies that restrict which microservices can communicate with one another, Rozen said. The approach would ensure that only microservices developed using a continuous integration/continuous delivery (CI/CD) platform are allowed to communicate with other microservices, Rozen said.

    Integration with multiple CI/CD platforms is already provided, added Rozen.

    That approach allows policies to be applied to microservices regardless of how they are constructed, Rozen said. That capability is critical, because developers are building microservices using everything from Python and Java to containers, he said. Many of those microservices are also frequently replaced, Rozen said, which can make updating any associated agent software a significant DevOps challenge. Given all the existing dependencies between microservices, overall application environment security is only as strong as the proverbial weakest link. The ARMO Workload Fabric enables developers to add a small amount of code to implement security policies each time a microservice is rolled out into a production environment.

    As part of an effort to make it simpler for IT organizations to apply those policies, ARMO provides a pre-built set of policies that organizations can immediately apply, in addition to creating their own polices over time, Rozen said. In many cases, IT teams simply don’t have the time or expertise required to build those policies, Rozen added.

    Microservices are being built and deployed at such a breakneck pace that it’s nearly impossible for cybersecurity teams to keep up. The ARMO Workload Fabric provides cybersecurity teams a means to centrally manage security policies that would otherwise be implemented as code by developers. It provides a level of observability for how those cybersecurity policies are being implemented across microservices that typically have a lot of dependencies on one another, Rozen said.

    Most organizations today recognize there is a clear need to shift responsibility for application security further left toward developers. The challenge is finding a practical way to achieve that goal, and in a way that doesn’t adversely impact the rate at which applications are being developed. The key to achieving that goal is finding a way to apply microservice security polices that causes the least amount of friction possible to existing DevOps workflows.