

Tricentis is providing early access to multiple artificial intelligence (AI) capabilities that it is gearing up to roll out later this year via a Tricentis Transform initiative, including an autonomous […]
CI/CD for AI-Enabled Applications: Why Traditional Deployment Pipelines Need to Evolve

Traditional CI/CD pipelines are optimized around a familiar assumption: source code changes, automated tests validate the change, a build artifact is produced, and the application is promoted through environments. AI-enabled […]
Why Self-Healing Tests Need a Deployment Gate

When an end-to-end test fails after a front-end change, the repair often looks routine. A class name changed. A button moved. A selector that used to be unique now matches […]
Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed

Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered […]
Production-Safe Testing: The Missing Piece in Most DevSecOps Strategies
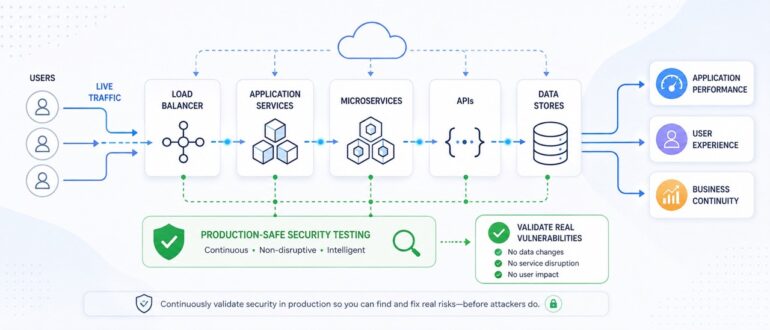
Most DevSecOps teams invest heavily in security before deployment, yet attackers target the production environment where applications, APIs, and user behavior are constantly changing. If security validation stops before release, […]
ProjectDiscovery Brings Open Source AI Testing to Vulnerability Discovery

ProjectDiscovery has made available an autonomous security testing platform that leverages an open source artificial intelligence (AI) testing framework to detect and validate vulnerabilities at a lower total cost. Company […]
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
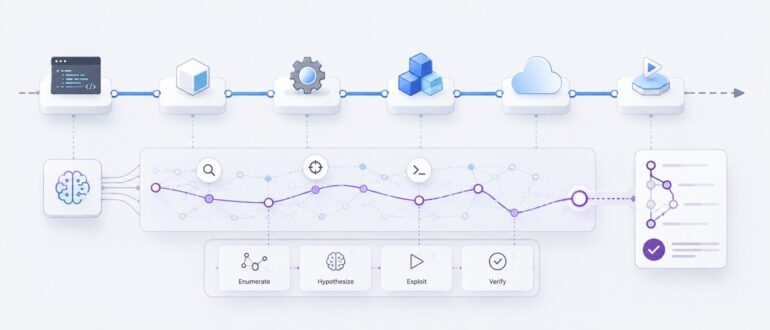
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in […]
Survey Surfaces Rising Tide of Production Issues Traced Back to AI Code

A survey of 400 business and engineering executives finds 80% have traced a production incident, outage, or customer-impacting defect to code generated by artificial intelligence (AI) tools in the past […]
Sandbox Testing for API-Heavy Systems: What Changes When You Don’t Own the Dependency

Sandbox testing works well when your team controls both sides of the integration. You define the service, you define the mock, you know exactly what the sandbox should return. That […]
Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads

Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion […]
- 1
- 2
- 3
- …
- 81
- Next Page »
