Author: Mitch Ashley

  • 5 Ways to Accelerate Standards Compliance With Static Code Analysis

    5 Ways to Accelerate Standards Compliance With Static Code Analysis

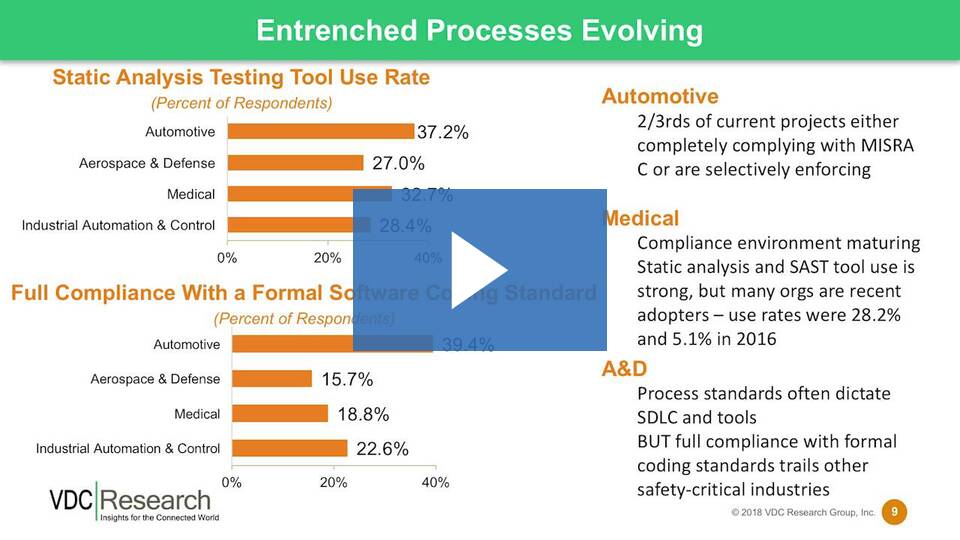
    In mission- and safety-critical industries, static code analysis is essential to facilitating the development of robust and reliable software. However, according to VDC Research, a B2B technology market intelligence and consulting firm, only 27% of embedded developers report using static code analysis tools. This raises an important question: Why is the adoption rate for static code analysis tools so low, when they are more effective than manual code reviews at finding coding errors, weaknesses, and vulnerabilities?

    In this webinar, we’ll answer that question, as well as explain how to effectively implement a static code analysis tool in your software development process. In addition, our presenters will review the results of the VDC Research paper on software development trends, techniques and best practices for standards compliance within embedded software development teams.

    Three key takeaways from the webinar include:
    1. Understanding trends for standards compliance.
    2. Identifying common challenges for automotive, medical, industrial automation and other types of embedded software applications.
    3. Learning best practices for achieving compliance using different tools, techniques, and processes.
     

    To read more, please visit: https://www.perforce.com/webinars/kw/5-ways-accelerate-standards-compliance-static-code-analysis

  • Top 10 Embedded Security Vulnerabilities

    Top 10 Embedded Security Vulnerabilities

    Nearly all of detected security vulnerabilities can be attributed to just 10 types. Here, we discuss the most common cybersecurity vulnerabilities and offer guidance on how to mitigate their risk.

    Vulnerability 10: Numeric Errors

    Numeric errors can refer to several different categories of problems, including wrap around errors, improper validation of array index, integer overflow, incorrect byte ordering and more. A common place for numeric errors is in math calculations and data overflow from an external source.

    Vulnerability 9: Cryptographic Issues

    Cryptographic issues are weaknesses related to the use of cryptography. This type of vulnerability is often caused by missing encryption of sensitive data, inadequate encryption strength and more.

    Vulnerability 8: Code Injection

    Code injections effect interpreted environments such as PHP.

    Vulnerability 7: Code

    This is a catchall vulnerability that can include such things as mismanaging passwords, improper handling of API contracts and code generation issues.

    Vulnerability 6: Resource Management Errors

    This type of vulnerability refers to a wide range of issues, including improper management of system resources, resource locking and insufficient resource pool.

    Vulnerability 5: Improper Access Control

    Improper access control is when software does not restrict, or incorrectly restricts, access to a resource from an unauthorized actor.

    Vulnerability 4: Improper Input Validation

    Improper input validation refers to getting incorrect or missing information from anything that could possibly impact a program’s control flow or data flow.

    Vulnerability 3: Information Exposure

    Information exposure is the intentional or unintentional disclosure of information that isn’t explicitly authorized.

    Vulnerability 2: Access Control

    This vulnerability refers to any weakness related to the management of permissions, privileges or other security features.

    Vulnerability 1: Memory Buffer Problems

    Memory buffer problems occur when software can read or write to locations outside the boundaries of the memory buffer.

    How to Prevent Cyberattacks

    An effective way to address each of these vulnerabilities is to rely on a static code analysis and static application security testing (SAST) tool. These types of tools analyze your code as it’s being written for potential coding errors, bugs and vulnerabilities. By addressing vulnerabilities earlier in development, you save time and money.

    For a more in-depth look at these 10 vulnerabilities and how to best mitigate their potential risk, review the associated white paper.

    To read more, please visit: www.perforce.com/blog/kw/common-software-vulnerabilities

  • What Is ISO 21434? Compliance Tips for Automotive Software Developers

    What Is ISO 21434? Compliance Tips for Automotive Software Developers

    What Is ISO 21434? Compliance Tips for Automotive Software Developers

    To read more, please visit: https://www.perforce.com/blog/qac/ISO-21434-Compliance

  • What is the NIST Cybersecurity Framework?

    What is the NIST Cybersecurity Framework?

    Cybersecurity threats are easier to handle when you have a framework to build off of. That’s why NIST developed the Cybersecurity Framework. Learn more.

    What You Need to Know About the NIST Cybersecurity Framework

    The National Institute of Standards and Technology, or NIST, helps organizations to better understand and manage their cybersecurity risks. NIST does this through its Cybersecurity Framework.

    The 5 Elements of the NIST Cybersecurity Framework

    There are five central elements of the NIST Cybersecurity Framework:

    1. Identify
    2. Protect
    3. Detect
    4. Respond
    5. Recover

    The 3 Components of the NIST Cybersecurity Framework

    In addition to the five main elements of the NIST Cybersecurity Framework, there are also three essential components.

    Framework Core: The Framework Core provides you with a set of activities to help you achieve specific cybersecurity outcomes. In order to help you achieve each activity, the Framework Core provides you with examples.

    Implementation Tiers: The Implementation Tiers provide you with an outline to increase the sophistication in your cybersecurity risk management.

    Framework Profiles: The Framework Profiles outline your cybersecurity activities and provides a look at the potential cybersecurity outcomes needed to meet your cybersecurity goals.

    How to Use the NIST Cybersecurity Framework

    In order to use the NIST Cybersecurity Framework, you must follow these three steps:

    1. Determine the appropriate implementation tier.
    2. Understand the gap between its current and target profiles.
    3. Put plans in place to implement the activities from the Framework Core to move toward the target profiles.

    The CIS Controls for NIST Cybersecurity Framework

    The Center for Internet Security (CIS) regularly publishes CIS Critical Security Controls that map to the NIST Cybersecurity Framework. While there are many sections to the CIS Controls, the most relevant is CIS Control 18, Application Software Security. The section recommends the following actions:

    1. Establish secure coding practices.
    2. Ensure software development personnel are trained in secure coding.
    3. Apply static and dynamic code analysis tools.

    To read more, please visit: https://www.perforce.com/blog/kw/nist-cybersecurity-static-analysis

  • What Is OWASP?

    What Is OWASP?

    With cybersecurity attacks rising, it is important for you to enforce secure software best practices, like OWASP and the OWASP Top 10. OWASP helps you to safeguard your code against software security vulnerabilities. Continue reading to learn why OWASP is important.

    What You Need to Know About OWASP

    The Open Web Application Security Project (OWASP) is an international nonprofit organization that educates software development teams—like yours—on how to conceive, develop, acquire, operate and maintain secure applications. Each of OWASP’s materials have been developed to improve your application security through your team, your processes and your technology.

    What You Need to Know About OWASP Top 10

    The most well-known OWASP resource is the OWASP Top 10. Every year, a team of security experts updates the OWASP Top 10 to include the 10 most critical web application and API security risks.

    The 2020 OWASP Top 10 is as follows:

    1. Injection
    2. Broken Authentication
    3. Sensitive Data Exposure
    4. XML External Entities (XXE)
    5. Broken Access Control
    6. Security Misconfiguration
    7. Cross-Site Scripting (XSS)
    8. Insecure Deserialization
    9. Using Components with Known Vulnerabilities
    10. Insufficient Logging and Monitoring

    Here Is Why OWASP Is Important

    OWASP and the OWASP Top 10 is important as it provides you with the following three benefits:

    1. It helps you to safeguard against cybersecurity vulnerabilities.
    2. It helps you strengthen software encryption.
    3. It helps you reduce the number of security errors, bugs, and defects in the code.

    Why a Static Code Analysis Tool Is Beneficial for OWASP

    One of the most effective practices for enforcing OWASP is to use a SAST tool. A SAST tool helps you to enforce secure coding standards and best practices. In addition, a SAST tool is able to flag security violations and provide you with guidance on how to fix those vulnerabilities and weaknesses.

    To read more, please visit: https://www.perforce.com/blog/kw/what-is-OWASP

  • What Is PA-DSS?

    What Is PA-DSS?

    If you develop payment application software, you must ensure that it is secure and compliant with PA DSS. Read on to learn more about the payment application security standard.

    What You Need to Know About PA DSS

    The Payment Application Data Security Standard (PA DSS) is a part of PCI DSS and is a global security standard. PA DSS applies to the development of payment application software. What’s more, if you are a software vendor that makes and sells payment applications, you must comply with PA DSS. This is to ensure the security of all of your software components. Compliance is essential because if you do not comply, you could receive massive fines.

    Important Requirements for PA DSS Compliance

    The PA DSS requirements apply to the storing, processing and transmitting of cardholder data and sensitive authentication data. There are 14 requirements that every organization that handles credit card information must follow:

    1. Do not retain full track data, card verification code or value (CAV2, CID, CVC2, CVV2), or PIN block data.
    2. Protect stored cardholder data.
    3. Provide secure authentication features.
    4. Log payment application activity.
    5. Develop secure payment applications.
    6. Protect wireless transmissions.
    7. Test payment applications to address vulnerabilities and maintain payment application updates.
    8. Facilitate secure network implementation.
    9. Cardholder data must never be stored on a server connected to the internet.
    10. Facilitate secure remote access to payment applications.
    11. Encrypt sensitive traffic over public networks.
    12. Secure all non-console administrative access.
    13. Maintain a PA-DSS Implementation Guide for customers, resellers, and integrators.
    14. Assign PA-DSS responsibilities for personnel. And maintain training programs for personnel, customers, resellers, and integrators. The Steps to Achieve PA DSS Compliance.

    There are five simple steps in order to comply with PA DSS:

    1. Comply with Requirement 5, which outlines the process for how to develop secure payment applications.
    2. Apply coding standards, such as OWASP, CWE, and CERT.
    3. Train developers in secure coding.
    4. Use a SAST tool to enforce PA DSS requirements automatically.

    To read more, please visit: https://www.perforce.com/blog/kw/what-is-pa-dss

  • Best Practices for a Secure Software Development Project

    Best Practices for a Secure Software Development Project

    The beginning of any new software development project can be daunting, as there are many decisions that need to be made and considerations that must be thought through. Often this includes defining project requirements, selecting the right processes, choosing the right tools and ensuring software security.

    In this webinar, we will walk you through the most time-consuming and difficult challenges of starting a new project.

    This includes the following four topics:
    1. Project requirements
    2. Development processes
    3. Tool selection
    4. DevOps/DevSecOps pipeline management


    To read more, please visit: https://www.perforce.com/webinars/kw/best-practices-secure-software-development-project

  • 5 Ways to Improve Developer Output With Static Analysis

    5 Ways to Improve Developer Output With Static Analysis

    Developers often have to produce efficient, effective code under tight deadlines. Without the proper software development tools to support this work, coding errors and vulnerabilities could occur. For that reason, it is important to use a static code analysis tool, which verifies the security, quality and compliance of your code as it is being written.

    In this webinar, we will outline three best practices for effective use of a static code analysis tool to improve your output, including:
    1. How to effectively achieve thorough coverage with a static code analysis tool.
    2. How to best use a static code analysis tool with mission-critical systems.
    3. How to achieve gains through effective, automated code analysis.


    To read more, please visit: https://www.perforce.com/webinars/kw/5-ways-improve-developer-output-static-analysis

  • How to Prevent Cybersecurity Threats With Secure Code

    How to Prevent Cybersecurity Threats With Secure Code

    Unfortunately, cybersecurity attacks are an ever-present threat for organizations of all sizes and industries. In fact, a cybersecurity threat is estimated to occur every 39 seconds. For that reason, it is important to understand the how, what and why of cybersecurity threats.

    The How, What and Why of Cybersecurity Threats

    Any malicious attack that threatens to damage software applications is considered to be a cybersecurity threat.

    In order to ensure that your software is safeguarded against any and all cybersecurity threats, you must take the appropriate steps, which includes:

    • Having an understanding of what the most common types of cybersecurity threats that you’ll most likely encounter.
    • Adopting effective secure coding practices.
    • Providing your team with software security training.
    • Using secure software tools — like static code analysis and SAST tools.

    By following these steps, you can more effectively safeguard your software.

    How to Prevent Cybersecurity Threats

    In order to prevent cybersecurity threats, you should use the following secure software development best practices:

    Establish Software Design Requirements

    You should establish software design requirements specifically to prevent and/or mitigate cybersecurity threats. By doing this, you can better address and eliminate potential threats.

    Enforce Secure Coding Standards for Cybersecurity Threats

    Software that is developed with secure coding standards—such as CERT and CWE—helps to prevent, detect and eliminate cybersecurity threats.

    Test Early for Cybersecurity Threats

    You should test your code early and often to identify potential vulnerabilities in your code that could lead to a cybersecurity attack.

    How SAST Tools Help to Prevent Cybersecurity Threats

    With the appropriate tools — such as static code analysis and SAST tools — you can better ensure the security and quality of your software. The reason for this is that both a static code analysis and SAST tool are able to automate vulnerability detection, test all of your code as it is being written, and easily integrates into your DevSecOps processes.

    To read more, please visit: https://www.perforce.com/blog/kw/best-practices-to-prevent-cybersecurity-threats

  • What is Differential Analysis?

    What is Differential Analysis?

    Differential analysis is an emerging solution for static analysis tools. It is a relatively recent solution, but it’s important to understand what it is, how it works and why you should care.

    What’s Differential Analysis?

    Put simply, differential analysis is a form of “fast feedback” static code analysis. By using system context data from previous analysis builds, the static analyzer examines only the files that are new or that have changed. This enables the static code analyzer to provide you with analysis results as if your entire system had been analyzed — meaning differential analysis provides you with the shortest possible analysis times while maintaining the accuracy and detail of your analysis data.

    Differential vs. Incremental Analysis

    Differential analysis is an improvement upon the more traditional incremental analysis, as it requires no prior analysis build of the software on your workstation. This is also what makes differential analysis ideal for DevOps processes — like CI/CD pipelines.

    The Importance of Differential Analysis

    Differential analysis shortens analysis times and provides you with faster feedback, which is incredibly beneficial. Especially if you need to comply with some kind of coding standard, which often involves running a local or pre-commit analysis of your code. In general, this involves running an analysis on the entire codebase to identify any new issues. While this works well for smaller projects with smaller codebases, problems – such as extended analysis times –  can arise when working with a larger codebases. However, with differential analysis, you analyze only the changed files, significantly reducing the amount of time the analysis takes.

    How Differential Analysis Works

    Without getting overly technical, here is how differential analysis works.

    1. The static code analysis tool connects to a server project.
    2. You run an integration analysis.
    3. You run an analysis of the changed code.

    To read more, please visit: https://www.perforce.com/blog/kw/what-is-differential-analysis