Tag: marketing

  • Product Evaluation Discussions

    Product Evaluation Discussions

    Instead of doing a predictions blog like 99% of the punditry, I figured I would do an awareness blog to wrap up 2022. Every year, you deal with a wide variety of people trying to tell you about products that may (or may not) be useful to your IT efforts. Some of the products even make it to the evaluation phase and while a few get installed, a smaller number get used.

    One of the many ways to minimize your time investment when talking about the bewildering array of new DevOps technologies and products is to know where the information you are consuming comes from. Here is my start at a list of information sources, where the information they impart comes from and how to get the most out of these sources.

    Marketing: The marketing team at any organization exists to spread the word about the product’s good points. Most marketing professionals only admit weakness in the underlying product if pressed. This is expected–if the sole purpose of your job is to tell the world why the product is needed, blathering on and on about the weak bits is not going to work out. But we all know there are no perfect products, even before you account for all of the environmental differences we’re installing into. So listen – they will present the product in the best light possible and have useful knowledge, particularly early in the evaluation process.

    Sales: The sales team wants to sell products, but they also are invested in happy customers. A good sales rep in high-tech is building relationships because organizations can create an income stream if the product’s value is realized on their site. This makes them practical. Their goal is definitely to represent the product and company positively, but in a light that admits more weaknesses and offers workarounds for the deal breakers.

    Sales Engineers: A lot of the sales team’s practicality comes from the team’s engineer(s). They’re the ones that have to help you get things installed and running, so they have a vested interest in the organization knowing ahead of time what will require work and what the risks are. Given a choice, talk to the SE alone before signing a contract–not because sales lies, but because the SE is there specifically to note issues that might crop up and how to get around them.

    Crowd Evaluations: Two things to remember about crowd rating sites–the participants are volunteers on the best sites, paid contributors on others. For paid contributors, well, the motivation is pretty clear. For many voluntary participants, the motivation is that they either love or loathe the product. Most of these sites allow vendors to respond to commentary, and some even allow vendors to have evals removed. No one offers a service where glowing vendor reviews can be corrected … keep that in mind. These sites are useful, and a few of them are mostly people that want to help. So find the good ones (I’m not advertising anything here, so no links–sorry) and use them.

    Analysts: Nearly all of the analysts I know–be they GigaOm analysts or a competitor–have experience in the field. They have done it, and most of them continue to keep their hands in the mix somehow. While I have not written (or maintained) a line of code in months, I do attempt to do so regularly. At the individual analyst level, the thing to watch is how long it’s been and how current they are. Some do pure analysis and haven’t touched the toys in a decade or more, and for C-level analysis, this is great … but for implementation recommendations, best to find a different source.

    Analyst Firms: This is where the real issues in analysis creep in. As an enterprise architect, I dealt with an analyst firm that–at the time, at least–would say whatever we wanted them to say. Totally useless in evaluations, but it worked well when convincing our technical advisory committee to approve the right approach. Each firm comes at the problems with its own lens, and being aware of a given firm’s slant is a good step to understanding how to use them–or if you should rely on them at all.

    Press: The age of pure-play press is largely dead, leaving a lot of “Paid for publication” out there. While there is still non-sponsored content being developed (one of the few rules Techstrong Group has for my writing of this blog is that I should avoid mentioning products; for example, making sponsorship they may pursue more about their vendor relationships and how many of you are reading my drivel), the majority of what is published as “articles” is “marketing” and should be treated as such. Reading this content can be useful for early education but not so much for evaluations.

    Internal Champions: Not the mandatory sponsor most projects require, but the person inside that is driving the org to look at a solution. These people are generally key. They know the environment, they know the product, they have ideas on how the product could help the environment, and they have a history in the organization. Whether their ideas about how various products help the company have panned out with other tools, for example. Of course the usual caveats apply… Security people still think you should be doing more to lock out bad actors – that is what they’re paid for, but that influences their evaluation of a new security product and how it fits in the org. Awareness of that type of vested interest can help filter internal champion input.

    There are others, or course, but I’m keeping this blog-length, and most–like MSPs or hosting providers–can be viewed as an extension of one of these (MSPs and hosting providers generally act like extensions of their chosen product’s sales and marketing, for example).

    And keep rocking it. All these people can help you understand how to make the environment better or your role easier. They can’t do it for you; that is your skill. Listen to what they all say and then act in the organization’s best interests. When I’m not a pundit, I tend to use marketing/crowd rating to get a feel for the space, then analysts and SEs to tell me about the space and specific products in it respectively. But figure out what works for your org and be aware of what viewpoints the various actors bring to your learning.

  • Cloud: Why Must We Be Confusing?

    Cloud: Why Must We Be Confusing?

    When I was a kid learning to play Dungeons & Dragons (D&D), the concept of level was never confusing—though the authors should have seen that it very well could be. For those unfamiliar, D&D has many uses of the word level—character level, caster level, spell level, dungeon level and, increasingly, as time went on, monster level. I can almost guarantee that I missed some uses of the word level in the game, but you get the idea.  In fact, if I missed your favorite, feel free to add a comment.

    We used context to determine what was meant, and we clipped along without any (game) world-shattering consequences. Though some people were horribly confused.

    (Side note: I worked with D&D co-creator Gary Gygax for a while and he knew about the over-use but didn’t feel that after D&D’s surge in popularity it could be fixed. His later RPG creations did seek more clarity and less word reuse, but most RPG systems available today still have many uses of the word level.)

    I am comfortable declaring that those of us who grew up on RPGs are now running vendor companies and doing analysis. Otherwise, why would we have so many uses for unique words? I mean, we no sooner got DevOps than we made a total mess about what, exactly, you meant when you said “CD”. Was it continuous deployment? Continuous delivery? Both? Similarly, we malformed continuous integration. Let’s call it CI—and then make an entire market around it really being continuous test while it is still used to refer to continuous integration, because that is not at all confusing.

    But then we jumped to cloud, and spent some time being really busy trying to confuse everyone about what “cloud” actually means. Is it only public cloud, or does it include private cloud? If private cloud, does that include virtual private cloud only, or does it include cloud in a co-host or data center? Is SaaS actually cloud, or is that a completely different beast?

    And that brings us to the reason I came here to write this particular blog post. We are now being barraged with “cloud” that includes Docker hosted on Kubernetes. I think of this as akin to one too many uses of the word “level”.

    Kubernetes is not cloud. It offers similar infrastructure in a smaller format, but the key to Kubernetes is that it supersedes cloud. Kubernetes doesn’t care about your cloud (or lack thereof) once it has been implemented. Cloud simply becomes infrastructure-as-a-service (IaaS) when Kubernetes is deployed. This is terribly important for a variety of reasons, not the least of which is that if you drop Kubernetes onto a cloud provider, you have two sets of infrastructure to lock down. Two sets that have a lot of internet exposure—because it’s not called “public cloud” for nothing.

    I do understand where referring to Docker hosted on Kubernetes as ‘cloud’ comes from; there are a ton of similarities. But Kubernetes needs a platform—hardware or virtual—to run on. And hand-waving the implications of that nested relationship is asking for trouble. And when cloud is either a thing of the past or so totally commoditized that people don’t think about it, Kubernetes or its successors will likely be the reason. So let’s take it easy re-using cloud too much.

    In the short term, though, my advice is that if someone in the industry mentions cloud in their product offering or analysis, ask which use of ‘level’ they mean. Because honestly, Kubernetes, if implemented on hardware or IaaS, can be picked up and moved to whereever it is needed. And that’s not “cloud”.

    Keep kicking rear. Doesn’t matter where your apps are running, it matters that you’re keeping them running and locked down. Keep it up, and call things what they are—container orchestrators are not cloud platforms, no matter which functionality they share. And to all my RPG peeps, keep having fun. There are always new adventures to be had… No matter the level.

    Image: Photo by S L on Unsplash.

  • AI: It’s What Staff Crave!

    AI: It’s What Staff Crave!

    If you’ve seen Idiocracy (Side note: I am not recommending the movie; I’m using a phrase from it we’ve all heard. The movie itself was a comedy not at all meant to be family-friendly when it was made, and changes in social mores since its 2006 release make it far less acceptable today), you are familiar with the title phrase I’ve used here. That’s what is repeated almost religiously to justify why they buy/use/drink Brawndo, an energy drink.

    One of the scenes involves people telling the star that plants need Brawndo—“It’s got electrolytes … That’s what plants crave!” This is repeated over and over until he asks, “What are electrolytes?” After some stuttering and failures to answer, someone says, “It’s what they make Brawndo out of.” Someone else inevitably tacks on, “It’s what plants crave.”

    Now, substitute “AI” for “Electrolytes”. That’s where we seem to be. Ask a vendor what algorithms they’re using, where their training data comes from, the difference in results between the test reservations and the real world. Most will end up saying a lot, not answering your questions and ending with, “It’s what staff crave!” or some such.

    A few companies will lay it all out there, assuming you can parse through the information and are familiar with the AI training algorithms they are using or the algorithms they’re using to classify inputs against the dataset. And these companies are grand because they (a) know what they’re actually doing beyond “It’s got AI/ML, it’s what staff crave,” and (b) Expect that you are knowledgeable about the data you’ve asked for or are capable of looking it up in this age of wonder that has boundless information at your fingertips.

    Don’t let your vendors get away with just repeating “It’s got electrolytes” over and over. AI and ML are a massive help in some areas, but they’re not yet a panacea and success rates vary wildly whether we’re talking problem domains, datasets, algorithms, training style, etc. Make them tell you the details. Where the data comes from and how big that dataset is. How much was reserved for testing and whether it was reserved randomly. Ask them what they hope AI will achieve, then ask them how that correlates to human interaction. Most AI today is still evaluating or replicating human interactions with something—most AI in IT particularly so. What algorithms were used to validate? And finally, make sure to ask for real-world results. I know people in data science and one has confidently said to me, “My models are 95% accurate.” When I finally dug into that claim (because my experience is that real-world use of AI/ML is almost never that accurate) it turned out that claim was true … for the reserved test data. So, the same dataset used to train got the same results on the reserved subset. That’s a good thing, but it is no indication of how said algorithm will do in the wild with unfiltered data. The big problem really is the switch from test data to real-world data.

    In fact, in IT, we are a little better off than most spaces wrestling with AI/ML, because very often there is no difference between test and training data in IT. A network security vendor will test against actual traffic—because they have access to massive volumes of it and it shortens the iterations to use what’s at hand and what the system is being trained for.

    And keep rocking it. The current iteration of IT is the opposite of the dark comedy future depicted in Idiocracy. You all are putting up systems and keeping them running at increasingly fast cadences; sometimes remotely because of COVID-19 or other work-related issues. Don’t stop turning out success for your coworkers and customers and take a moment to force vendors to explain what they’re doing with AI. If you’re a generalist like me, ask over email, though, so you can go look up the answers and make sure you understand the details.

  • AppSec Marketing in the Age of DevSecOps

    AppSec Marketing in the Age of DevSecOps

    A while back, I had a conversation with a friend I went to school with (currently a senior member of the engineering team at a large retail chain) who was tasked with the job of identifying potential application security partners (he addressed vendors as partners, which I personally liked) to collaborate with on various areas as part of their product security initiative. The following piece emerged as an extension of my immediate thoughts when he shared his views of what could have made his experience of interacting with front-line sales and marketing folks better.

    In the context of DevSecOps, much has been said about the need for engineering to speak security, security to speak code, DevOps to speak security, etc. But as a technology service provider (TSP) riding the current wave of application security, it’s almost mandatory for the sales and marketing teams to also speak relevant tech!

    Application Security Is Not One-Size-Fits-All

    Application security, as a practice area, is dynamic. No two applications are the same, even if they belong in the same market domain, presumably operating on identical business use cases. Some (of the many) factors that cause this variance include technology stack of choice, the programming style of developers, the culture of the product engineering team, priority of the business, platforms used etc. This, consequently, results in a wide spectrum of unique customer needs.

    Take penetration testing as an example. This is a practice area that is, presumably, well-entrenched both as a need and as an offering in the application security market. However, in today’s age, even a singular requirement such as this could make or break an initial conversation. While for one prospect, the need could be to conduct the test from a compliance-only perspective, another’s need could stem from a proactive software security initiative. There are many others who have internal assessment teams and often look outside for a third-party view. Others who are further along the maturity curve could be looking to up their game through a hybrid approach of tool automation with a complementary method of manual assessments. I’m not even considering the added complexity involved in the nomenclature of such a service—is it called penetration testing, security testing, vulnerability testing, VAPT (which actually is a combination of two independent practices) etc.?

    Each of these unique needs emerges from buyer personas which emerge from varying degrees of informed decision making. TSP’s would need to retrofit their positioning accordingly. They often run the risk of underwhelming a mature buyer or overwhelming an early practitioner, especially in high variance offerings such as security tooling, security regression and threat modeling, for example. While some might argue that losing an overwhelmed prospect could be the result of their accurate customer segmentation, there are other reasons for this.

    Scoping questions, such as the ones below, can significantly help technology marketers strike the right chord with their prospects and elevate the experience of the initial interaction.

    • What is the motivation for the penetration test? Is it compliance regulation, internal validation, business drivers, their customers’ needs, etc.?
    • What are they specifically looking from a third-party partner? Is it external certification, a specialized approach, uncovering logic flaws, etc.?
    • What is the current appetite (measured in resource bandwidth, commerce) to take on your advanced offering? (Such as automation, regression etc.?)
    • How security aware are the developers? Can they take the findings to their logical conclusion through successful remediation?

    DevSecOps Is About the Journey, Not the Destination

    Ever since the surge of DevSecOps, marketers and practitioners have been vocal about the possibilities and advantages that smart automation brings with it. Think tanks, too, have statistically alluded to its benefits in terms of cost savings and bandwidth efficiency, among others. Though recent marketing campaigns have rather effectively communicated the ‘what of DevSecOps and AppSec automation, more awareness of the ‘how’ of DevSecOps is needed. TSP marketers need to design and propagate content on use cases focusing on the implementation challenges and suggested how-tos. Such content not only helps build trust and credibility but also allows segues for tech marketing to collaborate with security engineering. Some of these include practical guides on open source tool automation and sample automation scripts and libraries, data sheets on resource optimization through automation and handbooks on vulnerability remediation, just to name a few.

    This collaboration between marketing and sales and security would provide an opportunity for the former to get themselves well entrenched in the practical workings of the service or solution that they are responsible for positioning. Ironically, this also allows them to appreciate constraints that would prevent them from over- or under-committing business value to their prospects through their messaging. This is especially more relevant with the numerous myths that surround application automation and DevSecOps in general.

    The DevSecOps Rolodex

    In 2012, I had the opportunity to meet with one of the senior CISOs in the industry. After some initial small talk, I was introducing what we did and how we thought we could help his team. I was 70 seconds into what was my planned 180-second pitch when he respectfully stopped me, pulled out a rather impressive Rolodex from his desk and said, “I could point you to 15 companies in a 20-mile radius who could help me with exactly what you’ve offered me. I wonder if there’s any secret sauce?”

    Startled, embarrassed, I managed to gather my thoughts and moved to the final 30 seconds of the pitch, though with much hesitation. As luck would have it, he found little bits of the secret sauce. The meeting obviously did not go exactly as I had planned, but it didn’t go badly, either. However, it made me realize that our customers and prospects often know just as much—or even more—about our competition than we do. Everybody is selling, all the time. So, someone else has already made their 70-second pitch. Not everyone gets lucky enough to be given an opportunity for a pause! It’s up to us to find the secret sauce and make that close in the final 30 seconds.

    We are riding a very healthy wave of application security focus right now, and it’s paramount that technologists and marketers collaborate to identify and nurture their own secret sauce in their messaging and positioning. After all, this is what is going to keep the person at the other end of the table from reaching out to others in their DevSecOps Rolodex!

  • 6 Examples of Digital Transformation at Adobe Summit Keynote

    6 Examples of Digital Transformation at Adobe Summit Keynote

    We’re attending Adobe Summit 2019 to research the intersection of DevOps and marketing. Follow along for more stories.

    In a recent article, we described how DevOps is transforming retail from brick and mortar into an omnichannel “brick and click.” At Adobe Summit, we garnered more insights, discovering how other institutions are implementing an innovative convergence of physical and digital spaces.

    The result is impacting all sectors, creating new hybrid environments within home tech, banking, apparel, and more. Let’s see which ones Adobe decided to highlight in its opening keynote to discover how companies of all types are reinventing themselves through digital transformation.

    Best Buy: Evolving 1 Storefront into 3 Services

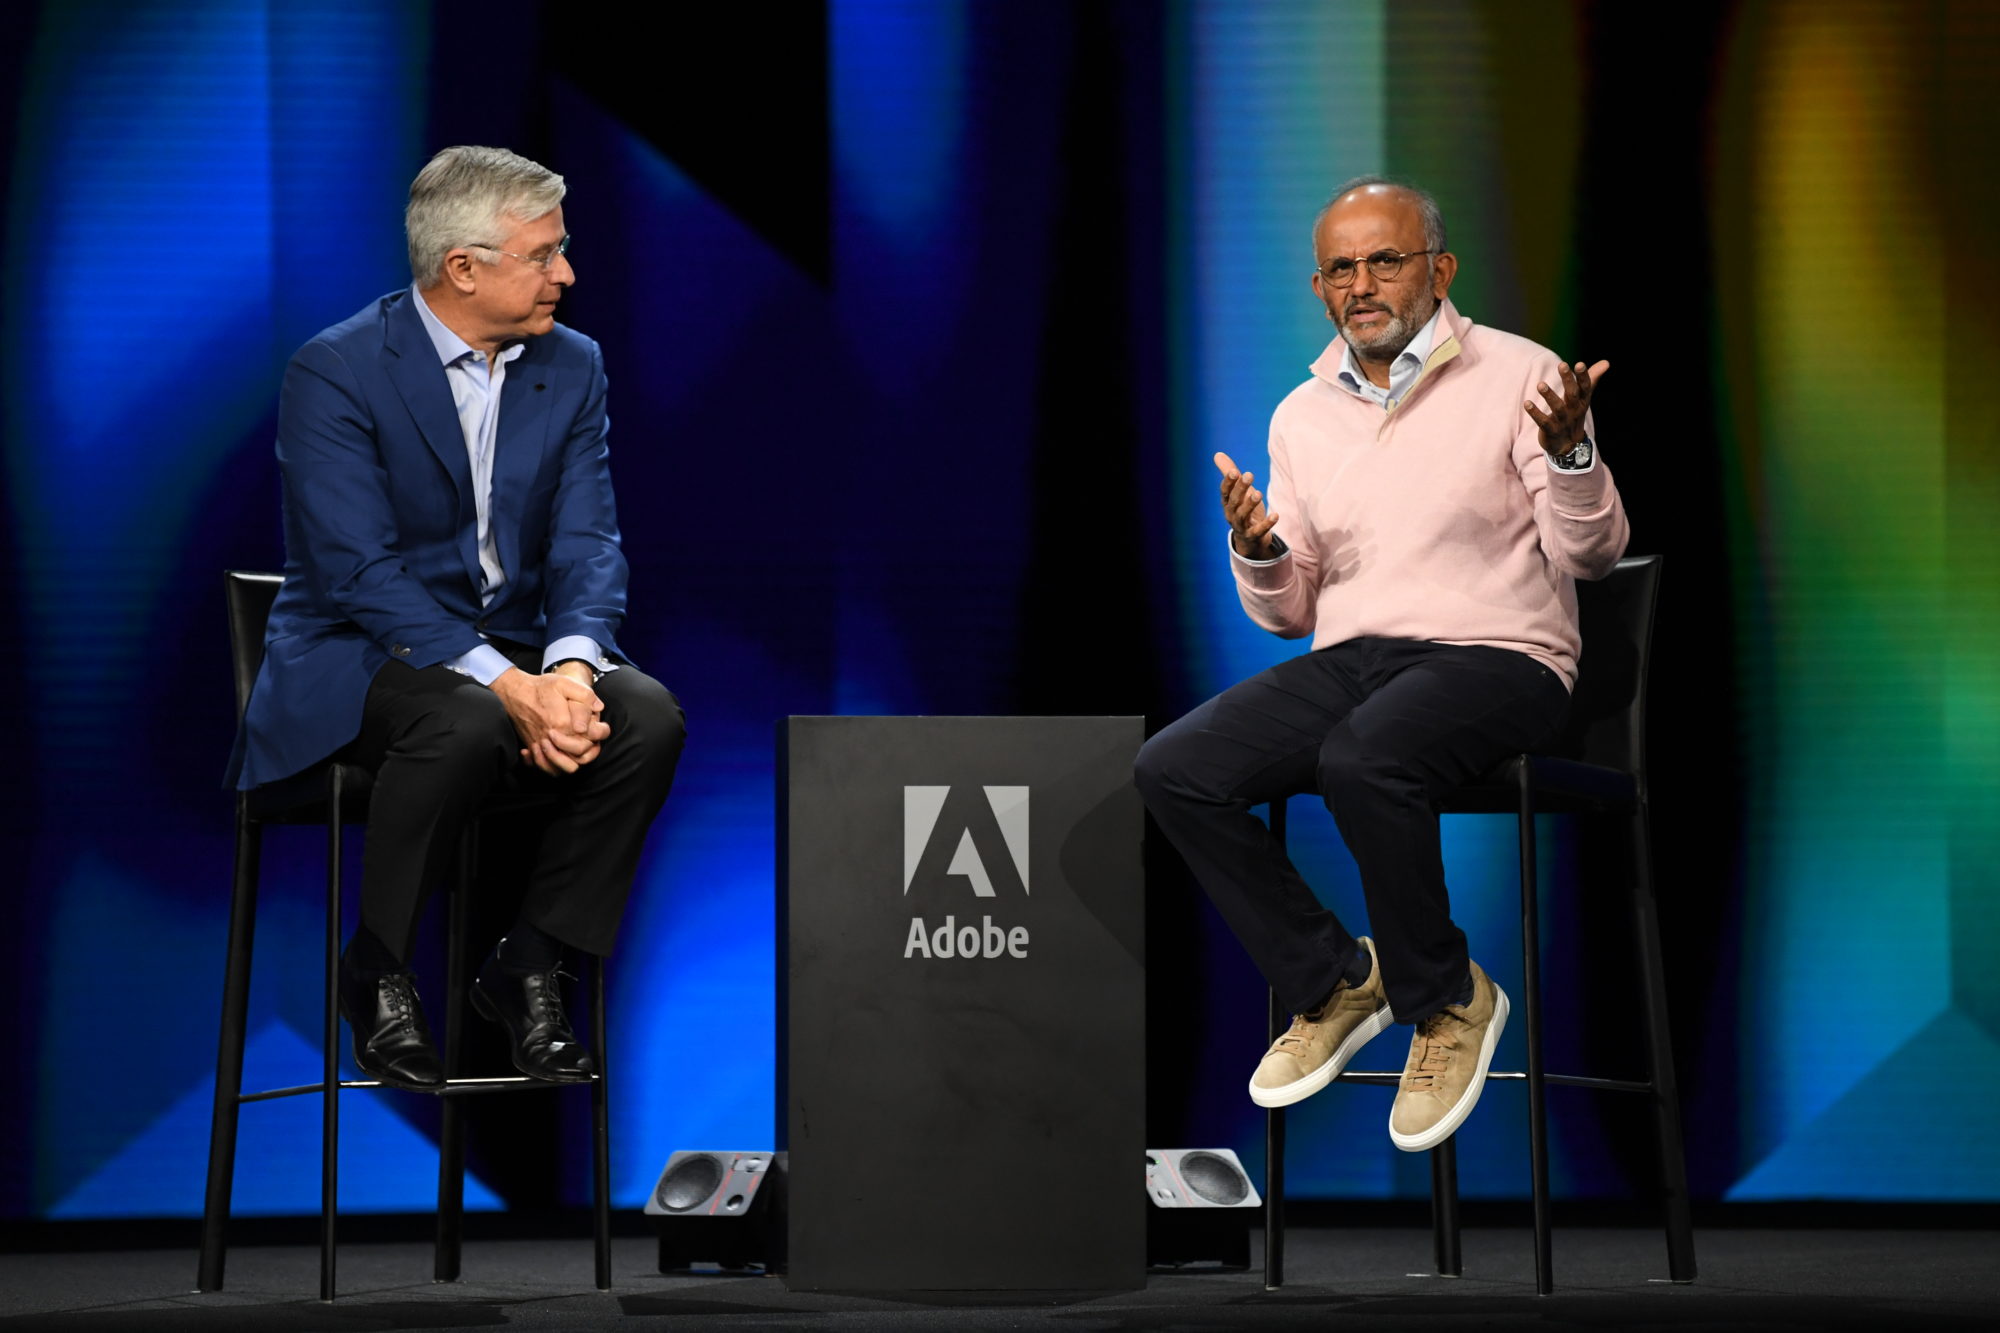
    Best Buy is a prime example of digital transformation for retail. At Adobe Summit, Best Buy CEO Hubert Joly described how the company is reinventing the “New Blue” to enrich lives with the help of technology; a sense of purpose is a mobilizing factor that affects innovation.

    For $200 a year, Best Buy in-home advisers will be your No. 1 on-call tech support. The company is also using AI to monitor seniors to trigger assistance when they are in need. Lastly, an app that compares features is bringing new in-store customer experiences.

    Not solely a brick-and-mortar retail anymore, Best Buy is transforming with subscription services and online presences, bringing in multiple new touch points to stay competitive with eCommerce.

    Best Buy CEO Hubert Joly sits down with Adobe CEO Shantanu Narayen March 26 in Las Vegas. (Jeff Bottari/AP Images for Adobe)

    Intuit: Reinventing the SaaS Platform Model

    Atticus Tysen, SVP & CIO at Intuit, described, how, over the years, Intuit has transformed its platform-based SaaS offering. Intuit is now utilizing ML and AI to improve its customer experience process. Doing so requires great data, as well as powerful data structures. As Atticus mentioned: “It all comes back to data…You need to monitor your data pipelines just like you monitor your offerings.”

    According to Atticus, a core component of curating data infrastructure is democratizing it. Opening such data to all employees dismantles silos to increase the speed of IT. It’s this sort of horizontal thinking that fosters the collaboration digital transformation requires.

    Atticus Tysen, SVP & CIO at Intuit talks with Cynthia Stoddard, SVP & CIO at Adobe, March 26 in Las Vegas. (Jeff Bottari/AP Images for Adobe)

    Zumiez: New Zero-Code Methods to Build Online Shopping

    Jennifer Small presented how the newly Adobe-owned Magento can be utilized to build and personalize shopping experiences. She walked through a theoretical Zumiez implementation, demonstrating how to make visual edits to develop cross-channel retail applications.

    With the rise of eCommerce, traditional retailers such as Zumiez must create lean digital spaces to interact with end users. Not only must such environments be agile, but every point along the customer journey also must be individually personalized.

    Online presences are adopting new tools such as AI-driven photo search, mobile A/B testing, user-driven optimization, responsive layouts, instant purchase and more. It’s only with the use of innovative tech that traditional retailers can stay relevant in a competitive landscape.

    Foot Locker: AR-Driven Demo

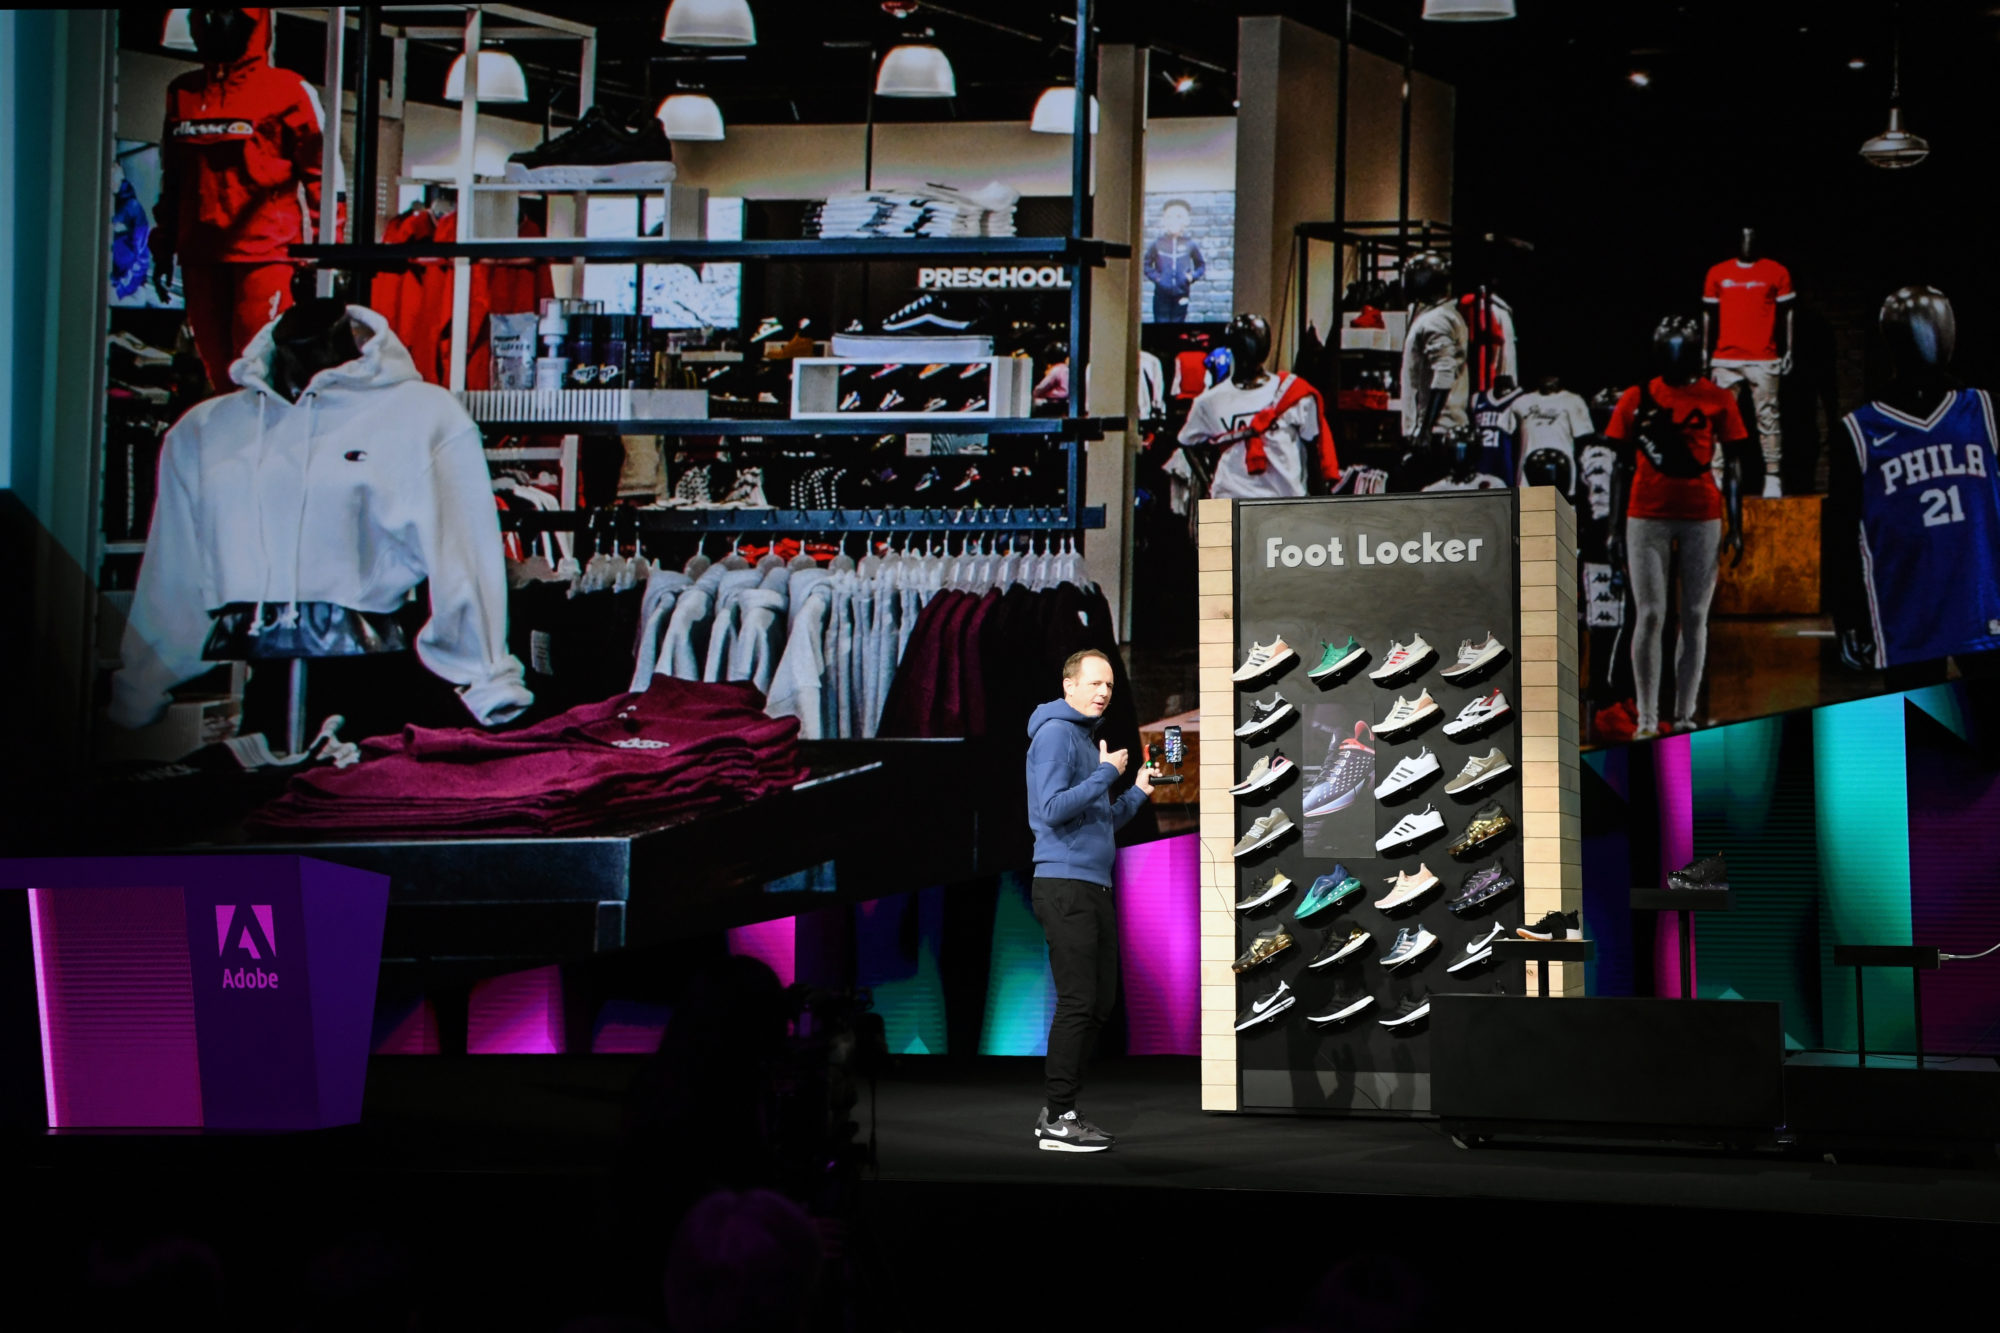
    David Nuescheler, Adobe Fellow & VP of Enterprise Technology at Adobe Systems, has been working hard in the lab using Adobe Sensei AI to take physical retail to new heights. In his demo featuring Foot Locker products, he painted an augmented reality that may be closer than we think for storefronts.

    Using a catalog of cloud-aware assets, David demonstrated how a storefront could render innovative user-facing views in real-time. Using AR, his live demo rendered a custom shoe to appear on an empty shelf. He scanned and identified shoes on a product stand, and overlaid warehouse inventories on top of products in real-time.

    Though demonstrated as a futuristic work-in-progress, such AR-infused digital experiences will likely arise in retail soon, adding a sense of magic to typical storefronts.

    David Nuescheler, Adobe Fellow & VP of Enterprise Technology at Adobe, demonstrates some cool storefront AR March 26 in Las Vegas. (Jeff Bottari/AP Images for Adobe)

    Chegg: From Textbooks to Online Tutoring

    Textbook rental and academic platform Chegg also made an appearance at the Adobe Summit keynote. Chegg CEO Dan Rosensweig detailed the company’s initial fear when its IPO plummeted, and the frantic reorganization that followed. If any digital transformation story has a positive end in sight, it’s Chegg.

    Now valued at $4.5 billion, Chegg was pressured to make a complete 180-degree pivot from shipping textbooks to embracing online subscription-based services. Though the company still ships about 5 million books a year, Chegg now has 1 million digital users. Academics from high school through to continuing education are leveraging Chegg’s tutoring and online study communities.

    Chegg is deeply tapped into its consumer base, placing great emphasis on responding to “who [the customer] is, and not who they used to be.” For Chegg, using consumer analytics to architect the new digital business is a continuous, and necessary, commitment.

    Chegg CEO Dan Rosensweig discusses with Adobe CEO Shantanu Narayen March 26 in Las Vegas. (Jeff Bottari/AP Images for Adobe)

    Adobe: An Integrated, Impressive Services Catalog

    A sure-fire case study in digital transformation is Adobe itself. Adobe CEO Shantanu Narayen kicked off the Adobe Summit 2019, its annual conference full of 17,000 tech-leaning CMOs and digital transformers in attendance.

    Shantanu transparently outlined how, years ago, innovation in the Adobe product line had become stagnant. Compared to the infinite growth of content creation across the world, its static products weren’t doing the trick. This began to change rapidly with the introduction of subscription-based formats including Creative Cloud. Again, Adobe had found a foothold.

    He demonstrated the company’s new Adobe Experience Platform, a holistic customer experience management platform. With many of the tools having been used as dog food at Adobe itself, the platform unites a large suite of applications dedicated to advancing the customer journey.

    Discover, Try, Buy, Use, Renew

    Discover, Try, Buy, Use, Renew. Adobe’s creed for customer experience management was reiterated many times at the Summit’s keynote. Such insights ring true in the agile transformation tactics taken by the businesses showcased above.

    Adobe Summit—or, as Marketo’s Steve Lucas calls it, “the Woodstock of marketing”—showcased how successful agile companies placed customer experience as the driver for product design. In tandem, the future of retail holds an interesting future that meshes both traditional physical and digital experiences.

    With customer experience now the No. 1 driver, should we place a “Mar” in front of the DevOps to create the triumvirate MarDevOps? The dogs are out.

    — Bill Doerrfeld

  • To Be Continuous Podcast: Category Creation featuring Martin Casado

    To Be Continuous Podcast: Category Creation featuring Martin Casado

    In this episode of “To Be Continuous,” Paul and Edith are joined by Martin Casado, General Partner at Andreessen Horowitz. He previously was co-founder and chief technology officer at Nicira, which was acquired by VMware in 2012. While at VMware, Martin served as senior vice president and general manager of the Networking and Security Business Unit.

    The group discusses the deeply complicated and difficult process of category creation, with a special focus on technology infrastructure products.

    This podcast is brought to you by Heavybit, a program that helps developer-focused companies take their product to market.

    [soundcloud url=”https://api.soundcloud.com/tracks/283115632?secret_token=s-zX7AW” params=”auto_play=false&hide_related=false&show_comments=true&show_user=true&show_reposts=false&visual=false” width=”100%” height=”166″ iframe=”true” /]


    Edith Harbaugh: What do you like about continuous delivery?

    Martin Casado: I think that there’s a broader movement around continuous delivery that is really interesting, which is, traditionally, infrastructure and operations came from an independent group. My first job out of undergraduate was working on simulations code in a national lab.

    I couldn’t control anything about infrastructure. I really didn’t have budget to buy a pencil. You get infrastructure, and you’d have some application to code, and you’d work on that application. We’d fiddle around with our MIG files or whatever, and that was pretty much it.

    The cool thing about the broad movement now, and I think CI/CD (continuous improvement/continuous delivery) is just part of this, is more and more applications, application developers, are actually getting responsibility for operations.

    This is provisioning, this is delivery, this is deployment. That’s a big huge change in not only what technologies get created but who’s consuming it and why they’re consuming it. I think it’s actually one of the more interesting trends right now.

    Edith: This would be a great time for you to introduce yourself.

    Martin: My name is Martin Casado, and I’m a general partner at Andreessen Horowitz.

    Edith: But you did stuff before you were at Andreessen.

    Martin: That’s right. The quick arc, as I mentioned, I used to be a research scientist at Lawrence Livermore National Labs. I spun out of that, did my PhD at Stanford. My research was in networking, so I was part of the team that started software-defined networking.

    I was there for four years, spun out of that, started a company called Nicira where we did software-defined networking. I did that for five years. That was acquired by VMware. I ran the networking security business unit at VMware for almost four years, and four months ago I decided to change and become a VC.

    Edith: So you basically created a category. What drove you to do that? What made you decide to start something knowing that it was so hard?

    Paul Biggar: You’re talking about software-defined networking? For the viewers at home, Martin roughly invented software-defined networking.

    Martin: There’s a whole bunch of people contributing, but I think a lot of the original momentum came from my thesis. You know, I’m going to be totally honest. If I had any idea how hard it was, I never would’ve done it.

    Edith: Really?

    Martin: I think so.

    Edith: I think you would’ve.

    Martin: Well, maybe. But it would’ve been a lot more daunting. I came out of Stanford pretty darn naive, like, “This is going to be easy!” Now, nine years and tons of gray hair later, I just realized that, man, it was a battle. I don’t think I had one-quarter that was easy. Everything was a battle.

    This is the way that I think about it. If you’re an entrepreneur, and you’re going to do category creation, you basically just have two jobs, in addition to product development. And job No. 1 is, there’s going to be some constituency out there you’re selling to, and that constituency, they wake up every morning and they think about all sorts of stuff, but they’re not thinking about your thing, because it hasn’t been created yet.

    That object in the mind space, that object doesn’t even exist in their brains yet. The first thing you have to do is create that object. It’s like Leonardo DiCaprio at “Inception.” You go in, you’re planting an idea in somebody’s head. It has to become a thing, something people think about, something people know and integrate.

    This is from nothing, and that’s hard. For us, it took five-plus years, and it touches every aspect of thought leadership such as analyst relations and technical conferences and broad marketing.

    Paul: So the activities that you’re doing in that category creation are largely marketing and getting people to hear about the activity and learn about it?

    Martin: I think so. I think maybe technologists will view marketing as this pretty shallow thing, but I think you’re exactly right. It’s marketing. But it is often very technical marketing, for example, in the guise of open source.

    In releasing open-source projects, you’re getting people to use it, you’re going to standards bodies, you’re going to conferences. It’s an incredibly technical thing, but in the end, it’s marketing in the sense that you’re actually creating awareness and a market.

    The first thing that you’ve got to do as an entrepreneur is, if you’re doing category creation, nobody’s thinking about your thing. You’ve got to get them to think about your thing, which is a lot of work. In my experience, five to seven years.

    Then the second thing that you have to do, which is just as much work, is then you have to attach a value to that thing. And I think we as technologists, there’s this kind of fallacy that we have where, “I’m going to create this new widget.” Let’s say I create the iPhone.

    Paul: Everyone will know how amazing it’s going to be.

    Martin: Exactly.

    Paul: Just build it and they will come.

    Martin: Yeah, there’s intrinsic value in my widgets. I take my widget, I put it on a sidewalk and someone picks it up. They’re like, “This is amazing. It’s worth millions of dollars!” And that’s totally not the reality.

    The reality is people only see value if they exchange money and they’ve used it.

    And if you’re doing category creation, how do people know what that value is? It’s a very difficult thing.

    Paul: And when you say attaching value, do you mean monetizing? Or is there more to it than that?

    Martin: I meant more the idea. Ultimately, this materializes monetization. Let’s say that you’re my constituency, and I’ve created this new widget. First I need to get you to think that this is actually a real thing. I’m going to call it a new phone. So, you need this new phone. First I need to convince you that you need the new phone.

    Then the second thing I need to convince you is it’s worth tens of thousands of dollars to you because you need to mentally actually attach that value to it. And it turns out introducing new concepts don’t necessarily have value if they’re new concepts.

    Normally, the value comes from, for example, an actual transaction. There’s a psychology around this. Or at least some experience with it, knowing that it’s going to, I don’t think you can just sit back to a couch experiment and be like, “Oh, I think this is going to save me money, therefore it’s worth something.” It really requires a lot of effort to make value.

    Paul: So the category that I see being created, or the one that’s closest to me at least, is this idea of containers and Docker, and more specifically Kubernetes, the idea that there’s this cloud infrastructure over there. The way that I became aware of it is exactly the way you’re talking about it. There’s open source coming out there that you can use and you can hack on yourself. There’s talks up there where people blow your mind.

    Martin: I think that actually this point, and certainly for all the listeners, I think this is one of the most salient points of this decade, actually, which is going to be a weird thing to say. At least an infrastructure’s the following.

    In the past, how did we create mindshare and customer bases? Well, there’s this whole pmm function and this whole sales function. And if you look at the big enterprise companies, if you look at Cisco and IBM and Oracle, really their power is this function. They own the sales channel.

    They have great relationships with the analysts, they’ve got great relationships with the customers, they’ve got certifications and the classes. So anytime they have a new concept, they take that concept and they cram it down the machine.

    As a startup, it doesn’t matter how cool your technology is, the hardest thing is to actually penetrate that channel.

    But when it comes to this new era of open source, now you actually have this hack that’s never existed before, where the buyer is shifting from an operator to a developer. Developers like open source, and you can actually create these concepts by getting open source out there and getting them to use it.

    Paul: We’ve been talking about this sort of thing, just the idea that it’s bottom-up now versus top-down.

    Martin: Not only that, it’s a totally different buyer that’s a totally different aesthetic. I don’t think developers care as much about analysts. I don’t think developers care as much about the 42-long sales dude with white teeth and the boat. I don’t think developers care as much.

    Paul: They won’t even answer his call.

    Martin: Exactly. About the channel, I think they don’t care about complex procurement processes.

    Edith: Having sold software for a little bit myself, if you get into a bigger corporation, you still don’t start to run into that.

    Paul: You get there, because the developers were first asking for it to exist.

    Edith: The longest part of our sale cycle is you get bounced to procurement and legal.

    Martin: Absolutely. I think this is the most important nuance of this argument, is exactly what you said. I’ve always maintained that open source and the developer is replacing marketing and pre-sales, not sales.

    You get credibility to the account, you can get things to technical close and technical validation, you can get account pull. So it’s almost like filling the pipeline, getting the transaction done, I still believe. For a long time, you need to have a professional, direct sales force that will be in there pushing things for procurement.

    Edith: It’s just a lot of work, because you pass the technical evaluation. They’re like, “Okay, go talk to procurement.” And to procurement, you’re a widget.

    Martin: Right, but the good news is, now it’s possible. Where in the past, to get that much legitimacy, to get things to technical close, was very difficult. You didn’t have the certification, you didn’t have access to the buyer, you didn’t have the account rep to make the introduction. You didn’t have any of that.

    Edith: That’s true.

    Martin: And now you do, and now it’s just about actually going through the logistics. And you’re absolutely right, it’s hard, it’s baroque. I’ve called it tribal bloodletting. It’s all of that, but you can do it as a startup.

    Paul: The thing that I think is really interesting is the converse of that. It’s that people who work in open source now are becoming actually incredible marketers. They don’t refer to themselves as such, but they have amazing social media presence.They build up tons of channels, whether it’s mailing lists or just Twitter followers.

    Edith: It’s like everybody recreates marketing. Everybody’s like, “Oh, we don’t need marketing.” Then you’re like, “Well, what is this thing over here where you have an email list?” Oh, that’s not marketing.

    Paul: It’s not marketing because I’m a developer.

    Martin: I really think that those that know how to do this are some of the most valuable people in the entire industry because this is the new entree for products into customer bases. I mean, there’s another kind of potential pitfall here, which is, let’s say you’re using open source for marketing.

    Now, there’s probably $7 billion have been invested in open-source companies and only about a $1 billion worth of returns. I’m not sure if those numbers are true, but I hear them quoted all of the time. But the reality is, a lot of money’s gone into it and not a lot of money has come back.

    The reason is because now, if you’re using open source to do marketing, you’re almost cannibalizing your sales motion. And so for a long time, the only open-source model we knew how to work was the Red Hat model, which is a services company. Only Red Hat’s ever pulled it off. It’s been very difficult.

    But another shift has happened in the last few years is people have figured out that actually you can use open source for marketing, but you don’t have to confuse that with your actual product offering.

    And with the rise of services, you can actually use open source for customer traction. You can monetize the service, and when it comes to services, no discussion of open source or closed source. So I think that we’re actually starting to unlock viable business models where you use open source for marketing.

    Edith: Who do you think does a good job of that?

    Martin: I think GitHub is a great example, right? Git isn’t even built by GitHub. It’s the standard in Linux. But if you look at GitHub, it’s a very fast-growing company that’s based on open source, and so everybody knows about it because of Git. So Git is doing the marketing. And this is just one example, I think there are many.

    Paul: It’s funny that you cite that as based in open source, because almost none of their stack is actually open source.

    Martin: Exactly, it’s a service offering. That’s what I’m saying.

    Paul: When you say service, you’re referring to software as a service, not service as in consulting?

    Martin: Absolutely. I should’ve been more clear. The long-standing question for us, certainly since 1995, is how do you build an open-source company that has the margins of a closed-source software company? Because you’re open source, basically you become a service and support company.

    What has happened in the last decade is exactly what you’re saying: people will realize that you can get account credibility and account traction, account knowledge, through open source.But then you can offer a back-end service offering as a service offering, and monetize that, and it’s often a closed-source stack on the back end of what you’re doing.

    But you don’t talk about open source/closed source as much with service offerings. It’s normally if you’re consuming something on-prem that you think about those things.

    Paul: How do you feel about this? People who are building, let’s say CircleCI as a good model, but there’s a ton of them. Building something that’s a SaaS product, a hosted SaaS product, but that then sells to people who use it in their own VPC and pseudo on-prem sort of thing.

    Edith: Oh gosh.

    Martin: I come from this somewhat traditional world of selling enterprise software. In there, there’s this whole discussion, and I was part of this discussion, of is it on-prem or is it off-prem in general? And I think that you framed this question perfectly. I’ve realized that that’s a false dichotomy. It’s actually not the right question to ask. I think as a service, is it actually an operational model and a delivery model? It doesn’t really matter if it’s on-prem or if it’s off-prem.

    I think that the days of selling closed-source software to companies is done.

    But you can sell them services and you actually can sell them appliances. But if you look at appliances, appliances almost look like services. They’re boxes that have services, and often the upgrade is happening remotely, management is happening remotely.

    I do think that the right model for these companies, I think CircleCI’s a great example of this, you have open source that customers use, you have a SaaS offering, but you also have an on-prem delivery offering as long as you don’t change the operating model, as long as it still looks like a SaaS model somehow, whether it’s a managed service or something like that.

    I think as soon as it becomes shippable software, where you have to manage a heterogeneous set of environments, you have to manage all the day-two ops. It becomes unwieldy.

    Edith: I had a really interesting discussion the other day with the VP of Sales from CircleCI and somebody from Microsoft. CircleCI was basically like, “We love that it’s selling on-prem. It’s helping you.” Microsoft is like, “We’re trying to get off-prem desperately.” So it was not the argument you thought was going to happen.

    Paul: I think it’s probably because of how sensitive the IP is. If you’re talking about something like, well, documents are pretty sensitive, but the source code is very sensitive. And so people are not as happy to ship that off-prem as we once thought was going to be the case.

    Edith: Microsoft’s reasoning was, and this might be the way Microsoft had done it, is they have 10-year maintenance agreements.

    Martin: We have, “If you have a problem, upgrade to the latest version and then we’ll deal with you.” I think that’s kind of what everyone has. There used to be this idea that you’d create a fork and then you’d backport things to that fork or the old version, or something like that.

    I don’t know anyone who’s doing this sort of services, the SaaS with a managed to on-prem version that does anything but “the latest version is the version.”

    This podcast is brought to you by Heavybit, a program that helps developer-focused companies take their product to market. Throughout the program, founders work on developer traction, product market fit and customer development. If you like what you hear, be sure to subscribe to Heavybit’s Podcast Network on iTunes.

    — Malia Powers