Category: DevOps Toolbox

  • AWS Aligns With Slack to Foster Dev Team Collaboration

    AWS Aligns With Slack to Foster Dev Team Collaboration

    Amazon Web Services (AWS) and Slack Technologies have formed an alliance through which they are moving to transform the way development teams collaborate.

    Under the terms of the multi-year agreement, Slack will migrate voice and video calls to the Amazon Chime real-time communications service.

    In addition, AWS and Slack are integrating Amazon AppFlow integration with Slack, which enables data to be transferred securely between Slack and AWS services such as Amazon Simple Storage Service (Amazon S3) and Amazon Redshift. The two companies are also promising to make it possible to transfer data bi-directionally between multiple Slack channels and AWS services in a single flow.

    AWS and Slack have also integrated the AWS Key Management Service with Slack Enterprise Key Management (EKM) to distribute and control cryptographic keys. That capability builds on an instance of EKM for Slack’s Workflow Builder automation tool that was released last month.

    Finally, the two companies are committing to make the AWS Chatbot service accessible from directly within Slack.

    Slack, which already makes extensive use of the AWS cloud, has emerged as a de facto collaboration tool within many organizations that have embraced best DevOps practices. Eron Kelly, head of product marketing for AWS, said this alliance will make it easier for development teams to employ a wide range of communications tools at scale.

    Many DevOps teams already rely on Slack Calls to launch video and voice calls whenever a subject being discussed using text messages requires a deeper level of interaction. As reliance on Slack Calls increases, the software development kit (SDK) for the AWS Chime service that Slack will invoke will ensure the quality of the video and voice calls, said Kelly.

    In many ways, DevOps processes revolve around a mix of asynchronous and synchronous communications. The challenge has been to find a way to enable DevOps teams to use those tools in a way that enhances rather than detracts from productivity. Managing multiple Slack communications channels can easily become overwhelming, especially if developers are working on multiple projects at the same time.

    Ideally, DevOps teams will eventually become more adept at determining, for example, what messages, such as status updates, are best delivered asynchronously versus urgent requests that need to be made via a communications medium such as Slack.

    In the meantime, the COVID-19 pandemic has clearly increased reliance on communications services delivered via the cloud. With most members of DevOps teams working from home, tools such as Slack have become a virtual substitute for walking over to the next cube in an office to resolve an issue. Once development teams return to the office, it will be interesting to see to what degree tools such as Slack have become the default means of communication, even with fellow employees who may be only a few feet away. In fact, such tools may play a critical role in helping organizations adhere to social distancing policies even after employees return to the office.

    As philosopher Marshall McLuhan once observed, the medium is the message. Today, however, those messages increasingly are being delivered within a stream of real-time communications that is becoming more challenging to manage.

  • Appian Infuses Low-Code Platform With AI

    Appian Infuses Low-Code Platform With AI

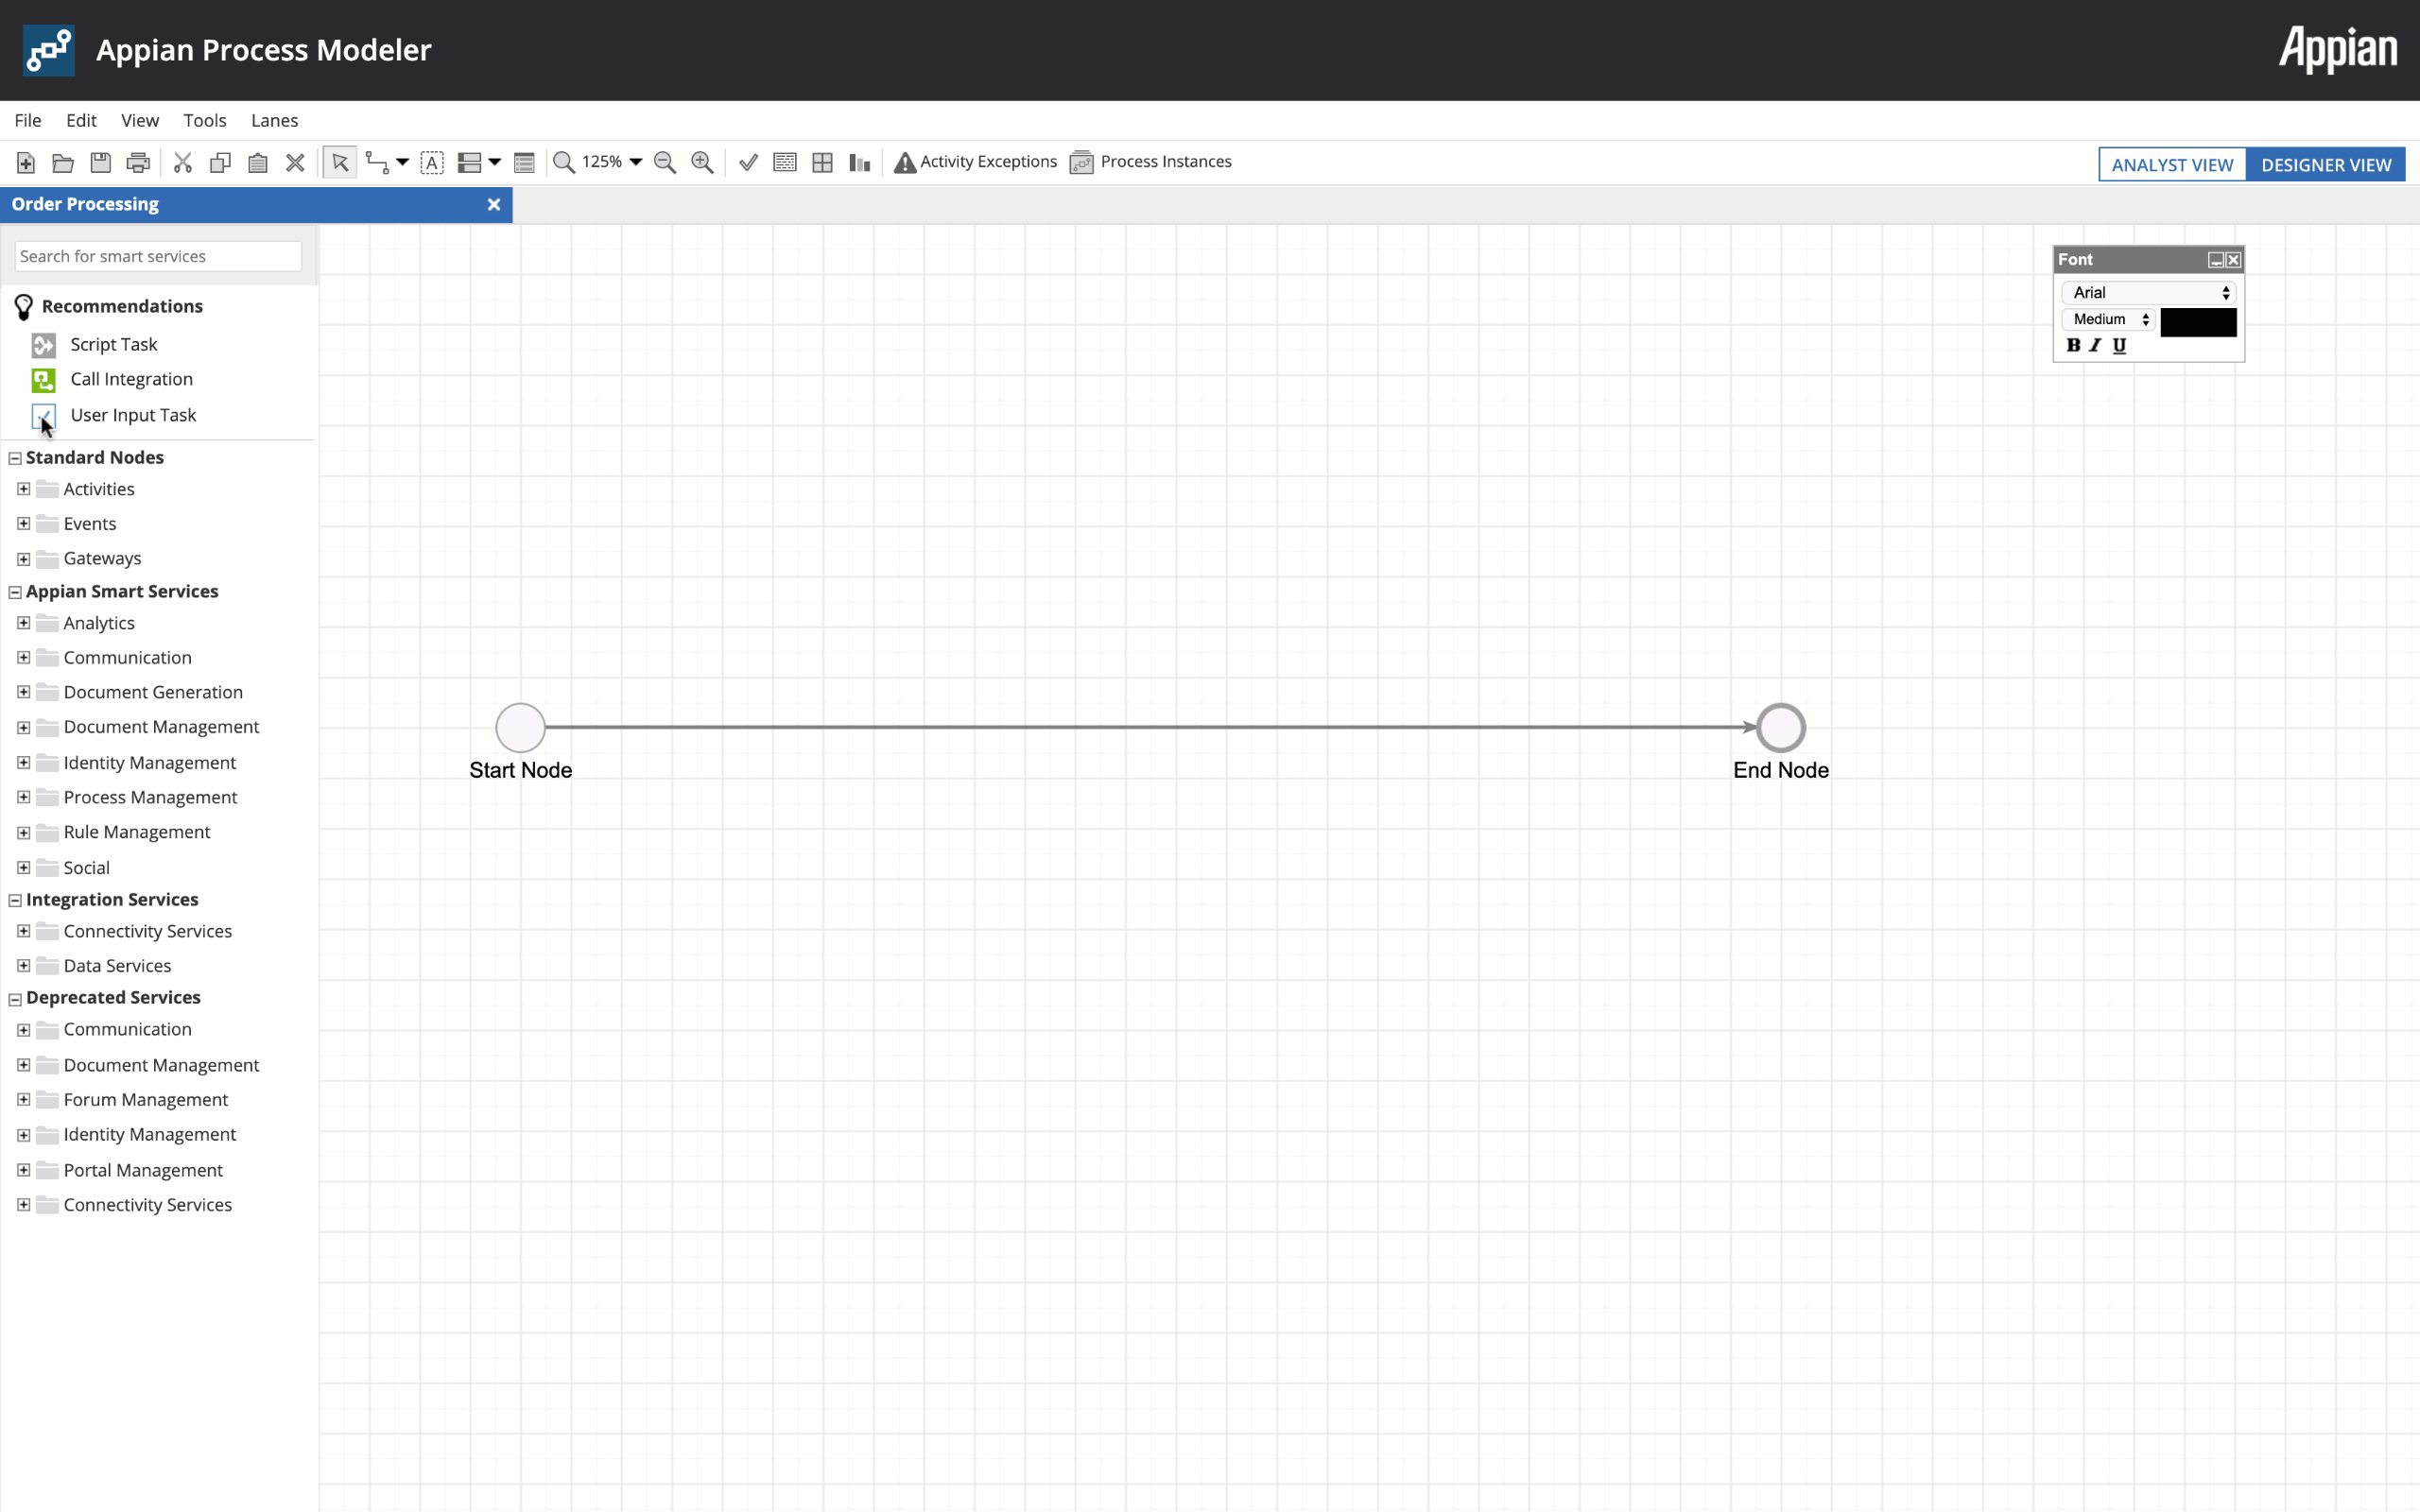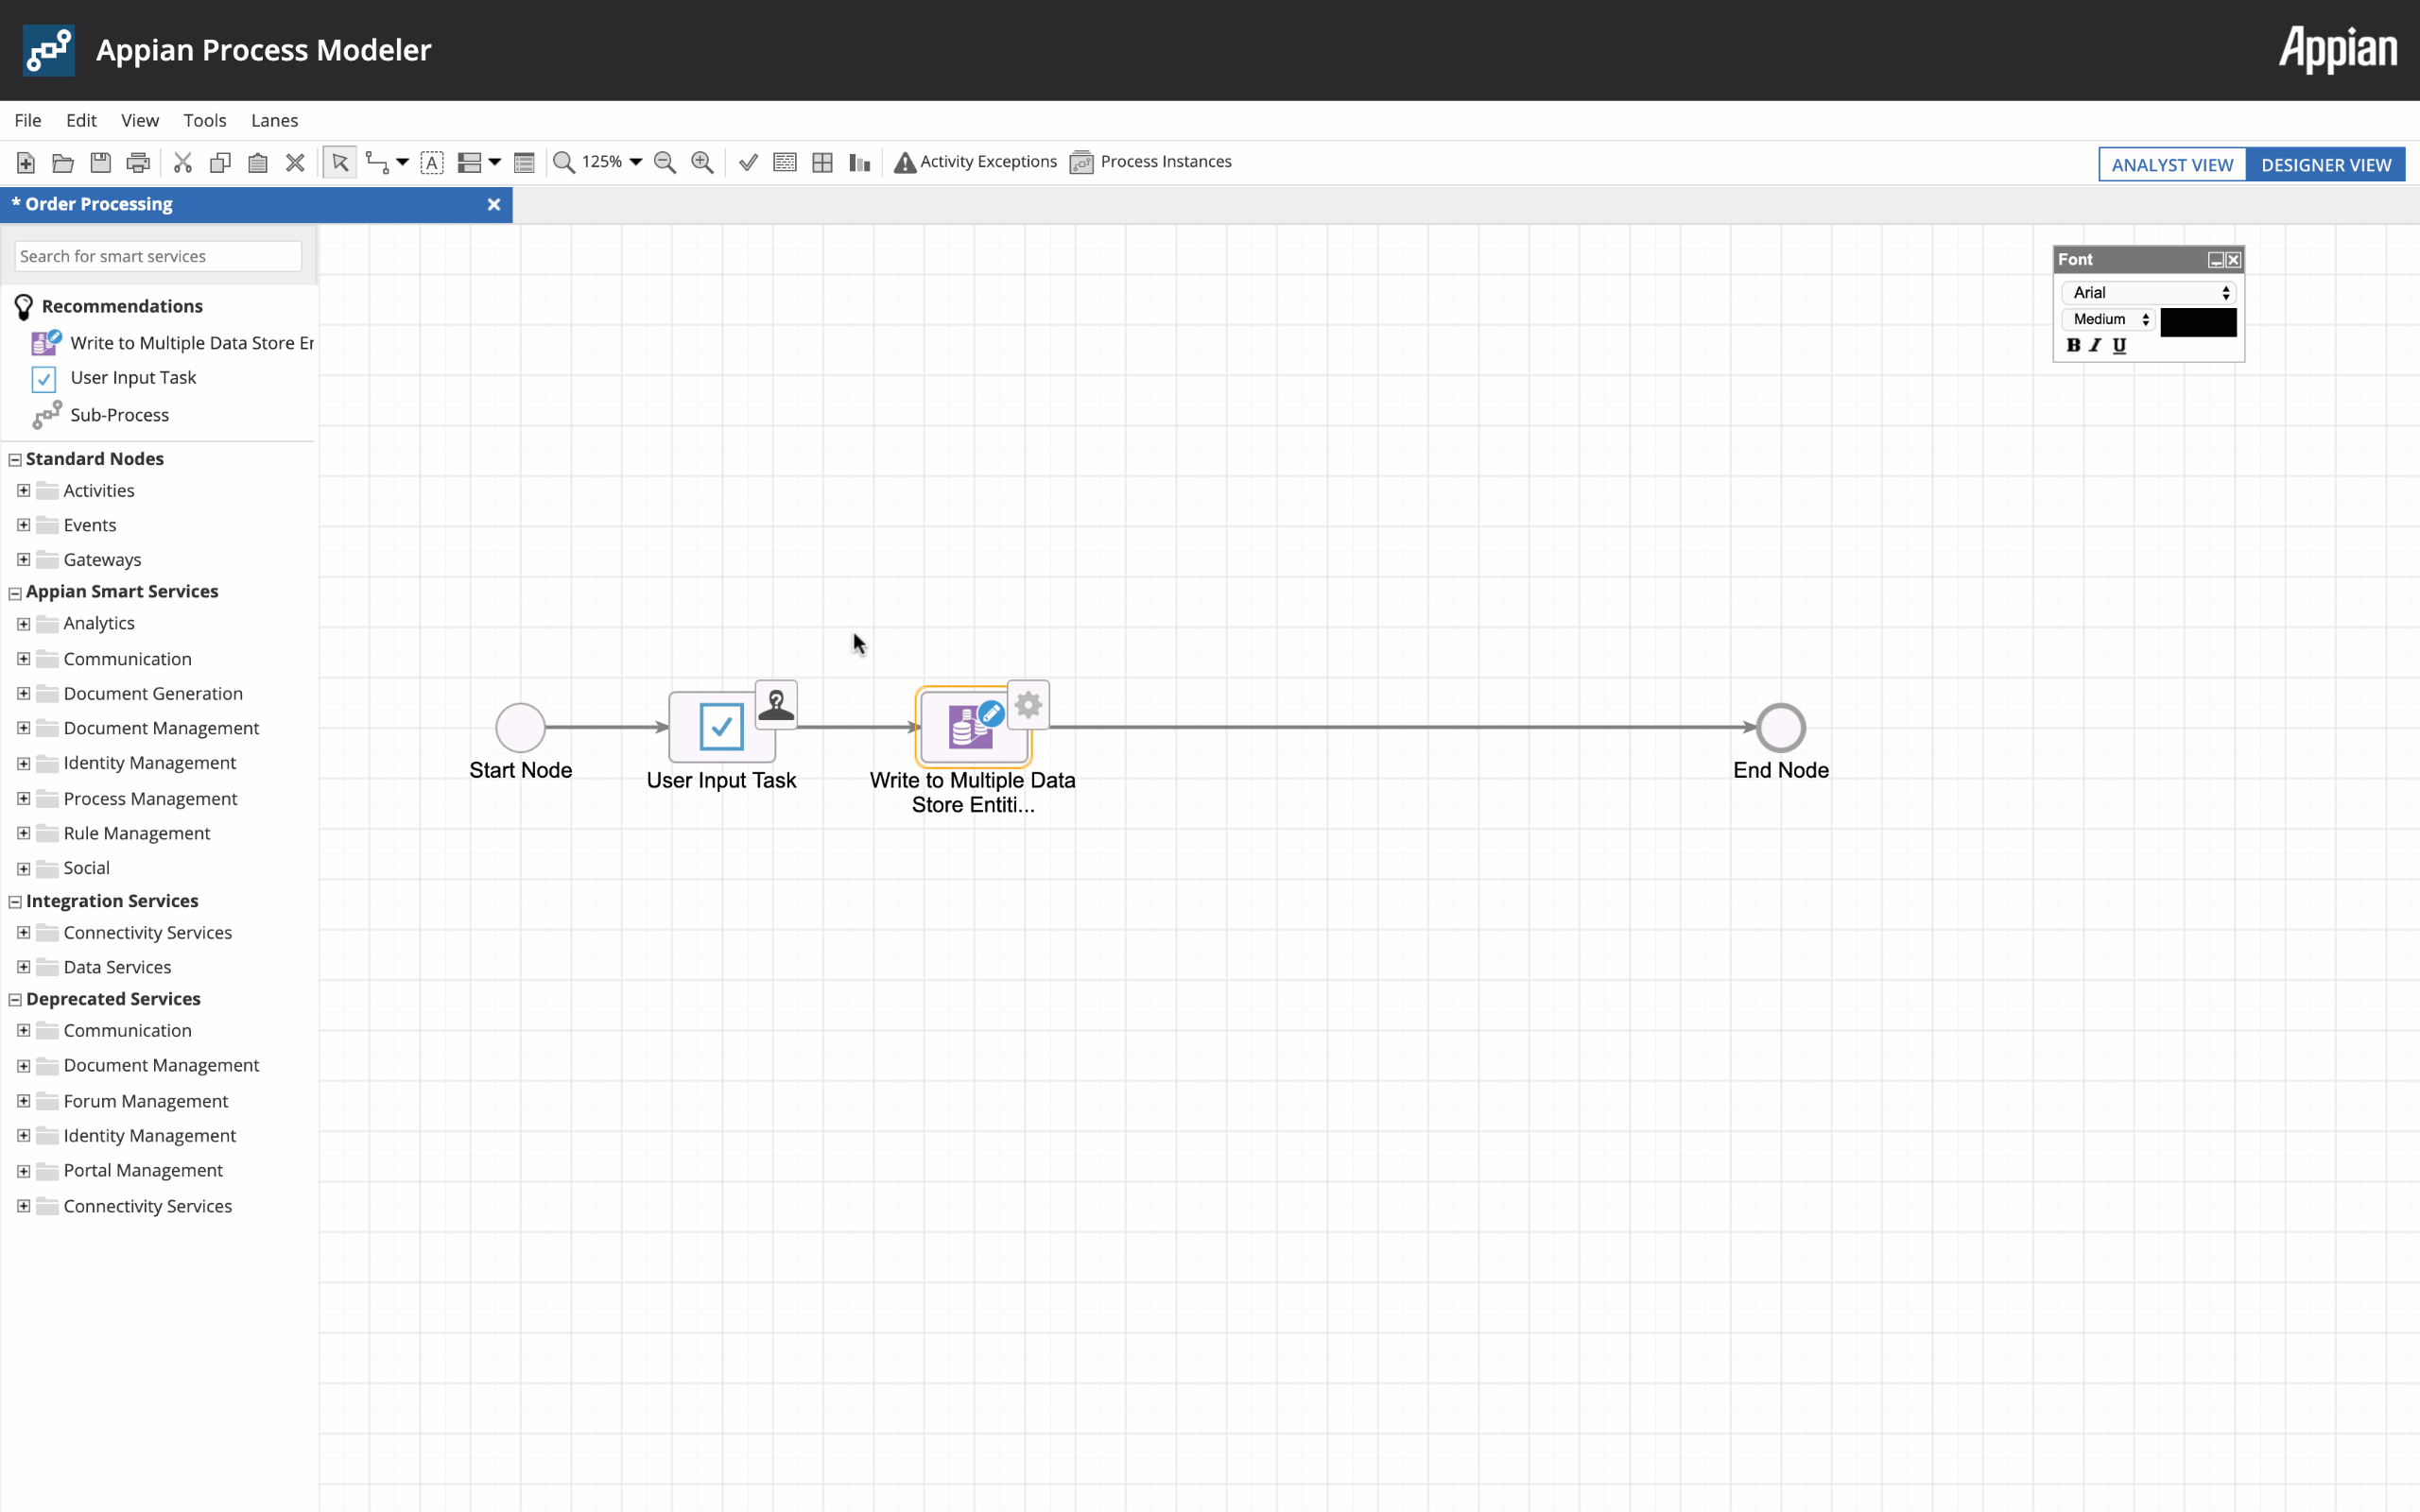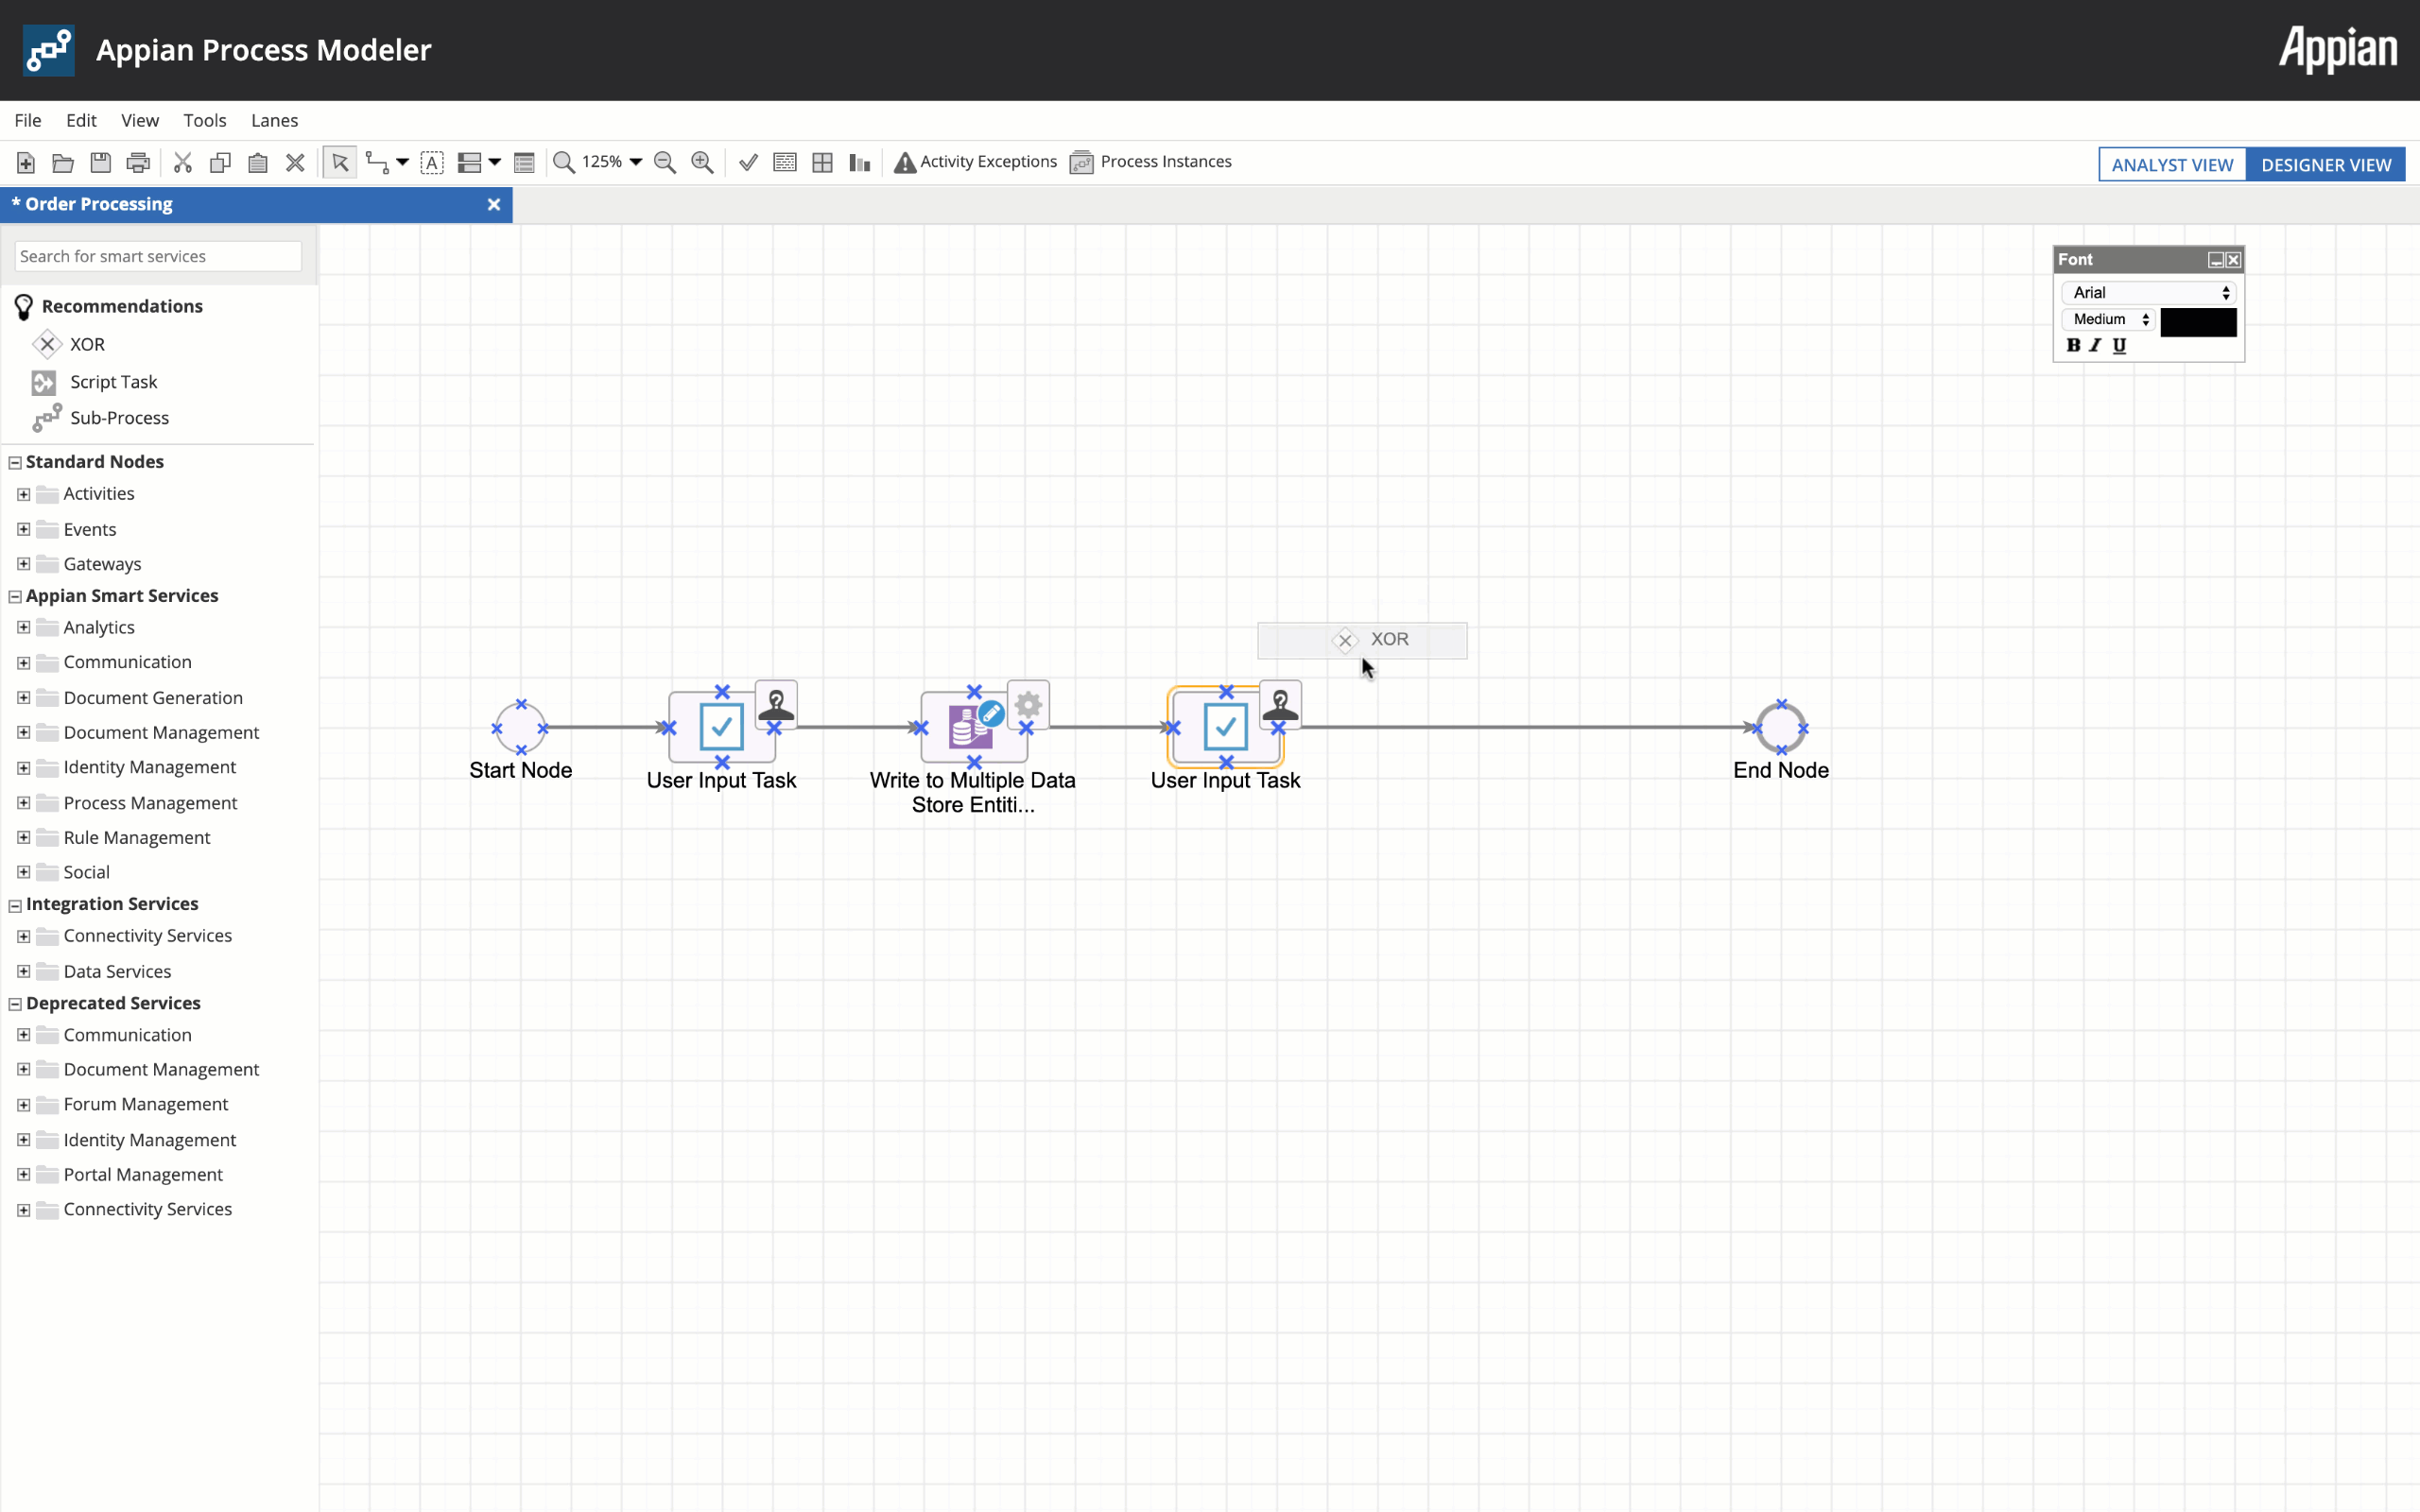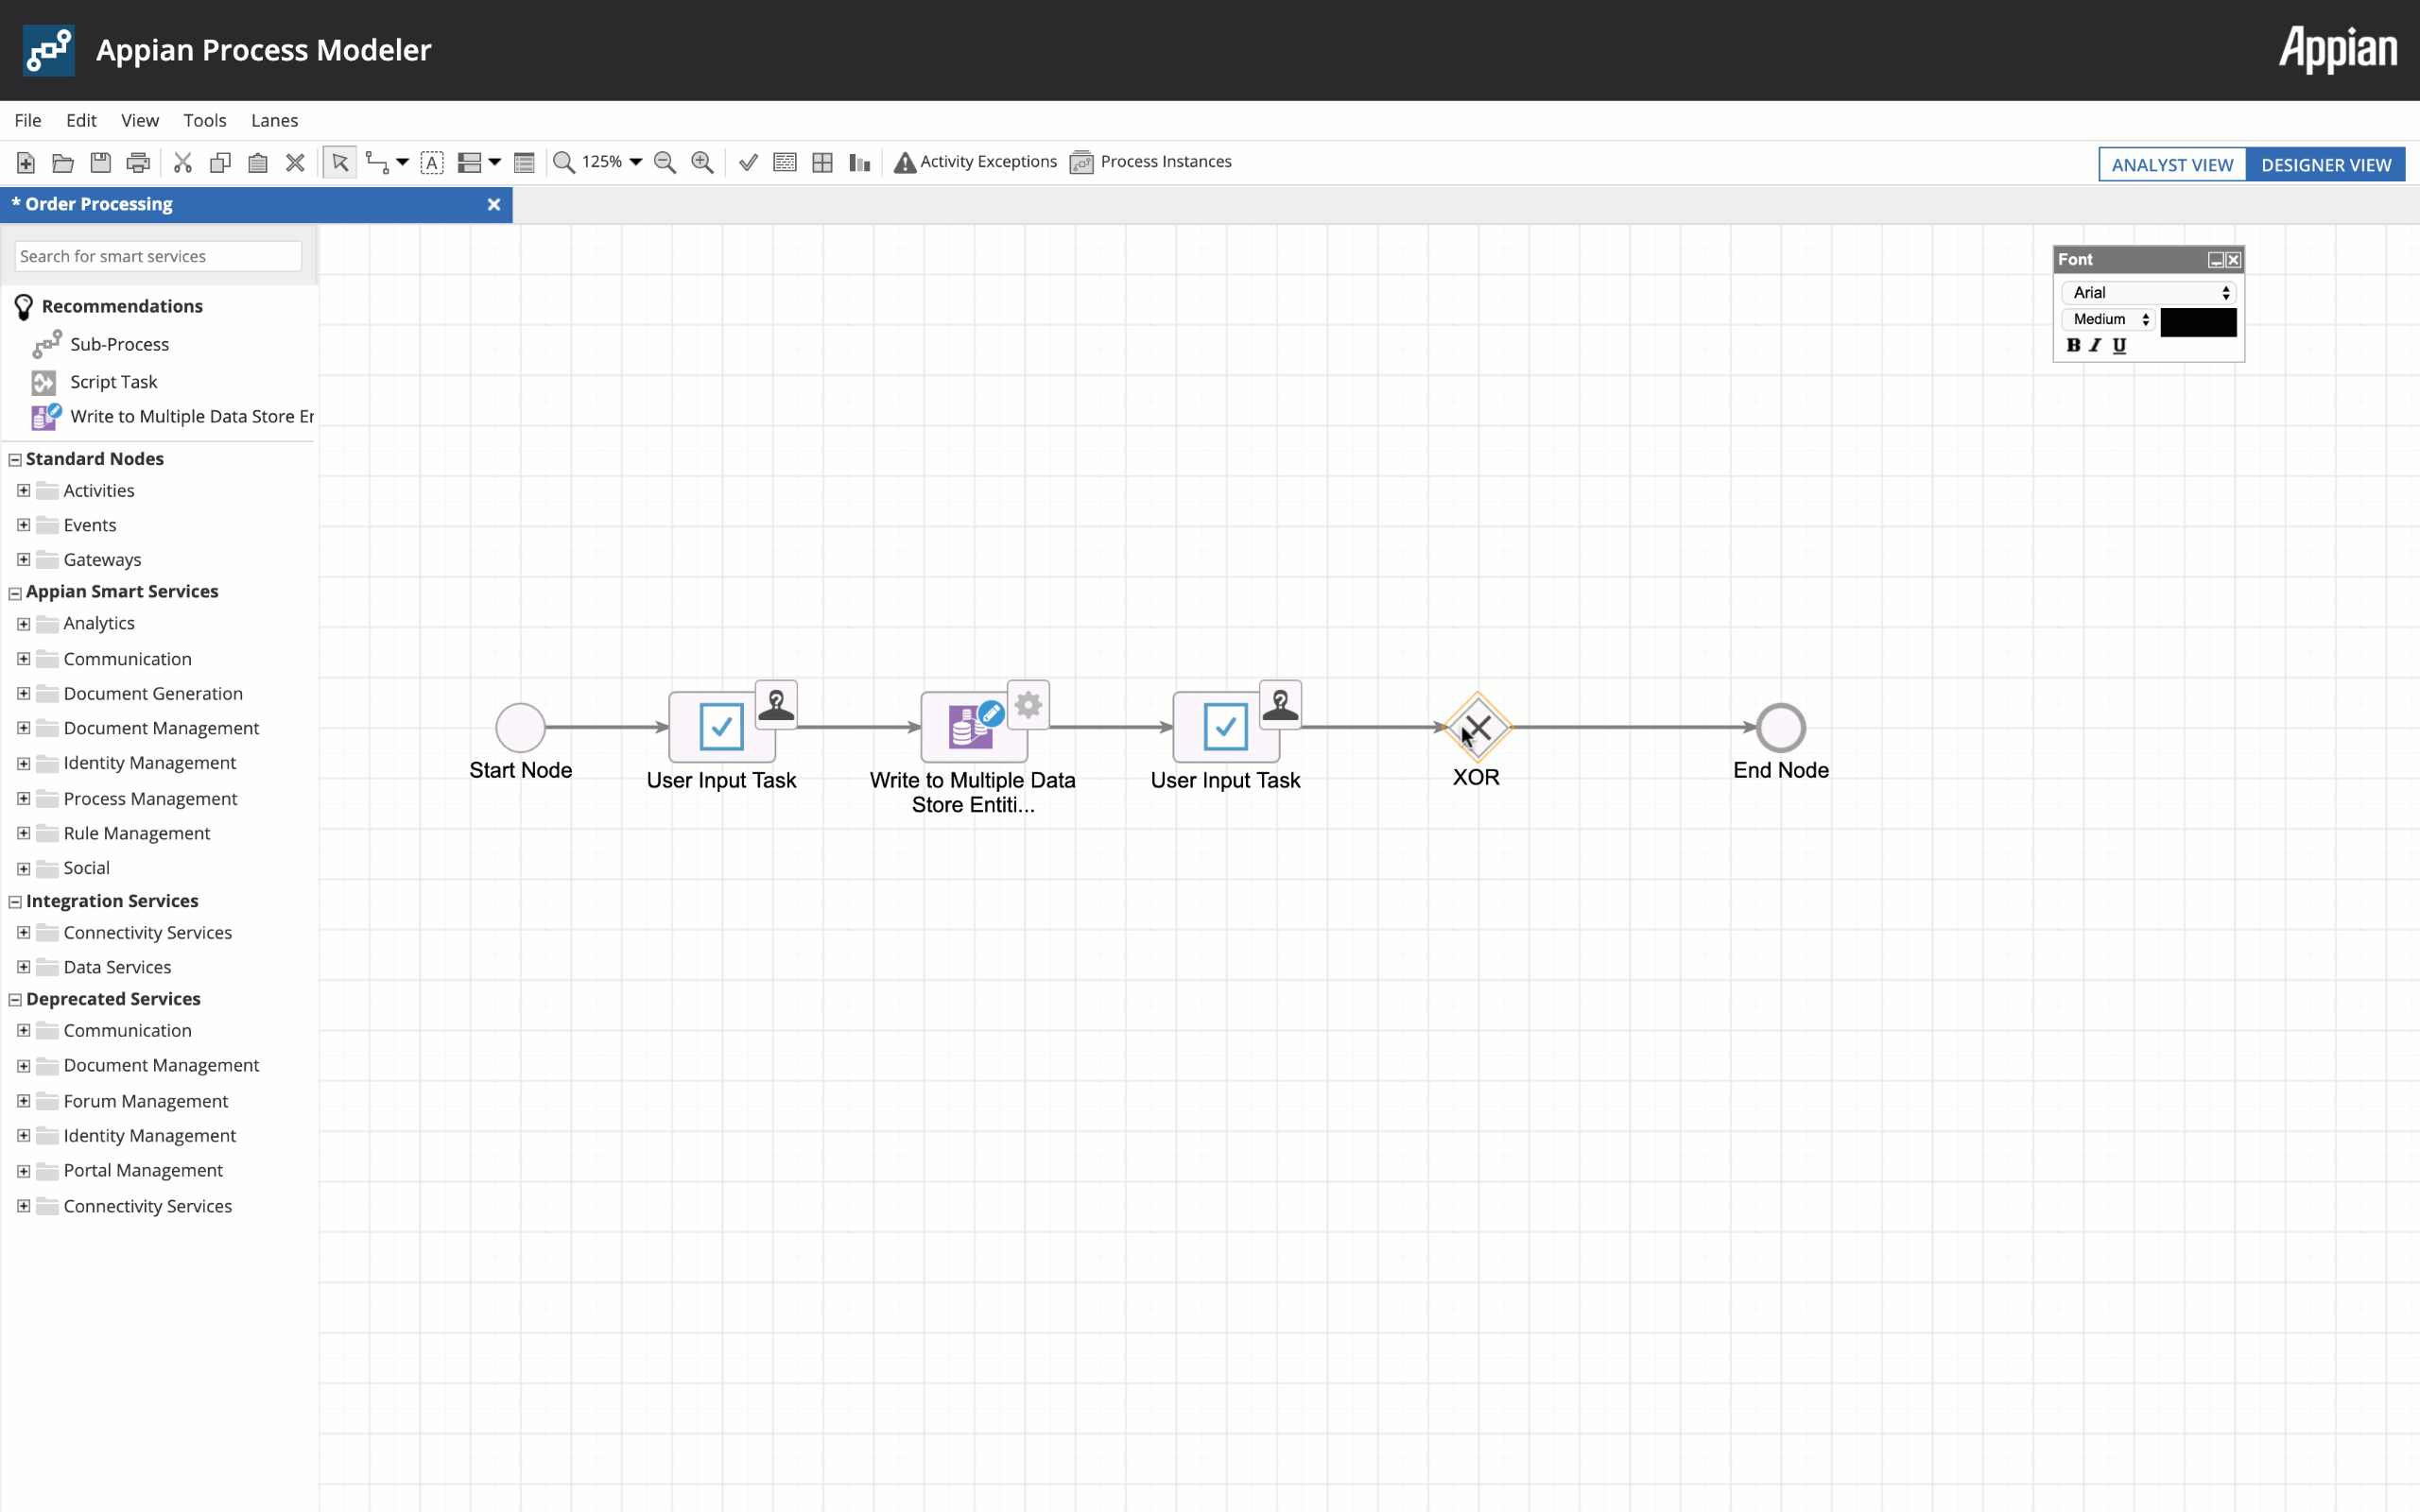
    Appian this week released an update to its low-code application development and deployment platform that employs artificial intelligence (AI) to recommend best next steps, including how to address cybersecurity issues.

    In addition, the latest version of Appian also makes it easier to incorporate robotic process automation (RPA) modules to automate rote tasks in addition to adding support for Google Cloud Document AI, which makes extracting documents for use within an application that employs RPA easier.

    Malcom Ross, vice president of product strategy for Appian, said the machine learning algorithms embedded with the Appian cloud platform make it possible to embrace best DevSecOps practices to accelerate the development of secure applications. With the rise of automated machine learning (autoML) it’s also becoming easier to automate the process of applying machine learning algorithms to application development and deployment, he said.

    While low-code platforms go a long way toward simplifying application-building, Ross said not enough attention is being paid to the deployment process. The goal is not necessarily to roll out more applications faster but to ensure whatever applications are deployed achieve a level of quality that eliminates the need to address cybersecurity issues post-deployment.

    Appian achieves that goal by running automated tests for an application, which now also include Appian Plug-ins to detect potential mismatches in plug-in versions or plug-ins that are missing.

    Ross said that when it comes to AI there always will be some trepidation. However, there are many manual tasks that many developers would just as soon see automated using AI. As AI becomes more widely relied on to drive consumer application experiences, the more acceptance there will be among IT teams to automate internal processes, he noted, adding cybersecurity is one area in which most developers will appreciate whatever help AI can provide.

    AI is not likely to replace the need for a DevOps team or cybersecurity professionals anytime soon. However, at a time when many organizations are massive amounts of economic pressure, it’s clear AI has a significant role to play in reducing the total cost of IT. Despite advances in IT automation, the cost of labor remains one of the most expensive elements of any IT budget. As such, IT organizations have a keen interest in making sure DevOps teams and cybersecurity teams are not wasting time on tasks that might be better handled by a machine.

    Obviously, the way AI systems and IT teams will interact with one another is still being defined. However, the one thing that is certain is platforms such as Appian will be making more recommendations about what needs to be done when. It may take some time for IT professionals to have confidence in those AI recommendations; however, in terms of mistakes that are routinely made it’s also apparent IT teams will soon be running out of excuses.

  • Logi Analytics Simplifies Dashboard Development

    Logi Analytics Simplifies Dashboard Development

    Logi Analytics launched a tool that promises to make it easier to design, build and embed interactive dashboards and data visualization within applications.

    Company CEO Steven Schneider said Logi Composer helps ease the task of creating data visualizations within the context of a DevOps workflow.

    Based on technology Logi Analytics gained via its acquisition of Zoomdata last year, Logi Composer enables DevOps teams to create interactive self-service dashboards for end users as part of a microservices architecture based on Docker containers, he said.

    To help achieve that goal, Logi Composer includes support for a range of Smart Data Connectors constructed as a set of microservices to access databases and other things.

    Schneider said as applications evolve developers increasingly are being required to embed business intelligence (BI) functionality within their application. However, he noted, most end users don’t want to move data into a separate BI application to analyze trends when they could be surfaced more easily within an application they are already using.

    The challenge has been finding a way to provide developers with a set of tools for building self-service visualizations in a modular fashion that makes them easier to build, maintain and update, he said.

    Of course, developers have been adding visualizations to applications for years. But most of those visualizations don’t let end users interrogate data—users now expect to be able to manipulate visualizations with a modern application at a much deeper level, said Schneider.

    A recent market study published by Dresner Advisory Services finds 62% of respondents consider self-service BI to be either “critical” or “very important.” A separate report published by Allied Market Research estimates the market for embedded analytics will generate revenues in excess of $60 billion by 2023.

    Data visualization is a critical aspect of every digital business transformation initiative. As organizations look to digitize more processes in the wake of the COVID-19 pandemic, the need for more robust data visualization capabilities within applications has become more acute. Most end users are unable to make sense of massive amounts of data without the aid of visualization tools.

    It’s unclear to what impact embedding BI capabilities within applications will have on standalone BI applications. There may always be analysts who want to pull data from multiple application sources to analyze trends. However, the bulk of users are likely to have their BI requirements met within an application that includes connectors to pull in external data when required. Applications that don’t include data visualization capabilities are not likely to be widely employed by users.

    Ultimately, embedded data visualization will reduce reliance on both spreadsheets and standalone BI applications. However, like most substantial changes to end user behavior, it may be a while before that cultural shift takes hold.

    In the meantime, DevOps teams should expect to see a lot more analytics functionality being embedded within applications. The challenge now is finding a way to streamline the development and deployment of those modules within the context of a larger application development project.

  • The Top 5 Challenges to Overcome with Heroku Logging

    The Top 5 Challenges to Overcome with Heroku Logging

    Heroku can be a very powerful tool for monitoring the massive amount of data generated by your applications, systems, APIs and add-ons.

    One thing you may have discovered with Heroku logging is that making sense of data within your log files can be time-consuming. When you’re running large numbers of applications which process tons of data each day, the sheer volume of data that appears in the logs can seem overwhelming.

    Managing Massive Log Output 

    Due to the sheer amount of data that is gathered, it’s important to find ways of making the process a little bit easier, limit information to what is useful and organize what you have into digestible pieces.

    Parsing with Drains

    Using Logplex and log drains can help you filter out large chunks of your logs. Syslog drains will help you move any system messages to another server for archiving purposes.  HTTPS drains can help you better take control of your system messaging for sending it to third-party apps for analysis. 

    By assigning clear indicators that identify the application, system or API that creates a log, these can be streamed into channels that can be better understood in relation to their given purposes. 

    Log Retention Period

    While we may think that more information is always good, there is a limit to the amount that we can process. Some log data becomes meaningless or redundant after a certain length of time. It is wise to set realistic log retention periods on data based on business needs.

    Limit Verbosity

    Don’t log everything. Turning on debugging is appropriate during development and if there is a specific problem that needs investigating, but in most cases, these shouldn’t be stored. 

    Complexity in Stream Patterns

    The challenge with large amounts of data is that there may be subtle differences between successful activity and erratic behavior. The details may be small, and essentially invisible to the naked eye unless examined carefully. 

    Use Regex for Identifying Patterns

    Through the use of log analytics tools, you can set these to pick up specified regex patterns to subtle changes or variations in your logs that can provide meaningful insights. 

    Different Log Data Needs

    You may have people with different needs who wish to make use of the information you gain in your Heroku logs. While you have data that is of interest to developers and QA engineers, there are other tech-savvy users who may wish to gain business intelligence (BI) from the massive output of data, to be able to identify key performance indicators (KPI).

    Analytics Tools

    Using intelligent add-on analytics applications can help by filtering and sorting information into usable chunks that can be understood by users in different roles. By accurately filtering, you can provide intelligent real-time alerts for a specific application or system behavior to those who may wish to make use of it. 

    Application Issue Forecasting

    One of the best potential uses of your detailed Heroku logs involves the opportunities to spot patterns of problems that have occurred in the past and use them to predict problems that may occur in the future.

    As an expert, you may be able to spot patterns in your logs, however, even the smartest and most attentive engineers will not be able to manually define every scenario worth detecting.

    Occasionally patterns will occur that are only detectable through the rote process of comparing and contrasting working behavior with non-working behavior. Often, the subtleties are too small for a human to be able to notice the difference.

    Machine Learning Assistance

    Naturally, utilizing ML-powered techniques can help catch the unknowns. By investing in ML, using some of the better libraries or choosing a Heroku logging add-on with these capabilities, you can monitor your applications and infrastructure with less effort. 

    Securing Sensitive Data

    With the rapid pace of CI/CD, a large amount of activity regularly flows through your pipelines from development into production. Throughout this process, it’s possible for sensitive data to start appearing in logs. While your teams may be diligent about keeping control over OAuth credentials, security keys, authentication tokens and more, nobody is perfect. Sensitive security credentials can accidentally make their way onto production servers. Sensitive customer data can also accidentally find its way into public logs if mistakes are made.

    Credential Detection and Security Alerts

    Logs can serve as a saving point for the identification of sensitive information. Using a parsing engine, these can be immediately redacted for compliant log management. By monitoring your log files for any patterns which could include secret keys or other potential security breaches, you’ll be able to continue ingesting critical log data without increasing business risk.

    Heroku Private Spaces

    With Heroku Enterprise, you can make use of Heroku Private Spaces which are an isolated network of private apps and data services, which will help you keep sensitive data separate from public interference. If you are handling a large amount of sensitive customer data, ensuring that any information gets filtered into these places will help you remain compliant with GDPR and other privacy-related regulations.   

    Conclusion

    Heroku can be a fantastic solution for monitoring the activity which goes on in your cloud clusters.  However, unless you have solid analytical tools in place, you may find yourself spending a lot of time wondering how to make use of this sea of data that has been collected. Consider using an add-on as an analytic layer to help spot patterns, organize data better and create smart alerts to make sure your operations continue to run smoothly.

  • Atlassian Unfurls Bevy of DevOps Updates

    Atlassian Unfurls Bevy of DevOps Updates

    Atlassian today made a dozen updates to its DevOps portfolio as part of an effort to better unify workflows spanning disparate tools.

    Suzie Prince, head of product for Bitbucket at Atlassian, said the latest updates are intended to enable DevOps teams to streamline workflows without requiring everyone in the organization to standardize on the same set of tools.

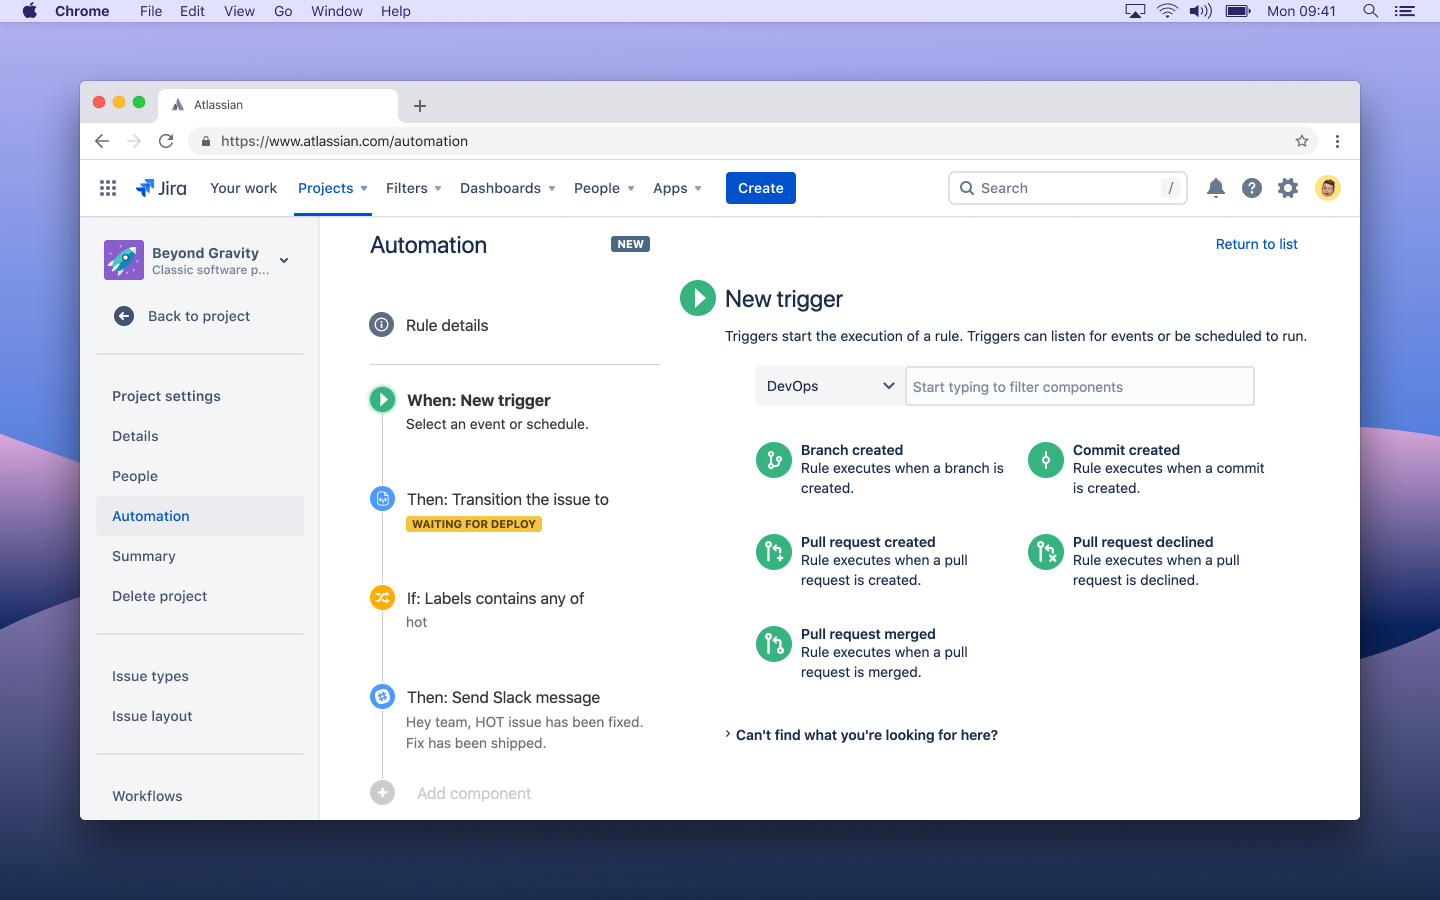
    Updates to the Atlassian DevOps portfolio include DevOps Automation Triggers, which makes it possible to create automation to keep development activities synchronized, such as reassigning issues surfaced in the Jira project management application from Atlassian to code review or sending a message to a Slack channel.

    Atlassian DevOps

    The Bitbucket repository from Atlassian has also been updated to make it easier and faster to review code changes after a pull request. New features such as a consolidated list of tasks, integrated Jira issue creation and activity feed filters make it possible for developers to complete their code reviews faster and juggle multiple pull requests at once, said Prince. A Your Work dashboard in Bitbucket Cloud has also been expanded to include assigned Jira issues.

    The Atlassian VS Code integration is also being made available to make it easier for developers who use the Microsoft integrated development environment to more easily track and visualize Bitbucket Pipelines.

    A Code Insights in Bitbucket Cloud has also been added to bring scanning, testing and analysis tools into the code review process, including Mabl for test automation and Sentry for automated monitoring. Bitbucket is also now providing integration with Snyk scanning tools to make it easier to discover vulnerabilities.

    Available in a preview mode is an automated change management capability across Jira Service Desk Cloud and Bitbucket Pipelines that can be used to pause CI/CD processes, create a change request in Jira Service Desk and trigger deployment once it is approved.

    A Risk Assessment Engine in Jira Service Desk Cloud also allows IT teams to score the risk of a change and automatically approve and deploy low-risk changes. A Change Management View has also been added to Jira Service Desk Cloud to streamline approvals for high-risk changes by pulling all of the relevant information together in traceable change requests.

    Atlassian has also tightened integration between its Opsgenie incident management software and Bitbucket Cloud to centralize alerts and filters. Via an Incident Investigation Dashboard, members of a DevOps team can look at the deployment that happened right before the incident, add it as a potential cause, and contact the developer who made the change if it needs to be rolled back.

    The company has also extended integrations with Slack and Statuspage to facilitate both members of DevOps teams and external stakeholders.

    Finally, Atlassian is making available a resources hub to make it easier to share DevOps best practices, templates and guides.

    Prince said it’s not ever going to be feasible for most organizations to standardize on one set of DevOps tools. The goal should be to enable organizations to construct DevOps processes in ways that allow developers to employ whatever tool is their favorite at the moment. Only then will organizations get developers to buy into a DevOps process that doesn’t necessarily change the way they are most comfortable working, she noted.

    The challenge, of course, is often getting IT leaders to be as equally comfortable with what, from their perspective, might be an experiment in controlled chaos.

  • Chef Extends IT Automation Reach

    Chef Extends IT Automation Reach

    Chef, at its online ChefConf 2020 event today, launched Chef Compliance and Chef Desktop as well as additional enhancements to the tools it provides for application deployment automation.

    John Wyss, vice president of product for Chef, said Chef Desktop enables IT teams to write their own configuration and compliance requirements as human-readable code using YAML files to manage and secure entire fleets of endpoints via a centralized console. It includes pre-written configuration code and curated content that can be employed to both audit and harden desktop operating systems.

    IT teams will now avail themselves of a zero-touch process for enrolling and provisioning endpoints while at the same time automating software deployment and management, Wyss said. That includes being able to enforce security policies using configuration profiles, data encryption and system updates.

    Chef Compliance, meanwhile, is built on top of Chef InSpec, an open source framework for testing and auditing applications and infrastructure. Chef Compliance takes Chef InSpec further by including tools to automatically audit IT environments based on the specifications defined by the Center for Internet Security (CIS) and Security Technology Implementation Guide (STIG).

    Those audits can then be applied to automate the remediation process without having to write code if IT teams so choose, said Wyss. The goal is to provide DevSecOps teams with a unified language for managing security and compliance, he added.

    Finally, Chef has updated Chef Enterprise Automation Stack to include analytics to filter and update views for disconnected services and receive real-time health-check messages and status alerts. Chef has also added rapid rollback, package cleanup and layered container support, and has made it easier to manage package settings and deploy packages across multiple platforms.

    Collectively, these capabilities should make it easier for DevOps teams to reduce process friction across the entire DevOps life cycle.

    In the wake of the economic downturn brought on by the COVID-19 pandemic, interest in IT automation is on the rise. Many organizations are either freezing IT headcount or, worse, yet, reducing the size of their IT staff. At the same time, IT environment is becoming more complex, especially if most employees continue to work from home. IT teams now need a common set of tools for managing not only application deployments on servers or in the cloud but also endpoints. Ultimately, that approach should also go a long way toward reducing the total cost of IT.

    In fact, in the wake of the downturn more organizations than ever are receptive to automating IT processes. What was once viewed as potentially an existential threat to the existence of the IT staff has become the only way to manage IT at scale, at a time when cutbacks are broad-based. Organizations that don’t find a way to automate the management of IT are likely to incur significantly higher costs than those that do. Arguably, the issue is no longer what to automate and when, but rather how much and how soon, as both applications and the end users accessing them become ever more distributed.

  • BMC Software Closes Compuware Deal, Sets Course

    BMC Software Closes Compuware Deal, Sets Course

    BMC Software today announced it has formally completed its acquisition of Compuware as part of an expanded effort to modernize mainframe environments.

    Bill Miller, president of ZSolutions at BMC, said now that the deal has been closed the combined companies will be able to more tightly integrate Compuware’s Topaz application development and deployment platform with the BMC Automated Mainframe Intelligence platform, as part of an Autonomous Digital Enterprise (ADE) initiative based on ongoing investments BMC is making in AIOps.

    Chris O’Malley, CEO of Compuware, said that level of integration will, for example, make it easier to automate the deployment of database and provisioning of mainframe resources using tools from BMC within a set of DevOps processes optimized for mainframe environments.

    The goal is to make the mainframe just one more target platform on which DevOps teams can build and deploy applications faster, added O’Malley. That’s becoming a bigger requirement in the wake of the economic downturn brought on by the COVID-19 pandemic, he said, as organizations prioritize digital business transformation initiatives that will inevitably require updates to mainframe applications.

    Rather than increasing technical debt by duplicating existing capabilities, O’Malley said more organizations will look to modernize mainframe applications to make them more accessible to a wide variety of front-end applications.

    The rate at which IT organizations that deploy applications on mainframes have been adopting DevOps has been uneven at best. Mainframe applications are often considered to be among the most mission-critical in the enterprise. Therefore, IT teams have relied on waterfall processes to build and deploy mainframe applications in a more deliberate fashion.

    At the same time, however, the use of Linux on mainframes has increased considerably in the last several years. The applications deployed on Linux operating systems on the mainframe frequently employ the same DevOps processes to deploy applications on Linux running on distributed computing systems.

    BMC’s ambitions, of course, far exceed the mainframe. The company has a portfolio of tools for managing both distributed computing and mainframe platforms. During the economic downturn, BMC is betting many IT teams will be under increased pressure to reduce the total cost of IT by centralizing the management of mainframes and distributed computing systems, among other moves.

    Of course, BMC is not the only IT vendor with similar ambitions. IBM and Broadcom, which acquired CA Technologies, are moving down a similar path. IT organizations will need to determine which providers enable them to best streamline management processes.

    In the meantime, it remains to be seen how much organizations remain committed to the mainframe. It’s generally not feasible for most organizations to move a transaction processing application running on zOS into the cloud. However, it doesn’t necessarily follow that those IT organizations will continue to invest in building and deploying new applications on mainframes instead of making them more accessible via application programming interfaces (APIs).

    Regardless of the strategy adopted, however, it is not likely that after being around for more than 50 years, mainframes will be disappearing anytime soon.

  • PagerDuty Looks to Streamline IT Incident Management

    PagerDuty Looks to Streamline IT Incident Management

    PagerDuty has added more automation and analytics capabilities into its portfolio of incident management tools, at a time when organizations are looking to significantly reduce the total cost of IT.

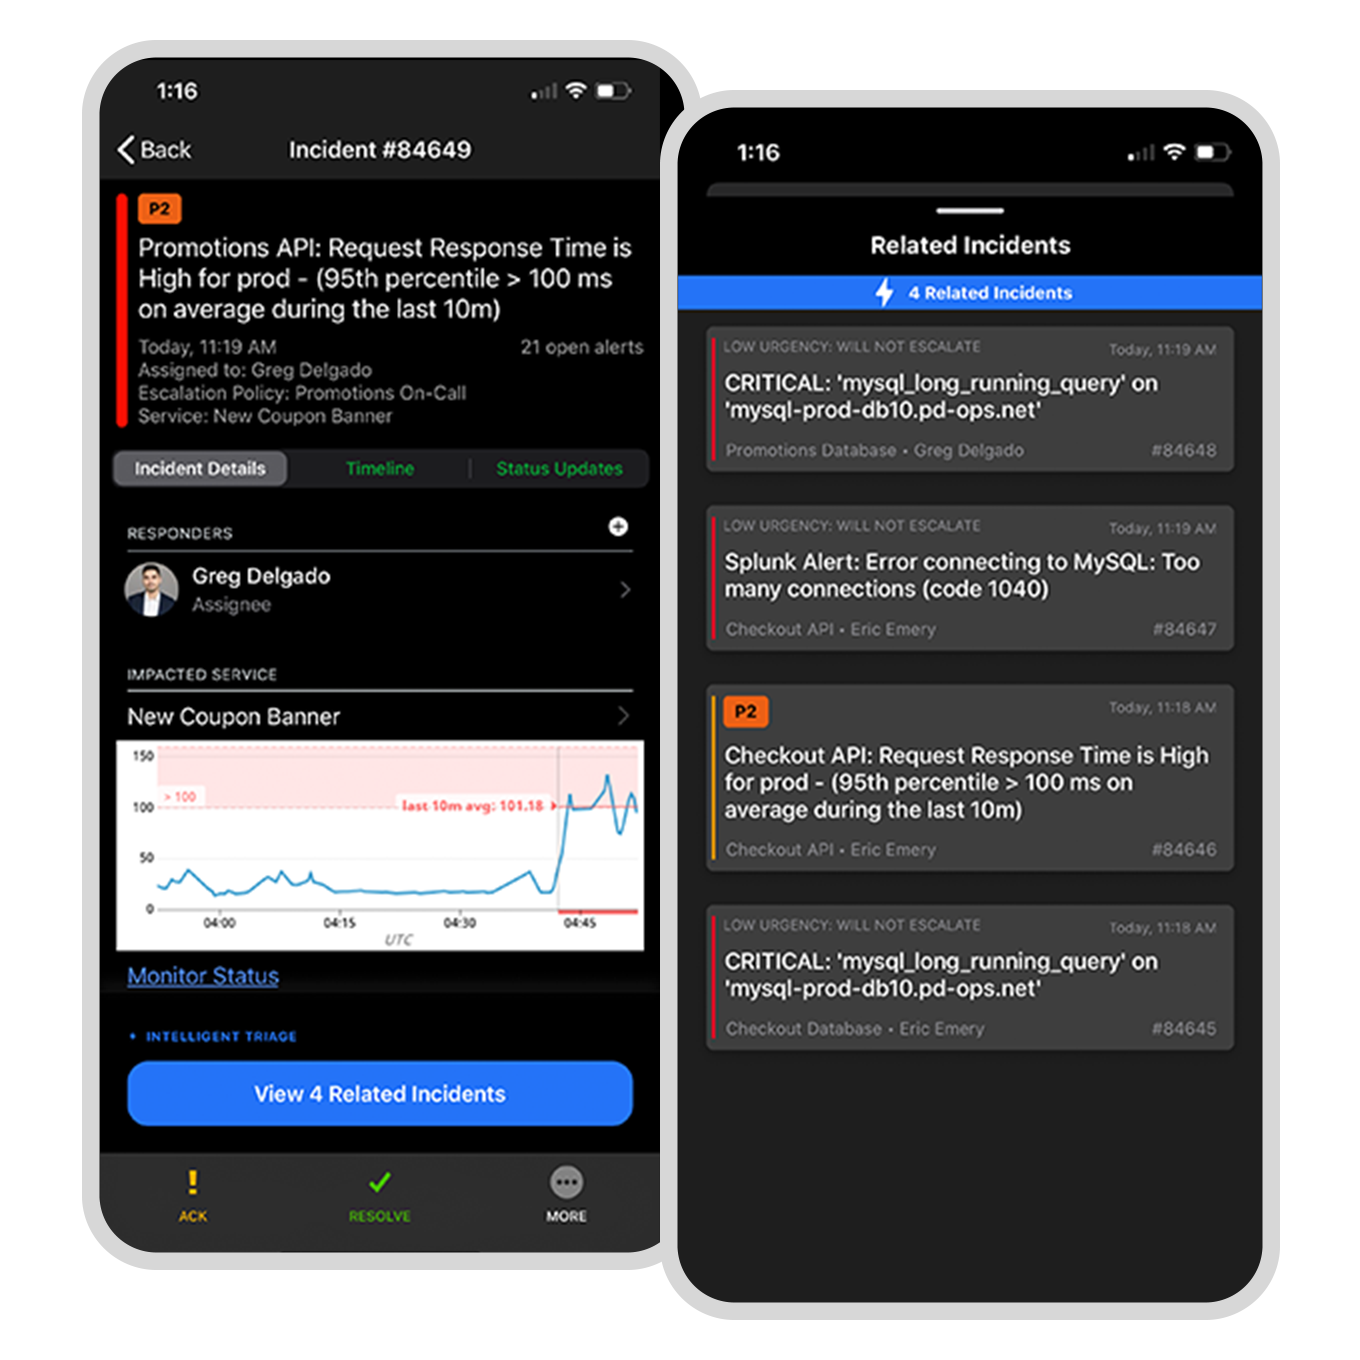
    Jonathan Rende, senior vice president of product at PagerDuty, said the general release of Intelligent Triage advances the level of AIOps that can be applied to incident management by eliminating a raft of manual tasks.

    Intelligent Triage aggregates signals from more than 375 monitoring, observability and ticketing tools, which are then grouped based on relationship and elevated depending on the impact on the business. That level of contextual data makes it possible for IT teams to increase productivity while dramatically reducing alert fatigue, said Rende.

    At the same time, PagerDuty is adding support for integration with Microsoft Teams alongside existing support for Slack. IT teams are increasingly relying on these collaboration tools to process requests for help from end users, he noted.

    In some cases, IT teams are communicating with one another via these media or employing built-in tools embedded in the PagerDuty incident management platform. In either case, workflows across IT teams are now occurring in near real-time, said Rende.

    Finally, PagerDuty is adding a Dynamic Service Directory to give DevOps teams a central knowledge base that identifies owners and experts for each service and their associated run books, in addition to making available a mobile status dashboard to allow remote teams to collaborate more effectively when incidents arise. That capability is especially critical at a time when many IT staffs continue to work from home as part of the effort to combat the COVID-19 pandemic, said Rende.

    In general, IT organizations are looking to automate incident response whenever possible to both minimize costs and potential disruptions. Businesses are more dependent on IT services than ever. However, as more applications are deployed the nosier the IT environment becomes. Discerning which alerts are stemming from the same root cause issue becomes more relevant as organizations either limit headcount or even look to reduce it during a time of widespread economic uncertainty.

    Of course, regardless of the state of the economy, most IT professionals would rather not have to waste time on manual tasks that don’t add a lot of value to the business. Most IT professionals need to free up more time to achieve more pressing goals. Every minute spent on chasing down an alert that winds up being yet another wild goose chase just piles on more stress.

    Advances in automation and AIOps have been coming at a steady pace for the last several years. The adoption of these new capabilities to manage incidents has been uneven at best. In the wake of the economic downturn brought on by the pandemic, it’s now more a question of how soon IT organizations will be tapping into these capabilities to streamline the management of IT. After all, many IT managers are going to conclude there’s no sense in letting a good crisis go to waste.

  • CTO.ai Launches SlackOps Tool for DevOps

    CTO.ai Launches SlackOps Tool for DevOps

    CTO.ai has launched SlackOps, a platform for managing DevOps workflows in real-time via the Slack communications and collaboration service.

    Company CEO Kyle Campbell said many DevOps teams are embracing Slack to share updates with one another. SlackOps takes that preference for DevOps a step further to enable complex DevOps processes, also known as ChatOps, to be launched from the Slack command line.

    That approach allows any member of the DevOps team to write a workflow once and securely share it regardless of what language is employed, added Campbell.

    SlackOps also provides access to a public registry that CTO.ai already makes available for sharing developer shortcuts within a specific community.

    Beyond streamlining communications processes across DevOps teams, Campbell said DevOps teams will be able to surface additional insights into workflows using DevOps research and assessment metrics to make them more efficient. SlackOps also makes it easier to onboard new members of a DevOps team, he noted.

    SlackOps is deployed as a container on the Slack platform and can be downloaded via the Slack marketplace in a couple of minutes.

    The goal is to enable organizations to embrace a lean approach to DevOps that enables them to quickly adjust processes as required, said Campbell. Rather than having to commit to a single tool or platform, developers should be able to advance the overall state of DevOps within their organizations without having to be concerned whether a new tool or platform will disrupt communications across the DevOps team.

    It’s too early to say to what degree Slack might emerge as a control plane for managing DevOps processes. It is, however, becoming more popular as a way to communicate across members who employ a broad range of tools. Rather than attempting to force DevOps teams to standardize on a single set of tools and platforms, Slack provides a more flexible means of communicating in real-time that is delivered as a cloud service.

    Of course, there are now plenty of alternatives to Slack. It will be up to each DevOps team to decide which communications medium best suits them. However, embedding a DevOps workflow application within a communications platform could serve to make Slack a more compelling option for many DevOps teams. Regardless of the communications medium, DevOps teams should expect to be more continuously engaged with one another. That may prove to be a critical requirement with most members of a DevOps team working from home for the foreseeable future in the wake of the COVID-19 pandemic.

    As workflows built around asynchronous email messages increasingly are giving way to real-time communications, the challenge many DevOps teams face is finding a way to embrace that higher level of interactivity without members of the DevOps team becoming overwhelmed by the volume of messages being shared. Making the transition to DevOps was enough of a cultural challenge for many organizations. Inundating DevOps teams with real-time messages, not all of which may be pertinent to a DevOps workflow, needs to be tempered by tools that help identify the DevOps signal within all the noise.

  • GitLab Releases Massive Update to CI/CD Platform

    GitLab Releases Massive Update to CI/CD Platform

    GitLab has updated its continuous integration/continuous delivery (CI/CD) platform with a raft of capabilities spanning everything from value stream management to cybersecurity.

    In addition, GitLab announced it is making generally available Gitaly Clusters, which enable DevOps teams to create a warm replica of a Git repository.

    Brendan O’Leary, senior developer evangelist at GitLab, said with release 13 GitLab continues to build on a single code base that allows the platform to be managed and accessed as an integrated set of applications rather than disparate components that DevOps teams need to pull together and then manage.

    In terms of core DevOps capabilities, the latest release adds the ability to customize the Value Stream Analytics module to specific workflows. GitLab is also planning to make it possible to visualize stages of a workflow.

    GitLab is also improving traceability between requirements and has added the ability to visualize the workflow associated with a specific release. A future release will enable DevOps teams to employ feature flags to conduct both A/B testing based as well as create feature flags from merge requests and to filter feature flags by status, according to the company.

    Other capabilities added include more customizable dashboards, with security dashboards now being shareable outside of GitLab to foster collaboration with IT security teams. Future releases will add Kubernetes Clusters to the dashboard to show all clusters and pods in use.

    DevOps teams now can route existing monitoring alerts to GitLab for triage and incident resolution. At the same time, GitLab has moved design management to the core platform.

    GitLab is also now making AutoDevOps, which provides pre-defined CI/CD pipelines, available on Amazon Web Services (AWS).

    In terms of cybersecurity, GitLab has revamped the way the platform manages vulnerabilities to make it easier in a future update to prioritize remediation efforts.

    GitLab also has static application security testing (SAST) support for .NET frameworks and has expanded support for offline environments. There’s also now support for dynamic application security testing (DAST) for REST application programming interfaces (APIs) and access to full commit history scan for secrets. Fuzz testing support will be introduced later this year, according to the company, along with an ability to secure secrets across services. GitLab also plans to add integration with security tools that track container behavior analytics, as well as an out-of-the-box container network policy.

    Thanks to GitLab’s collaboration with Okta, there is now also tighter integration with Okta’s System for Cross-domain Identity Management, which can be provisioned for a GitLab group.

    In terms of compliance, GitLab also plans to enable DevOps teams to establish a compliance framework, adopt its regulatory controls and simplify audit reporting. The company is also working on an initial security policy user interface to simplify setting up security guardrails.

    Finally, GitLab has become a Common Vulnerabilities and Exposures (CVE) ID Numbering Authority (CNA). GitLab users can request a CVE from GitLab, either for GitLab itself or for any project hosted on GitLab.com. In the future, users can request CVE IDs directly from within GitLab.

    O’Leary said GitLab is working toward increasing developer confidence in their security skills. By making it easier to embrace best DevOps practices, developers no longer will have to tiptoe around security issues that they today largely have little to no familiarity with, he said.

    In general, O’Leary said GitLab’s biggest challenge is getting organizations to move beyond simply using it to manage source code. Once organizations do make their first foray beyond source code management, however, it’s not too long before they are employing a wide range of modules, he noted.

    Of course, encouraging organizations to dive deeper DevOps has as much to do with the culture of the organization as it does the capabilities of the CI/CD platform employed.