Tag: devsecops

  • Helping Developers Win in the Shift-Left Revolution

    Helping Developers Win in the Shift-Left Revolution

    The shift-left revolution is upon us. Just because it’s a cliche, doesn’t mean it’s not true. As software development organizations continue to implement DevOps culture, processes, and tools, developers are adopting the practice of testing and ensuring the security of their applications as early as possible in the DevOps pipeline.

    This is quite a change from the traditional waterfall method. There, developers dealt with the design and creation of a product or application and security professionals came in after they were finished, to review and test security, flagging any possible issues and sending them back to the software teams to figure it out.

    This fundamental change in the way companies are addressing application security affects many of the moving parts in a software outfit. It requires a new set of processes, practices and tools all to be implemented, all while keeping up with today’s fast-paced release cycles.

    To gain an understanding and insight on how developers are handling this hefty challenge, we polled more than 600 developers in software organizations and asked them about how security figures into their day-to-day tasks and processes, and the tools that help them to address their evolving roles.

    Developers: Owning Their Shift Left

    The first thing that we wanted to learn is whether developers are on board with the shift-left approach that most organizations have adopted for security testing. Our findings showed that, for the most part, developers are taking ownership of the day-to-day operational responsibility for AppSec in their organizations, playing a more significant role on this front to secure their products.

    When asked who owns the day-to-day operational responsibility for AppSec in their organizations, 23% answered that developers own those responsibilities, 21% said DevOps, 28% said software development team leaders owned it and only 29% said security teams in their organizations are the owners.

    developers shift-left chart 1The fact that a whopping 71% of developers put the ownership of AppSec squarely on the shoulders of software development and DevOps folks means that developers are very much on board with the shift-left movement and have taken on the new security tasks that come along with that.
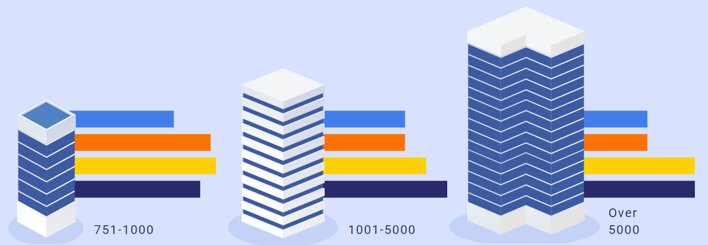
    Breaking it down, we also found that in smaller organizations, more developers and DevOps professionals feel that they own their AppSec responsibilities, while those percentages go down with larger organizations. This can be explained by the fact that often smaller companies have less specialization, requiring developers to branch out of their professional comfort zone. Smaller organizations also tend to allow developers more freedom and flexibility to define their own processes.

    developers shift-left chart 2Do these responses mean that in addition to their focus on innovation, functionality and quality, developers have also added security into their considerations when they are in the process of creating and building projects?
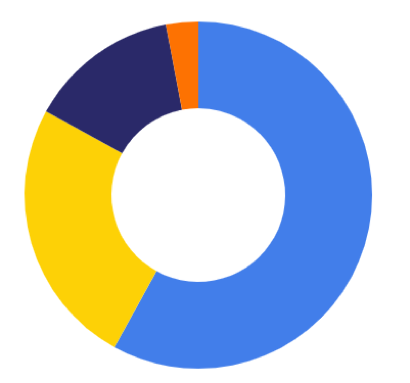
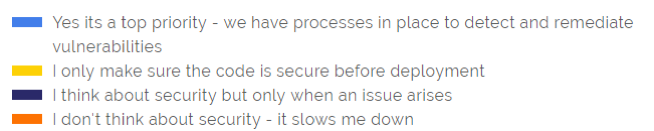
    The answer would appear to be yes, according to 58% of developers in our survey, with an additional 39% saying that security figures into their consideration when issues arise (14%) or that they validate security before deployment (25%). Only 3% of developers said that security is none of their concern since it slows them down.

    Are you taking security into consideration when developing software?

    developers shift-left chart 3

    While their responses show that there is still a ways to go before security is completely baked into development processes, it’s clear that most developers are already in the right direction, making security a priority within their tight schedules.

    The AppSec Process: Who’s On First?

    How does making security a top priority or at least a consideration figure into the different phases in the DevOps pipeline? Practically, where is it being applied? We asked developers at which phase in the software development life cycle (SDLC) they started testing their AppSec.

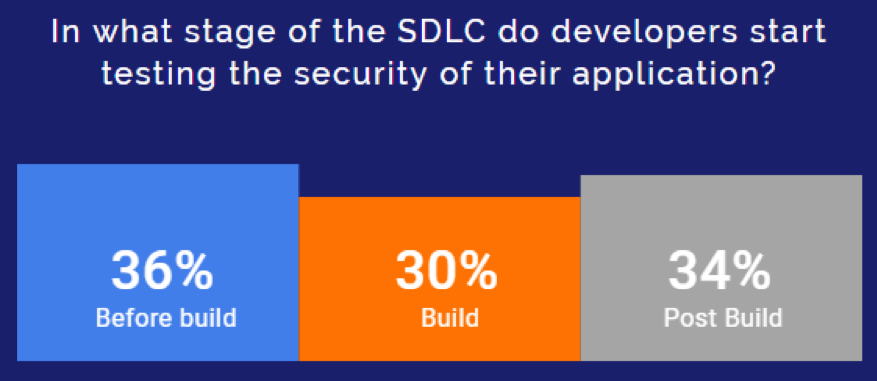
    Their answers showed once again that developers are taking on security where it traditionally was not a part of their workflow. In fact, many replied that they are integrating security testing tools as early as the pre-build stage, with 36% of the respondents saying that they are testing in their IDE and repositories.

    developers shift-left chart 4Survey results also showed that along with the DevOps processes, they are also adopting tools that help them to shift security further left. 68% of developers report using at least one AppSec technology such as SAST, DAST, SCA, IAST or RASP. All of these automated solutions help security teams and developers detect potential security issues in their products, providing software teams with visibility and control over their AppSec.

    A Question of Remediation

    Until now, survey results show that developers have taken their place on the front lines of AppSec and the shift-left revolution, arming themselves with an impressive collection of automated detection tools. However, these solutions are creating a new set of issues that should worry stakeholders.

    It appears that the much-needed security testing tools are threatening to bury development teams under a mountain of alerts, which they are now required to research and remediate while keeping up with their deadlines. It’s impossible for developers to keep up with all of the security alerts in their inbox, especially considering that many AppSec tools were developed for security teams and focused on widespread coverage (detecting all potential issues), rather than accuracy and prioritization.

    This poses quite a challenge for developers, who say that they are spending a substantial chunk of their very valuable time dealing with remediation-related tasks. A full 42% of the respondents reported that they spend between two and 12 hours each month on these tasks, while another 33% said that they spend 12 to 36 monthly hours on them.

    In light of these time-heavy statistics, it is clear that developers need new technologies and practices that will allow them to prioritize security without slowing down the development life cycle and costing them so many valuable work hours.

    Helping Developers Win the Race to Remediation

    The survey results showed that developers today are required to take the lead when it comes to application security, but need more backup to do so. Detection tools can take developers part of the way, but to empower them through to remediation, organizations must provide them with developer-focused solutions that can help them to close the loop from detection to remediation.

    Once developers are alerted to a newly detected security vulnerability in their project, they need to validate it, assess its impact, research remediation options and perform the remediation path chosen. Currently, these are all time-consuming manual processes that require a level of skill and proficiency.

    With developers poised to face security head-on, organizations expecting them to fully address AppSec need to provide them with the tools that will easily integrate into their native environments and help them take vulnerability management one step further, enabling them to prioritize security alerts so that they can get to the most burning issues first and even automate their remediation process.

    — Ayala Goldstein

  • Software Compliance Teams Can Learn a Lot from DevSecOps

    Software Compliance Teams Can Learn a Lot from DevSecOps

    Many argue that application security should be the responsibility of a security team. However, while security professionals can contribute, developers are usually the only ones with the technical ability to fix software security vulnerabilities. The same goes for software compliance. When it comes down to it, only developers are equipped to build applications in compliance with specific software standards.

    Considering the tight deadlines for development teams, giving them additional duties can present challenges. To help developers deliver secure applications without slowing them down, many teams have adopted DevSecOps—which encourages integrating automated security testing into the DevOps workflows for every release.

    DevSecOps helps teams deliver more secure software faster, but what about more compliant software? Many teams trying to achieve software compliance encounter similar challenges as those trying to achieve software security. Luckily for them, they can use similar strategies.

    What Does DevSecOps Do?

    The fast, iterative software release cycles supported by DevOps workflows present hurdles for software security.

    In traditional approaches to securing software, testing occurs toward the end of the software development life cycle (SDLC), after an application’s construction. As a result, most (if not all) of the application is tested at once, and a long, daunting list of security issues is sent back to developers.

    However, many teams find this methodology incompatible with DevOps. Development teams don’t have the time—not to mention the budget—to stop whatever they’re doing to sort through a massive spreadsheet of issues.

    To solve this problem, organizations can implement DevSecOps by integrating security testing into the shorter, higher-frequency feedback loops of fast DevOps release cycles. Rather than running one big test after developers finish building an application, DevSecOps calls for automated security testing performed early and often. By helping developers check in more secure code, DevSecOps helps reduce the volume of issues QA must identify and send back to them.

    If development teams can integrate security testing into DevOps workflows, why not compliance testing?

    How to Apply DevSecOps Practices to Software Compliance

    While testing for security usually requires a different analysis than testing for compliance, development teams practicing DevSecOps can use a similar approach to compliance testing.

    Like traditional application security testing, compliance testing typically happens in the QA environment. A very rough application development and testing workflow looks something like this:

    1. Developers write the code for an application.
    2. QA tests the code while developers move on to another project.
    3. QA sends a list of compliance violations back to developers, requiring them to pause their current work to fix those problems.

    There is nothing technically wrong with this compliance testing strategy. However, this approach is frustrating for developers and costly if the list of issues is especially long. To resolve more compliance issues before an application is complete, teams can implement practices inspired by DevSecOps to help developers commit compliant code earlier in the SDLC.

    One of these strategies is to integrate automated compliance testing into DevOps release cycles. By testing the application in increments rather than all at once, teams can reduce the number of compliance violations per testing cycle. While it obviously requires higher-frequency testing throughout the SDLC, this approach has proven to be faster than waiting to find issues in QA.

    Another approach is to create a sandbox environment in the integrated development environment (IDE) where developers can run tests themselves. Testing their own code as they write it equips developers to check in cleaner, more compliant code, so compliance violations are less likely to show up in QA—or worse, production. This approach has the added benefit of familiarizing developers with code that leads to compliance violations.

    These strategies for identifying and resolving compliance violations are not meant to replace QA testing. However, by integrating compliance testing into multiple stages in the SDLC, teams will see fewer issues in feedback loops between QA and development—which better supports DevOps workflows.

    What Does This Look Like in the Real World?

    As with security testing, integrating compliance testing into DevOps release cycles requires new technologies and workflows, each with a different learning curve.

    Regarding technology, static analysis is growing as a popular option to help development teams build compliant applications. Coverage varies between static analysis tools, but in general, the technology can find issues in code quality standards, such as MISRA and CERT C/C++, as well as security standards, such as OWASP Top 10 and PCI DSS.

    The static analysis tool or any other technology that teams choose to address, software compliance plays an important role in the workflows they adopt. As discussed earlier, those hoping to keep issues out of QA will want to find solutions that can:

    1. Integrate into the quick feedback loops between testing and development.
    2. Scan code in the IDE as developers write it.

    Creating a more continuous cadence of feedback between testing and development could represent a significant shift in a developer’s day-to-day.

    While “DevCompOps” doesn’t quite have the same ring, development teams in regulated industries will find cost-cutting benefits by integrating compliance testing into DevOps release cycles.

    — Charlie Klein

  • DevOps World | Jenkins World 2019 Training is Best in Class

    DevOps World | Jenkins World 2019 Training is Best in Class

    Do you work on Jenkins pipelines? Are you responsible for implementing CloudBees tools in your development environment? Do you manage a DevOps team? Is your organization ramping up DevSecOps capabilities?

    If you answered yes to any of these questions, you should be attending the training sessions coming up at DevOps World | Jenkins World, a premier global event for Jenkins users and DevOps practitioners. The event is devoting two full days to educating attendees on the finer points of these topics listed above. The conference itself is taking place Aug. 12-15 in San Francisco’s Moscone Center and the training is scheduled for Monday and Tuesday (August 12 and 13).

    Conference attendees will have plenty to do throughout the week. The final two days will feature an agenda packed with keynotes, industry-focused thought leader sessions, an awards ceremony and, if that’s not enough, an after-party with a superhero theme. In-between sessions, there will be time to walk the expo floor, to get a glimpse of the latest and greatest technologies in the space and do some networking with some of the other 2,000 enthusiasts attending the conference.

    Training will be front and center early in the conference. Professionals with varying levels of experience—those just getting started and those with a substantial background in their subjects—can take advantage of trainings targeted just for them. They can sharpen their skills, gain new perspectives and walk away with certifications that will help them advance in their careers.

    Anybody who’s been in the business for a while will confirm: Well-trained teams are a big asset in DevOps. The field is expanding rapidly and changing every year, and DevOps practitioners need to devote themselves to continuous learning to keep pace with modern software development. At DevOps World | Jenkins World, they can learn about best practices ranging from authorization to security, build management and interfacing with cloud services.

    While training sessions are available to purchase at a nominal cost, attendees can receive a free Jenkins certification exam voucher—a $150 value—for the Certified Jenkins Engineer (CJE) and Certified CloudBees Jenkins Platform Engineer (CCJPE) exams. Attendees can choose to sign up for an onsite exam at the conference or use it at a later date.

    For a full rundown of the conference’s training offerings, check out the Training and Certification page.

    Now, let’s take a quick glimpse at what’s being offered.

    Jenkins Training

    Jenkins, the world’s leading open source automation server, is celebrating its 15th anniversary this year. A lot has changed during that time. A community has grown around the technology resource, adding new tools, new plugins and new best practices year after year.

    While the community dedicates itself to sharing information and educating its members, the DevOps World | Jenkins World conference provides the perfect setting to get the targeted training members to get the most out of Jenkins in their work environments.

    DevOps World | Jenkins World has four separate certification courses designed to build attendees’ Jenkins skills. There are introductory and intermediate courses that will position them to become more proficient in specific areas important to their own career development. Attendees can learn about Jenkins pipeline fundamentals—everything from the structure of a declarative pipeline to the use of features to finish the pipeline. They can also take advantage of an intermediate session with lectures about shared libraries and Docker agents and follow-up lab exercises. Jenkins Admin courses get learners started on the Jenkins dashboard and configuration practices and then branches out to cover more advanced concepts such as scaling Jenkins, managing different functions and more advanced uses of Docker and Kubernetes.

    There’s a second track that covers concepts connected to continuous delivery with Jenkins X. The Jenkins X project, introduced by CloudBees, provides a resource to educate community members on cloud-native processes. This course explores ways to take advantage of Jenkins X, showing attendees how to create a fully operational continuous delivery pipeline using containers, Kubernetes, Jenkins X and many other tools.

    CloudBees Training

    If you work with CloudBees technologies in a DevOps environment, the CloudBees Core Fundamentals course is a great place to advance your skills. Attendees need to take Jenkins Admin Fundamentals and Intermediate classes to really leverage the concepts covered here. They’ll learn how to optimize the CloudBees Core product suite to successfully scale CD and DevOps in their organizations. They’ll also learn about key proprietary features in CloudBees Core to enhance the capabilities of Jenkins, including enhancements for authorization and security that provide the control and administration needed to master key aspects of the pipeline.

    DevOps Training

    This course is more advanced—a certification for DevOps leaders of all kinds. To take the course, you don’t have to be an official leader of a DevOps team. Teams need leaders of all kinds. Whatever your position on the team—be it tactical of strategic, as a designer, implementer or motivator—you can play a leadership role. This course will teach the finer points of managing people and situations in a DevOps environment. It will build leadership skills—showing how to align and collaborate to break down silos and evolve the organization. It will present real-life scenarios and case studies to prepare team members to thrive in a fast-paced DevOps and Agile environment. Completion of this certification positions learners to complete the DevOps Leader exam successfully.

    DevSecOps Training

    It took a while for organizations to start integrating security into DevOps environments. Security was once considered an afterthought in—or even a hindrance to—DevOps processes. But now, DevSecOps is taking hold, and organizations need to build the skill levels to make the discipline successful.

    This course offers attendees the training they need to gain a DevSecOps Engineering Certification. It outlines DevSecOps as a concept, reviews key best practices DevOps teams need to adhere to and explains how DevOps security practices differ from other security approaches. The course will teach practical steps on how to integrate security programs into DevOps practices and highlight how professionals can use data and security science as the primary means of protecting the organization and customer. Completion of the course positions attendees to successfully pass the DevSecOps Engineering Certification exam, which is offered on the last day of class.

    Learn more about the training and workshops available. Then register with code DWJW20 and get 20% off your registration.

    — Jason Farmer

  • GitLab Research Reveals DevOps and Cybersecurity Disconnects

    GitLab Research Reveals DevOps and Cybersecurity Disconnects

    DevOps and cybersecurity teams have a complicated relationship, which impacts code quality, research shows

    Finger-pointing has long been the name of the game when it comes to cybersecurity failures. After all, who should be responsible when so-called bad code or bad practices are blamed for the latest incident? 

    A recent survey by DevOps lifecycle tool company GitLab reveals a significant disconnect between application developers and cybersecurity professionals—a disconnect that could only lead to more security woes and additional finger-pointing. GitLab surveyed more than 4,000 app development and cybersecurity professionals and brought some light to the complicated relationship between both. 

    For example, some 49% of the cybersecurity professionals surveyed claimed they struggle to get developers to make the remediation of vulnerabilities a priority. Sixty-eight percent of those same security professionals believe less than half of the developers they work with can identify security vulnerabilities before new code moves into the test cycle. 

    While cybersecurity professionals like to point the finger at the developer community, there are two sides to the survey. Almost 70% of the developers surveyed said that while they are expected to create secure code, they get little help or guidance from the cybersecurity experts with whom they work. Perhaps the fault lies with the lack of mechanisms to make cybersecurity a priority in many organizations. “We don’t have clear guidelines about security, so the different services present different levels of security,” noted one developer in the report.

    While developers and cybersecurity professionals may be at odds, the report also revealed there is plenty of additional blame to go around. Case in point is the revelation that many organizations don’t make cybersecurity a priority. Some 44% of those surveyed reported they are not judged on security vulnerabilities in their code. That creates an environment where developers don’t have to consider cybersecurity issues when writing code.

    With developers, cybersecurity professionals and even the companies they work for all at odds about the responsibilities of proper cybersecurity hygiene, one has to wonder how tomorrow’s vulnerabilities will be prevented.

    “Our research tells us that while most developers are aware of the dangers that vulnerabilities present and want to dramatically improve their security capabilities, they often still lack organizational support for prioritizing secure code creation, increasing secure coding skills and implementing automated scanning and testing tooling to make that happen sooner rather than later,” said Colin Fletcher, GitLab’s manager of market research and customer insights.

    Solving the blind spots around cybersecurity is going to take a different approach, one that further tears down the silos created around cybersecurity teams and development teams. There is a little bit of irony in that observation; after all, DevOps is all about tearing down silos and creating functional teams. 

    It’s also an irony not lost on those at GitLab. The company promotes solving the cybersecurity issues by adopting a good DevOps practice, where cybersecurity becomes an integral part of the DevOps process. According to GitLab, incorporating cybersecurity into DevOps will have the positive result of the combined team being three times more likely to discover security bugs before code is merged into operations.

    The report offers some significant conclusions that support GitLab’s claims. For example, some of the security top findings include:

    • Sec teams are three times more likely to discover bugs before code is merged with a good DevOps practice in place, and are 90% more likely to test between 91% and 100% of code than in an organization with early-stage DevOps.  
    • Nearly half of security pros surveyed (49%) said they struggle to get developers to make remediation of vulnerabilities a priority.
    • Half of security professionals said bugs were most often found by them after code is merged in a test environment.  
    • Mostly remote teams are 23% more likely to have mature security practices than primarily office-based teams.
    • Only 44% report security vulnerabilities are a performance metric for developers in their organizations.

    GitLab also revealed there is another consideration, one of ownership. According to the report: 

    No part of software development raises more issues about ownership than the subject of security. The idea that everyone is responsible for security might be the ideal but it can also be part of the problem as everyone can easily turn into no one. Security professionals often complain about being on the outside, while developers and operations teams can resent being told how to prioritize their work. Our survey responses indicate developers are taking more responsibility for security, but of course a lot of work remains. In fact, only 20% of those surveyed rated their organization’s security efforts as good, while 36% said they were fair and 24% said they were poor.

    — Frank Ohlhorst

  • 6 Reasons to Convince Your Manager to Send You to DevOps World |Jenkins World

    6 Reasons to Convince Your Manager to Send You to DevOps World |Jenkins World

    This year’s DevOps World | Jenkins World will take place Aug. 12-15 in San Francisco, at the Moscone Center.

    Now, chances are you don’t need any real convincing to attend this event. DevOps World | Jenkins World is, after all, the premier annual conference for DevOps- and Jenkins-related content. You’ve experienced it yourself, or heard others talking about past years’ events—how the conference is packed, year after year, with sessions given by experts, multiple keynotes from industry leaders, hands-on training, plenty of time for networking, a themed after-party and all kinds of other cool things to take advantage of. This year, the event is going to be bigger than ever.

    But, maybe you need a little help convincing your manager to authorize your trip. If so, we’re here to help. We’ve pulled together a list of selling points you can bring to your manager to show the incredible value a trip to DevOps World-Jenkins World can generate.

    You Can Turn Yourself into a DevOps Leader

    As we all know, DevOps is more than a technology, more than a process; it’s a culture that needs to be nurtured and fed. It needs DevOps leaders to advance that culture. Sending you to DevOps World-Jenkins World can turn you into a DevOps leader.

    You can start by taking a DevOps Leader course that will equip you with the skills and knowledge you need to successfully complete the DevOps Leader certification exam. But it goes beyond one specific course. There are other courses focused on DevSecOps, Continuous Delivery with Jenkins X and best practices connected with the use of CloudBees Core. There are sessions addressing topics ranging from DevOps culture to DevOps theory versus practice. Immersing yourself in all the DevOps content here will raise your knowledge level to new heights.

    You’ll Sharpen Your Automation Skills

    If your organization is using Jenkins, your manager knows how important is the role technology resources play in automating key aspects of the software delivery process. Management is constantly pushing teams to brush up on Jenkins and related DevOps tools—how they work, how to get the most out of them, how to fix problems, etc. Any resource that will help advance the collective knowledge of the group will be welcomed with open arms.

    DevOps World | Jenkins World offers a treasure trove of educational sessions that will help you advance your CI/CD knowledge and Jenkins expertise. Training includes intro and intermediate sessions on Jenkins administration and Jenkins Pipeline. The courses build on each other and propel learners toward the expertise needed to pass the Certified Jenkins Engineer exam. You’ll be bringing back knowledge you can apply to your organization on day one.

    There are also sessions on automated release orchestration and on a number of the DevOps tools and technologies widely used throughout the industry.

    You’ll Hear From the Masters

    It’s one thing to watch a video or read a book by one of the industry’s giants. It’s quite another to see the expert live and maybe even have a conversation with them during the show. DevOps World | Jenkins World offers this kind of access. Jenkins founder Kohsuke Kawaguchi (KK), CloudBees CEO Sacha Labourey and Redmonk analyst James Governor are some of the speakers who are sure to enlighten and entertain. Bring home stories of how KK challenged the crowd to think differently or what Redmonk’s Governor really thought of a commonly held DevOps practice.

    You’ll Gain a New, Broader Perspective

    With more than 100 sessions to choose from, it goes without saying that you can learn a lot of new things. Beyond the basic workshops and presentations, you can take in talks about everything ranging from DevOps in the public sector to machine learning in “continuous everything” environments. Want to hear the 10 attributes of the DevOps elite? How the auto industry is embracing continuous delivery? How Verizon followed a high-availability model using Jenkins? It’s all here. And you can bring the knowledge back to your organization, sharing it in one-on-one meetings, in presentations or in general thoughts about initiatives for next year.

    You’ll Build Your Network

    What happens when you put 2,000 or so DevOps enthusiasts in one place? They’re going to do the same thing sports fans and car fanatics do: talk loudly and animatedly about the topic they love. DevOps World | Jenkins World attendees will share stories about epic fails and debate a long list of best practices.

    Know what else they’re going to do? Exchange Twitter handles or vCards. This can be hugely valuable, not just to you but to your organization. Imagine your manager, needing help, asking you if you know anybody who knows this technology, understands this issue or has access to some hard-to-find resource. You tell your manager you can help; you met someone at the show who knows all about this. You picked up dozens of Twitter followers now engaged with you or your company and would love to help.

    You’ll Be Giving Back to Your Organization

    Building on the last item: Your manager wants this trip to be valuable—for you, for her and for the organization. You want the same thing. It’s your job to highlight how you plan to use your time wisely at the show to directly benefit your company.

    Get creative. Talk about frustrations, pain points, staffing needs, business opportunities—you name it, you can solve it. DevOps World | Jenkins World has the content and the structure to be a resource for your organization. Detail your expenses, and stress how this is a work trip designed to enhance the organization’s overall knowledge base.

    When you have successfully made your case and received approval to attend, register with this code: DWJW20 and get a 20% discount off your registration.

    — Heidi Gilmore

  • 3 Reasons Why Ephemeral Access is Best for DevOps

    3 Reasons Why Ephemeral Access is Best for DevOps

    Recently, we worked with a customer, MOST Digital, whose developers were struggling with a common workflow challenge we hear from many companies.

    The company is in the software robotics automation space—it essentially makes little robots that automate all sorts of business processes for a company, such as HR report filing or routine emails. MOST Digital developers need access to customer environments to fetch data, often jumping in and out of on-premises and cloud platforms to do so.

    The problem was developers had to use client-specific jump hosts and VPNs to transition between IT resources. The process was slow, complicated and difficult to manage, which made life more difficult for MOST Digital’s team. Projects were delayed as they had to wait to receive help from each client’s IT organization.

    “This wasn’t what MOST Digital wanted for their team,” said Sami Säisä, director and head of strategic development at MOST Digital. “We want to provide them the best environments and best tools that there are available.”

    It’s a common refrain we hear from many customers, and it makes sense. The easiest way to frustrate a developer is to throw obstacles into their workflow. Unfortunately, most common secure access solutions create obstacles, and it’s not just jump hosts or VPNs. Even privileged access management (PAM) solutions, which are supposed to simplify and centralize IT credential management, are traditionally too bulky, complicated or non-intuitive for modern workflows. That encourages developers to bypass PAM altogether, which creates a major security risk.

    So, what’s the best way to overcome the complexity brought on by credential management? Well, why not just get rid of permanent credentials?

    Ephemeral certificates are a modern form of secure access that are temporary, time-based and automatically expire. Here’s why they’re a better solution for companies that want to keep modern developers happy.

    Ephemeral Certificates Offer ‘Just in Time’ Access

    Developers are building and coding in a world that emphasizes speed, agility and elasticity. They’re taking advantage of state-of-the-art tools meant to make it faster and easier to do work. They’re taking advantage of modern, hybrid IT environments that combine multiple cloud infrastructures in an attempt to find the most effective mix of resources for development and deployment.

    The last thing they want are processes that slow down workflow. Unfortunately, secure access today often means doing just that: slowing down and stopping to manually input credentials across environments. Developers might also share credentials among each other to try and speed up work, but that creates yet another security risk.

    Traditional PAM solutions don’t make the process any easier. Those tools create a central vault to manage an organization’s secure credentials. Privileged tech users, such as developers, have to use them to access and authenticate their credentials. PAM grants access per user and per host, so a new, permanent credential needs to be created every time a new developer, contractor or contributor needs access to a new IT resource.

    However, most PAM tools were not built with the workflow of the modern developer in mind, so they slow things down while also encouraging loopholes and workarounds that compromise organizational security.

    Ephemeral certificates overcome all of this by eliminating manual credential inputs. Gartner refers to these as just-in-time access, because access credentials are created on-demand automatically and require no installation, configuration or updating. In other words, they free developers to focus exclusively on the work they do best.

    Ephemeral Certificates Eliminate Bad Habits

    Rather than deal with all of the typical secure access challenges, some developers will often bypass PAM solutions altogether, instead choosing to spin up their own SSH keys to access the IT resources they need. Those keys exist outside of the PAM solution—they are untracked and unmanaged.

    Not only is it a policy violation to have developers find workarounds for IT-approved security practices (not to mention a huge waste of the investment in a PAM solution), but it also creates a security risk.

    The best way to encourage policy adherence is to make your policy easy to follow. Developers won’t bypass your security solution if it’s easy to use, and ephemeral certificates are inherently simple.

    There Are No Credentials to Misplace–Or Have Stolen

    If every developer is creating their own SSH keys to access IT assets and no one’s keeping track of them all, what happens if one is lost or when that developer leaves the company? Suddenly, there are keys laying around that could be scooped up and used as an all-access pass to systems in your environment.

    How do you monitor and audit this type of shadow IT access? How do you trace non-policy compliant access from development to production? How do you prevent developer access to sensitive data?

    Ephemeral certificates are inherently more secure because they are temporary, only existing for the period during which access is required, and automatically expire as soon as you are done using them.

    As a result, there are no credentials to lose, misplace or steal, leaving fewer old credentials lying around for someone to take advantage of down the road. On top of that, ephemeral certificates don’t leave user-specific access credentials stored on target servers, so if someone does get access to your target server, they won’t be able to find any credentials that could be used to hop to other systems.

    Ephemeral Access Is a Step Closer to DevSecOps

    From security to IT management, there are lots of reasons why ephemeral certificates are a better solution for businesses. But the single most impactful use case is making your team’s life easier.

    Want to frustrate a developer? Throw some obstacles into their workflow. But if you want to keep your developers busy on value-driving activities, get rid of outdated and unmanageable workflows. They’ll thank you for it later.

    — Markku Rossi

  • Product IT Operating Model: The Next-Gen Model for a Digital World

    Product IT Operating Model: The Next-Gen Model for a Digital World

    Digitization presents many new opportunities for businesses to create value. At the same time, it forces IT to rethink the way it operates. Modern CIOs need an operating model that understands the blurring lines between IT and business and is designed for agility and speed. The product-centric IT operating model is rapidly emerging as the answer.

    What does the model entail? In the product IT operating model, product lines are funded based on their strategic value to the organization, from the top-down, and are supported by dedicated management and delivery resources. The entire product team is measured on a common set of goals, which include customer experience, time-to-market, efficiency improvements, quality of software and availability and reliability of production environments.

    5 Dimensions of Product IT Operating Model

    Adopting a product IT operating model requires organizations to take an integrated approach toward product-based development and embark on a journey of continual improvements. While scaling agile DevOps that aligns business outcomes with engineering effort, enterprises must focus on these five key dimensions:

    1. Organizational Change Management (OCM): Successfully transitioning from the traditional IT operating model to a product-based development approach requires organizationwide change management. An experienced IT service provider, can prove to be a key ally in ensuring a smooth transition.

    2. Culture: Culture is an intrinsic characteristic of any organization, and instituting small but effective cultural changes coupled with OCM is the right approach to transition, rather than a “big bang” change. That’s also what some of the well-known enterprises across industries are doing.

    a. Teams and Collaboration: The alignment of large teams across multiple organizational groups delivers to a common plan on the pace of change and helps to continuously embed innovation and experimentation for improved services.

    3. Structure: Product-focused and highly talented teams across design, architecture, DevOps and operations are key to enhancing business capability. By measuring the entire team on same set of goals, it is easy to enhance customer experience, efficiency and quality of software while creating a stable production environment.

    Structure also means aligning traditional application portfolios to specific business outcomes and bringing together all the capabilities and resources required for an organization to deliver on its business outcomes.

    4. Technology: If business models, organizational structures, people and ways of working are the gears that run the enterprise IT engine, technology is the grease that enables this engine to run smoothly, without friction. Two key aspects of technology include:

    a. Application Programming Interfaces (API): API-based architecture provides an extensible framework of building blocks, which in turn can be used to build powerful applications or software products. Easy maintenance is a hallmark of API-based architecture, as it can be quickly migrated further to any other target architecture.

    b. Cloud, Microservices and Containers: Modern organizations need on-demand scalability. Cloud and microservices enable just that without disturbing ongoing business operations. However, it is important to first understand an organization’s product vision and road map, business priorities, competition, pace of market transition in their area of business and industry trends before choosing cloud or container-based infrastructure.

    5. Process and Automation:

    a. Agile Delivery Model: This is a critical prerequisite to building a minimal viable product (MVP), ensuring rapid delivery of critical enhancements or delivering a suite of product features in appropriate increments. Industry-standard agile practices such as LeSS and SAFe should be used, as they allow complete flexibility to tweak the model on the fly.

    b. DevOps and DevSecOps: A DevOps culture is fundamental to adopting a product IT operating model. Continuous integration and delivery (CI/CD) require DevOps to be fully interwoven into the software development life cycle (SDLC), along with the right tools and governance mechanisms. This ensures high-quality products are delivered within short deployment lead times, along with the ability to fix production issues with low mean time to restore (MTTR) and ensure minimal to no change failure rate. DevOps also enables new-age practices such as automated testing, self-service access to infrastructure and automated performance management.

    DevSecOps goes hand-in-hand with DevOps. It ensures security aspects are built into the products across the delivery pipeline, so the products are not only fault tolerant but also fool-proof, to a large extent. An experienced DevOps team builds and integrates security tools, solutions and processes to safeguard the organization.

    c. Test Automation and Test-Driven Development (TDD): By integrating test automation into the development process, the product IT operating model allows organizations to create high-quality and quickly deployable products. Additionally, TDD enables governance to be integrated into the delivery pipeline by developing quality code in line with test cases written to describe user requirements more precisely. Tests are fully automated to ensure quality of code.

    d. Service Health: With KPIs focused on the financial health of engagement, it’s easy to set a budget based on business capabilities and product levels to meet business goals effectively. The KPI framework encompasses key KPIs such as business, financial, learning and innovation and employee engagement outcomes, while staying flexible enough for different contracting models.

    Delivering Value in a Changing Business Environment

    Digitization mandates that IT deliver on three important aspects: Improve time to market, optimize costs and increase quality.  Adopting a product IT operating model helps IT deliver on the mandate by enabling a fail-fast way to deploy software quickly and cost-effectively, without sacrificing quality. However, given the extent of change involved in the shift, it is not something that can be achieved overnight. It must be underpinned by a journey of cultural change and continuous learning, using tools such as design thinking-driven, persona-based change journeys, alignment workshops and targeted campaigns and communication. Partnering with an expert system integrator can help organizations jump-start the process and ensure on-track transition with minimal disruption to business.

    — Gagan Jain

  • GitLab Survey Surfaces Major DevSecOps Challenges Ahead

    GitLab Survey Surfaces Major DevSecOps Challenges Ahead

    A report based on a survey of 4,071 software professionals published this week by GitLab, a provider of a continuous integration and continuous deployment (CI/CD) platform, found that while appreciation of the potential value of DevSecOps best practices is high, the ability to implement those practices is uneven at best.

    According to the survey, half of the respondents reported that security vulnerabilities are discovered mostly by the security team rather than developers after code is merged and in a test environment. And, when cybersecurity professionals participate in a DevSecOps process, the survey found those organizations are three times more likely to discover bugs before code is merged. In addition, a full 90% of those organizations are more likely to have tested between 91% and 100% of their code early in the development process.

    Obviously, that’s better than discovering them after they’ve been deployed in a production environment. On the downside, however, nearly half of security professionals participating in the GitLab survey (49%) said they struggle to get developers to make remediation of vulnerabilities a priority. That challenge may reflect the overall maturity of the DevSecOps practices in place. For example, only 25% of developers participating in the survey rated their security practices as being good. That compares to only 20% of security professionals who rated their processes as good. Only 14% of respondents said they are relying on application security tools to test more than 91% of their code. A full 44% are using these types of tools to test less than a third of their code.

    Priyanka Sharma, director of technology evangelism for GitLab, said the survey makes it clear that DevSecOps is now officially a thing in the enterprise. However, only 44% of the survey respondents said that security vulnerabilities are a performance metric for developers in their organizations. As such, it’s clear there is still a long way to go before anything approaching DevSecOps nirvana is likely to be achieved. In fact, Sharma noted building and deploying more secure applications may require organizations to slow down the rate at which applications are being built, at least initially.

    The GitLab survey makes it clear most organizations are still struggling with mastering DevOps. Only 28% of developers said they feel good about their organization’s level of DevOps sophistication, while less than half (45%) said they have been able to implement continuous code deployment at least somewhere in their organization. That level of adoption suggests there still is plenty of opportunity to refine DevOps processes that are not fully ingrained. In fact, it appears most organizations are still trying to master agile development methodologies—more than half of the respondents said they employ Scrum (54%) as their application development methodology, followed by Kanban at 37% and DevOps at 36%.

    Ultimately, most organizations will have no choice when it comes to embracing DevSecOps. There simply are not enough cybersecurity professionals available to secure every application on their own. That means developers will need to assume more responsibility for cybersecurity, regardless of whether they like it. DevSecOps processes will be required to validate whether developers have implemented all the security patches and controls required. Anything less than that going forward will be deemed as nothing short of reckless—which, as any lawyer will gladly share, means much higher penalties for everyone involved.

    — Mike Vizard

  • Transforming the Security Team Into a DevOps Partner

    Transforming the Security Team Into a DevOps Partner

    Securing DevOps environments is an increasingly important concern for chief information security officers (CISOs) and security teams. While developers often recognize security is important, it is not their top priority. More typically, the DevOps team prioritizes delivering new capabilities and features to the business and customers, often as part of a larger digital transformation initiative. And, developers often view security as something that will slow down deployments.

    Security teams usually have limited DevOps knowledge or expertise. Too often the result is that DevOps adoption begins and even takes hold inside an organization before the security team gets involved. Consequently, security vulnerabilities are not always adequately addressed in DevOps environments and can drive unnecessary risk.

    Integrating Security in DevOps

    The priority is for the security team to take the lead in integrating security into the DevOps processes before poor practices become entrenched. But as both teams are often siloed and don’t tend to work collaboratively, how can security teams better engage, energize and collaborate with their DevOps counterparts to strike the right balance? In a nutshell, how can organizations bring their DevOps and security teams into alignment and establish collaboration for stronger overall security?

    There are a few crucial steps to take to achieve true integration of security and DevOps.

    1. Establish the Requisite Skills to Get in the Driver’s Seat. Effective collaboration requires effective communication. While developers write the actual code, it’s important for security teams to gain knowledge about programming languages along with how applications are built, tested and deployed automatically. This will help them have more meaningful discussions and credible conversations. Security professionals can start by learning some of the fundamentals: PowerShell, Python and Rust, as well as how DevOps tools use REST calls and containerization technologies–particularly Docker and Kubernetes.
    2. Make it Easy for Developers to Do the Right Thing. You can’t be the manual cog in their completely automated process. Make it easy for developers to do the right thing by training them in secure coding practices and implementing a self-service model for security capabilities. For example, you could provide security policy as code that can be integrated into the developers’ automated processes.
    3. Establish Effective Ways to Collaborate. Set up formal systems to ensure DevOps practitioners understand security risks and implement good security practices across the organization. Consider how best to deploy security resources into existing or new organizational models and structures. This includes establishing centers of excellence, community leaders, security champions and embedding security team members inside development teams.
    4. Get Developers to Think Like Attackers. Educate DevOps teams on specific attacker tactics, show how sample code modules could expose secrets and provide examples as user stories. For example, “As an attacker, I would scan the organization’s code repositories looking for secrets.” Take the team through a penetration testing exercise or engage a red team to demonstrate how an attacker would compromise a CI/CD pipeline.
    5. Adopt Agile and DevOps Methods. Security should begin utilizing agile and DevOps methods within their own teams, not only to gain a deeper understanding of DevOps methodologies but also to achieve greater efficiency by automating tasks or delivering capabilities in smaller increments more frequently.

    The bottom line is, it is crucial to understand how other enterprises approach secrets management challenges across DevOps and cloud environments. This can help encourage collaboration and help fast-track the security team’s own efforts. Ultimately, this will ensure agility is not just implemented for the sake of innovation, but companies reflect on their processes and prioritize security to make the most of their transformation.

    — Josh Kirkwood

  • DevOps Chat: Mayhem Testing With ForAllSecure

    DevOps Chat: Mayhem Testing With ForAllSecure

    Secure software depends on people finding vulnerabilities and deploying fixes before they are exploited in the wild. This has lead to a world of security researchers and bug bounties directed at finding new vulnerabilities.

    As dedicated as security researchers are, there is a vast ocean of software in existence, waiting for someone to find and exploit the next security vulnerability for profit or nefarious uses. With autonomous vehicles on the horizon, is there an autonomous solution to finding and fixing software vulnerabilities?

    Enter DARPA Cyber Grand Challenge winner “Mayhem,” created by a team of researchers from Carnegie Mellon University who spun out security startup ForAllSecure. And they have a BHAG (Big Hairy Audacious Goal). “Our vision is to check the world’s software for exploitable bugs so they can be fixed before attackers use them to hack computers.” Mayhem has moved on from capture the flag contests to observing and finding vulnerabilities in DoD software and is working its way to corporate systems.

    In this episode of DevOps Chats we talk with David Brumley, For All Secure co-founder and CEO, and CMU professor about the technology behind Mayhem, how it observes software as it executes and injects changes to effect and observe new and potentially exploitable behaviors. More information about Mayhem is also available at www.forallsecure.com.

    As usual, the streaming audio is immediately below, followed by the transcript of our conversation.

    Transcript

    Mitch Ashley: Hi, everyone, this is Mitch Ashley with staging-devopsy.kinsta.cloud, and you’re listening to another DevOps Chat podcast. Today, I’m joined by David Brumley, CEO at ForAllSecure. David is also a professor at CMU. He’s currently on leave. The topic that we’re talking about today is called Mayhem behavior testing—it ties back to David’s work at CMU. So, David, welcome to DevOps Chat.

    David Brumley: I’m happy to be here.

    Ashley: Great, we’re happy to have you on the podcast. Would you start by just introducing yourself a little more fully—your background, maybe a little bit about some of the research and how that led you to form ForAllSecure?

    Brumley: Yeah, absolutely. When I got out of undergrad, I was a computer security officer. My job was to chase intrusions on the Stanford network and try to help people fix them. And at the time, I got pretty frustrated with the idea that we were always behind attackers, that I couldn’t find vulnerabilities first or get the fixes deployed.

    I actually went back to grad school, got a Ph.D. and really made that my work since 2003 on how do we go about finding vulnerabilities before attackers and just as importantly, how do we get those fixes fielded? Because it’s not just about finding the vulnerabilities, it’s about how quickly we can get those in place.

    I’ve been working on that, I’m a tenured professor at Carnegie Mellon, and for the last three years, been working on commercializing it.

    Ashley: Excellent. Well, an entrepreneur and a professor, and it’s great to see that your research has led you to kinda bring this out to market. That’s exciting. So, tell us, what is Mayhem? What is Mayhem or behavioral testing?

    Brumley: Yeah, what Mayhem does, we call behavioral testing. So, behavioral testing is about watching an application as it executes and learning from that execution and then trying to come up with a new input that would cause the application to do something different. And you do this again and again and again, like hundreds of times per second, with the idea that if you can learn the behaviors of a program and you can start driving it to new behaviors, you’ll, one, come up with a test suite for the program, that’s important for the DevOps part and how you get things out quickly, and second, things like vulnerabilities and exploits that trigger vulnerabilities are just triggering a particular behavior. So, you can automatically generate inputs that trigger these. At one point, people were saying we were automatically generating exploits with this technology.

    Ashley: Interesting. I’m pretty sure that it’s not the same thing, but it sounds like a more thoughtful and learned approach to what we know as chaos testing from the Chaos Monkeys from Netflix, et cetera. But you’re really picking specific behaviors, building a profile of the application, and then looking for new behaviors that you can test against it?

    Brumley: That’s what we’re doing, and so, there’s really kind of two technologies people may have heard of. One is called fuzzing. So, fuzzing is about running the application again and again and again. And it uses heuristics to pick those inputs, and one of the things we built is a way to monitor that application as it runs and to inform the fuzzer on how to come up with new inputs that would get different behaviors.

    The second that we did is, we really took a page from surprisingly formal verification. So, the formal verification was trying to prove a program was safe. What we tried to do is use those same techniques to prove where a program is unsafe, and our proof creates an input that triggers the unsafe property.

    So, we use these two techniques—fuzzing, symbolic execution and a few others and a portfolio approach to try to come up with behaviors that are exploitable.

    Ashley: Interesting. Do you do this in a production environment, in a test environment, in both? How do you approach this?

    Brumley: For a product, we always do it in testing. We think it’s important to have these techniques out there in testing so that you can find them before attackers. We have done some simulations in production. One of the things we participated in was, DARPA had a big autonomous Cyber Grand Challenge. So, we fielded it there, but we think the market would be in the testing environment.

    Ashley: Mm-hmm. It would definitely make sense—makes more sense there. Say a little bit more about fuzzing and how that exactly works. Is it the software that’s doing the variations, or are you introducing variations to that from what you learn?

    Brumley: We’re introducing the variations, so the idea is, an exploit for a program is just an input.

    Ashley: Mm-hmm.

    Brumley: And, you know, test cases are just inputs. So, you run the program on an input and you watch how it executes. Like, you see it executes this system call, that system call. It covers these branches. And you use that to learn a new behavior or guess a new input. And then the fuzzer will use a heuristic to pick that new input, with the idea it should trigger a new behavior.

    Ashley: Step back just for a moment, you’ve talked a little bit about Mayhem and the technology behind it. You’ve stepped out of CMU to set up this company, ForAllSecure. How did you get that started? Are you working with a particular private sector, government sector? Sounds like something that might be interesting to the government side of things, too.

    Brumley: Yeah, we got started by really participating in this, as I said, DARPA project. So, they have Grand Challenges every so often. One was the self-driving car contest. This was, like, a self-driving car for a computer security contest. We won that and that gave us our first $2 million, so that was, like, seed funding from the government.

    Ashley: Excellent! Wow, that’s awesome.

    Brumley: Yeah. And so, we’ve been working to bring it into the government so it’s used in pretty much every service and in the IC right now to try to look for vulnerabilities in weapons platforms as well as in software the government might be using to try to fix it before attackers can break into it.

    Ashley: Mm-hmm.

    Brumley: About, oh, six months ago, we then went and raised money from NEA to help transition this from just a government tool to something in the enterprise section as well.

    Ashley: Mm-hmm, so you’re also beginning to work with the private sector, then?

    Brumley: Yeah, we’re working—starting to work with the private sector. It’s really kind of an interesting difference between the two.

    Ashley: Oh, there’s a lot of difference. [Laughter] Yes. Highlight what you see the difference as. I have some experience with both, also.

    Brumley: Well, I think that the private sector, it’s harder for them to put a value on finding a vulnerability and fixing it quickly while, in the DoD, it’s really easy. That mission didn’t succeed, which is a big deal.

    Ashley: Mm-hmm.

    Brumley: So, I think that’s one difference. I think the second difference as we see going to market is, in the DoD, they care a lot about checking legacy systems, because they still have to maintain them. And if you think about it, lots of vehicles, airplanes, trains—things like that. And in an enterprise, they care about things that were developed in the last two or three years only. And so, they’re just kind of products in different parts of the life cycle.

    Ashley: Yeah, interesting. You also have many layers of different parties involved in the government sector—contractors, subcontractors, primes, et cetera. So, you’re dealing with lots of layers of companies that are working as part of the government team.

    Brumley: Yeah, working with the government is definitely, it’s a chore until you get into the groove and you realize a lot of the, what you perceive are barriers, are actually just regulations put up to protect taxpayers from complete abuse. So, it takes a long time, it takes about nine months to get anything really going from start to scratch in the government. But once you kind of get that cycle, it goes forward pretty quick.

    Ashley: Yeah, that was my experience, too. It’s an investment, but once you get going, it’s great.

    Brumley: Yeah.

    Ashley: So, talk a little bit about where you are in the product life cycle? Do you have product in the market? Is Mayhem publicly available? Are you alpha, beta? Give us an idea of that.

    Brumley: Yeah. So, within the DoD space, we have Mayhem that you can buy starting in July this year—so, pretty close. So, we have a number of beta installs, people are happy, and we’re gonna be switching over to general availability pretty quick.

    Ashley: Mm-hmm.

    Brumley: In the commercial market, we’re taking it a little bit slower, because some of these differences I’ve discussed. They use different application stacks, they’re often concerned with much newer software than old software, they often use different languages.

    And so, that, we’re looking for design partners. People who wanna take Mayhem, what’s working in the DoD, what’s working in places like aerospace, and see if it works for them and figure out what we need to do to make it a really good fit.

    Ashley: Mm-hmm. So, you’re spending a lot of time with customers and potential customers really learning what the commercial sector is looking for or can benefit from.

    Brumley: We’re learning what they’re looking for. We’re also trying to understand, like you said, when you go to market, it’s kind of interesting in the DoD who the buyer and who the user are and trying to understand that in the commercial space. Like, it’s kind of fascinating to me in DevSecOps, it’s almost always the security team that’s the buyer but it’s the development team that’s the user.

    Ashley: Mm-hmm. Yeah, exactly. And that’s an interesting dynamic there, it’s, you know, the DevSecOps conversation, one that we helped facilitate bringing together through a lot of the activities at staging-devopsy.kinsta.cloud.

    I’d love to hear a little bit about, so you said you’re not commercially available yet in the commercial or private sector, but you are entertaining companies to work with? Is that true?

    Brumley: That is. So, we’ve worked with a large aerospace vendor that makes airplanes. Can’t say much about that. We’ve been able to really help them find some flaws in some software that they use as well as build up test suites for them so that when the developer does push a fix, that can be more rigorously tested, working with a Fortune 100 company, and then some IT infrastructure people.

    Ashley: Mm-hmm. I could see, for example, data center providers being another place that it’s gonna really benefit from.

    Brumley: Oh, absolutely. Anyone who has something that’s extremely high value like a web server that, if it gets compromised, your entire business is at stake.

    Ashley: I’d love to hear your thoughts about how you fit this into the DevOps or the DevSecOps pattern or cycle. How does this happen? Where do you build it into?

    Brumley: Yeah, so, from what we can see in research right now in a lot of DevSecOps, it’s really kind of a primitive stage where people want to run a scan before they field software. To me, this is insane. I don’t know any attacker who runs a commercial product and a scan and then says, you know, “Here’s the new zero day” or, “Oh, better not go after that, the scan was okay.”

    Instead, what they do is, they’re always trying to break into that software. They’re always trying to learn from what hasn’t succeeded and come up with attacks and succeed. So, Mayhem is like that. So, the idea is, it’s more of asynchronous testing. You’re gonna push as part of your DevOps cycle through, you know, things like making sure you’re not using old versions of libraries. But then, you’re gonna launch a process that, for the lifetime of that product, tries to hack it in the background.

    I think that’s really kind of the conceptual shift that we think needs to be made is to stop thinking of security as a scan you do once, and actually expect it to work, to something that’s always going on in the background.

    Ashley: I’m gonna shift just like we do with testing, we’ve moved into continuous improvement, continuous testing do the same for DevSecOps where this is running maybe on multiple versions of the product and test environment all the time.

    Brumley: Absolutely, as well as all the dependencies. If you look at Google—so, Google runs fuzzing, one of the technologies that I talked about earlier, on Google Chrome. And they found 12,000 new vulnerabilities in the last three years, and each one was accompanied by a test case, so zero false positives. And one of the things this has allowed them to do is get ahead of attackers, because they’re finding those flaws so quickly with their automated, always on infrastructure that I’ve talked to people who try to participate in bug bounties. And by the time they report it, it’s already fixed.

    Ashley: Mm-hmm. I mean, aren’t the bad guys also doing fuzzing themselves, so you’re at a disadvantage if you’re not?

    Brumley: Absolutely. Every top notch hacker I know uses fuzzing extensively as one of their techniques. I mean, this is assuming you kind of do the base, like, did the person forget to set a password? Always check for that first, right? But after that, after that base level, you’re gonna do fuzzing, especially after high value targets.

    Ashley: Talk a little bit about where you see things going next. You’re kinda testing with the commercial market, you’re heavily engaged with the federal market. What happens next in terms of the product roadmap?

    Brumley: Well, the next question that we have in terms of the product roadmap is, how do we close that life cycle from finding a vulnerability to having a fix fielded. So, some app site companies, what they wanna do is always add on that next language support so that they can support a larger and larger set of languages.

    Ashley: Mm-hmm.

    Brumley: For us, we’re really looking at C, C++, Java, Python—the core languages used by infrastructure Go and Rust. And we want to be able to do deep analysis in these languages and then be able to help automatically suggest fixes and actually, for DARPA, we proved that the computers could automatically patch. So, it could automatically patch binary programs, and it could assess whether that patch would have any business impact, and field it, if not. And so, that’s really what we’re trying to do, and we’re going language by language as opposed to trying to cover all the languages at once.

    Ashley: Interesting. What’s your top pick in terms of languages you’re looking at first?

    Brumley: So, the top one that we started with is C and C++. And that’s been a bit surprising to people, because it’s an older language. I can tell you why we picked it.

    Ashley: Okay.

    Brumley: The reason that we picked it is, regardless of what language you choose, you’re gonna be calling out to C and C++ code. In Java, you have JNI calls. In Python, you have, you know, as part of TensorFlow, if you’re doing machine language, everyone goes to C/C++ or a compiled language when they want performance.

    And so, if you wanna analyze these applications completely, even if it’s Java or Python, you have to be able to analyze those components as well. So, we’re kind of working our way up.

    Ashley: Yeah, I was gonna say, it sounds like you’re working way up the stack into the scripting languages.

    Brumley: Absolutely. The second reason is, when you look at really critical infrastructure out there, it’s still primarily developed in C and C++. So, you know, I, like many people, have probably put up a Flask or Python website, it’s really quick to do, it’s online—you definitely don’t want it hacked. But when you start talking about a car or an airplane or a power plant—these are also on C/C++. And so, just from a safety point of view, you have to cover those.

    Ashley: Interesting. Do you foresee, looking kinda down the road—I’m not asking you to announce anything officially, but do you see that you might be working with either the patch management companies, the vulnerability scanning companies as a complement to them? Would this be something that potentially displaces them? How do you see that future unfolding?

    Brumley: Yeah, I think people who detect known vulnerabilities are complementary to us. So, the way I think of it is, there’s really two types of security companies out there. There are those who find new vulnerabilities, and there’s those who check for old vulnerabilities.

    So, you have, for example, Tenable, which is a network scanner that goes and looks for known vulnerabilities. You have software component analysis, which looks for known vulnerable versions of libraries and other things, right? So, those are pattern matchers in some sense.

    We’re not one of those companies. That’s someone that you would partner with. What we’re doing is, we’re finding new vulnerabilities. And so, this is more like a typical SaaS or DaaS type solution.

    The other sort of people that we’re looking to partner with are the patch management. So, one of the cool things that we can do is, when we find a vulnerability, we automatically are building a test suite as well, just part of the process. So, when there’s a patch we can replay it, and we can tell you things like, “Hey, have any of the previously passing test cases stopped working? Has performance dropped?” as well as, of course, where the bug’s fixed.

    Ashley: I definitely can see the partnership alignment there. If you had to paint a future of what success looks like for, both for you and ForAllSecure, what would that be?

    Brumley: I think we’re really motivated by this vision that we wanna automatically protect and check the world’s software. And so, we wanna close that cycle and make it autonomous. And we’re making, actually, pretty careful design decisions as we do that.

    So, I think a lot of people talk about, you know, big startups, billion dollar businesses—that’s not really our goal. Our goal is, we want to make it so the time from when we detect a vulnerability to there’s a patch that’s tested and ready to field is seconds. That, to us, is success.

    Ashley: The billions will come later, right? [Laughter] That’s if you’re passionate about that core problem.

    Brumley: I think so. Because this problem, we were talking about DevSecOps. Like, DevSecOps, the problems facing DevSecOps face every system administrator if we go back in the world. In Silicon Valley, we think of SREs and DevSecOps, but there’s this huge nation full of just system administrators who wanna know, “If I update it, is it gonna break? Do I need to update it?” And solving those problems for those people is what’s important for us.

    Ashley: Do you have any demonstrations coming up, either online or you’re gonna be at some conferences? Is there a way for folks to see this yet?

    Brumley: Yeah, so, we’re gonna be at Black Hat and we’re happy to demo it there. We’ll have a booth and a room. We also have a number of online videos. If you want to see the fully autonomous, in its splendor system, there’s definitely videos of the DARPA Cyber Grand Challenge as well.

    Ashley: Going back to the original challenge.

    Brumley: That was the original vision. I mean, when I talk to people about this technology, what really lights up their eyes is not finding security bugs, it’s that there’s not enough people to do the work. And by being autonomous and focusing on that value proposition, you’re really focusing on the pain point, which is, how do I do things that there’s just not enough highly skilled people to do.

    Ashley: Well, I applaud you for what you’re doing. You know, there’s yet another scanner, yet another anti-virus something. It’s great to see folks that are really doing some innovation, kinda thinking about the problem differently and really trying to solve it in a more systemic way, and that’s one of the things that I see that you’re doing. It isn’t just, we’re trying to test for these kind of behaviors, but it’s also in this ecosystem of how patches happen and things can happen dynamically, automatically.

    Brumley: Absolutely. I mean, we’ve had a number of customers who want us to support 10 different languages, but there’s no product in the world that can add 10 languages to support and also be really good at each one of them. For us, our main value proposition is, for everything we do, can we have zero false positives, can we make sure it’s actionable before we report it at all?

    Ashley: Awesome! Well, we’re—[Laughter] the time always flies by on these podcasts. Is there any last parting thoughts that you wanna share with us before we wrap up?

    Brumley: Well, thank you for having me and, as I said, we’d love to talk to you at Black Hat 2019.

    Ashley: Great, great. Well, I’ll be there as well, so we’ll get to meet up there. We’d love to have you on a future podcast as things develop and hear more about how things are moving along for you and ForAllSecure.

    Brumley: Thank you very much. Have a great day.

    Ashley: Well, another DevOps Chat podcast has flown by, as they always do. I’d like to thank David Brumley, CEO, at ForAllSecure for joining us today. Thank you, David.

    Brumley: Thank you.

    Ashley: And I’d like to thank you—you, our listeners—for joining us, of course. This is Mitch Ashley with staging-devopsy.kinsta.cloud. You’ve listened to another DevOps Chat. Thank you for joining us today.

    — Mitchell Ashley