

Claude Code’s Auto Mode was bypassed in an attack chain that turned a routine webpage summary into remote code execution, highlighting the limits of AI agent guardrails.
When AI Coding Agents Become Malware Delivery Systems
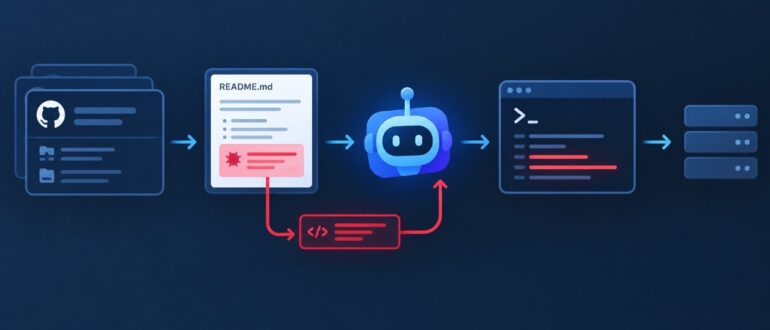
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search […]
Why “Tokenmaxxing” Was Always the Wrong Way for Developers to Measure AI Productivity

The term “tokenmaxxing” left the developer lexicon just as quickly as it arrived, and like most viral technology concepts, it means different things depending on who’s using it. In practice, […]
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat

Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies […]
What the Microservices Era Can Teach Us About AI

AI agents are not just microservices with LLMs attached. Their long-running, non-deterministic workflows demand durable execution, per-step identity, governance and observability.
Anthropic Makes Claude Code’s Auto Mode the Default, Betting Automation Beats Manual Review

Anthropic is making Claude Code’s auto mode the default for Pro, Max and Team users, replacing constant permission prompts with classifier-based guardrails designed to catch risky actions without slowing developers down.
Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA

Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published […]
‘GitLost’ Flaw Lets Attackers Trick GitHub AI Agent Into Leaking Private Repos

Noma researchers again show how easy it is to manipulate AI agents with malicious commands via indirect prompt injection attacks.
From Phishing to Vishing: Why DevSecOps Must Rethink Communication Security

Key Takeaways: Vishing is the new frontline threat: Attackers are shifting from emails to phone-based scams, using AI and social engineering to bypass traditional security controls. DevSecOps must expand its […]
Still Using API Keys for Your AI Agent? Here’s When it’s Time to Upgrade
API keys got you here. They won’t get you where you’re going. OAuth isn’t a future upgrade. It’s the foundation your agents should have been built on from the start.
