

Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published […]
CISA’s 2026 SBOM Guidance Adds Hash Requirements and AI Coverage

CISA’s updated 2026 SBOM minimum elements expand software transparency requirements to AI, SaaS and open source while adding hashes, licenses and stronger validation.
Cybersecurity Laws Will Shape the Future of DevOps
From the EU’s NIS2 Directive to U.S. SEC breach disclosure rules, cybersecurity regulation is accelerating faster than code releases. DevOps teams must evolve into RegOps—embedding compliance, traceability, and trust directly into their CI/CD pipelines. The future of DevOps isn’t just agile—it’s accountable.
CISA Pushes Steps to Better Secure Software and Product Designs
The country’s top cybersecurity agency is urging developers to take steps to ensure the software they’re building and the products they roll out are secure and protect end users. The […]
Most Critical Open Source Projects Lack Memory-Safe Code, CISA Says

The country’s top cybersecurity agency is continuing to urge software developers to adopt memory-safe programming languages to help reduce the number of vulnerabilities in their products.
CISA, NSA Issue Supply Chain Security Guidance Report
The NSA, ODNI and CISA have issued guidance to assist software developers and suppliers in shoring up software integrity and security.
I Guess This is Growing Up: Devs and CISA’s Secure-by-Design Guidelines
With the downward pressure of a global recession, inflation and general post-pandemic turbulence underpinning disruption to multiple facets of life, it seems only fair that we in the IT, software […]
Federal Agencies Share DevSecOps Guidelines

The National Security Agency (NSA), Cybersecurity and Infrastructure Security Agency (CISA), and the Office of the Director of National Intelligence (ODNI) have published a set of DevSecOps best practices based on […]
Live Fireside Chat with Christopher Krebs: How to Combat Disinformation

We live in a digital world where most information is now found online. This makes it increasingly difficult to verify the veracity of information. Threat actors have been taking advantage […]
Christopher Krebs to Keynote in Live Fireside Chat/Q&A Session at DevOps Connect: DevSecOps at RSA Conference 2021
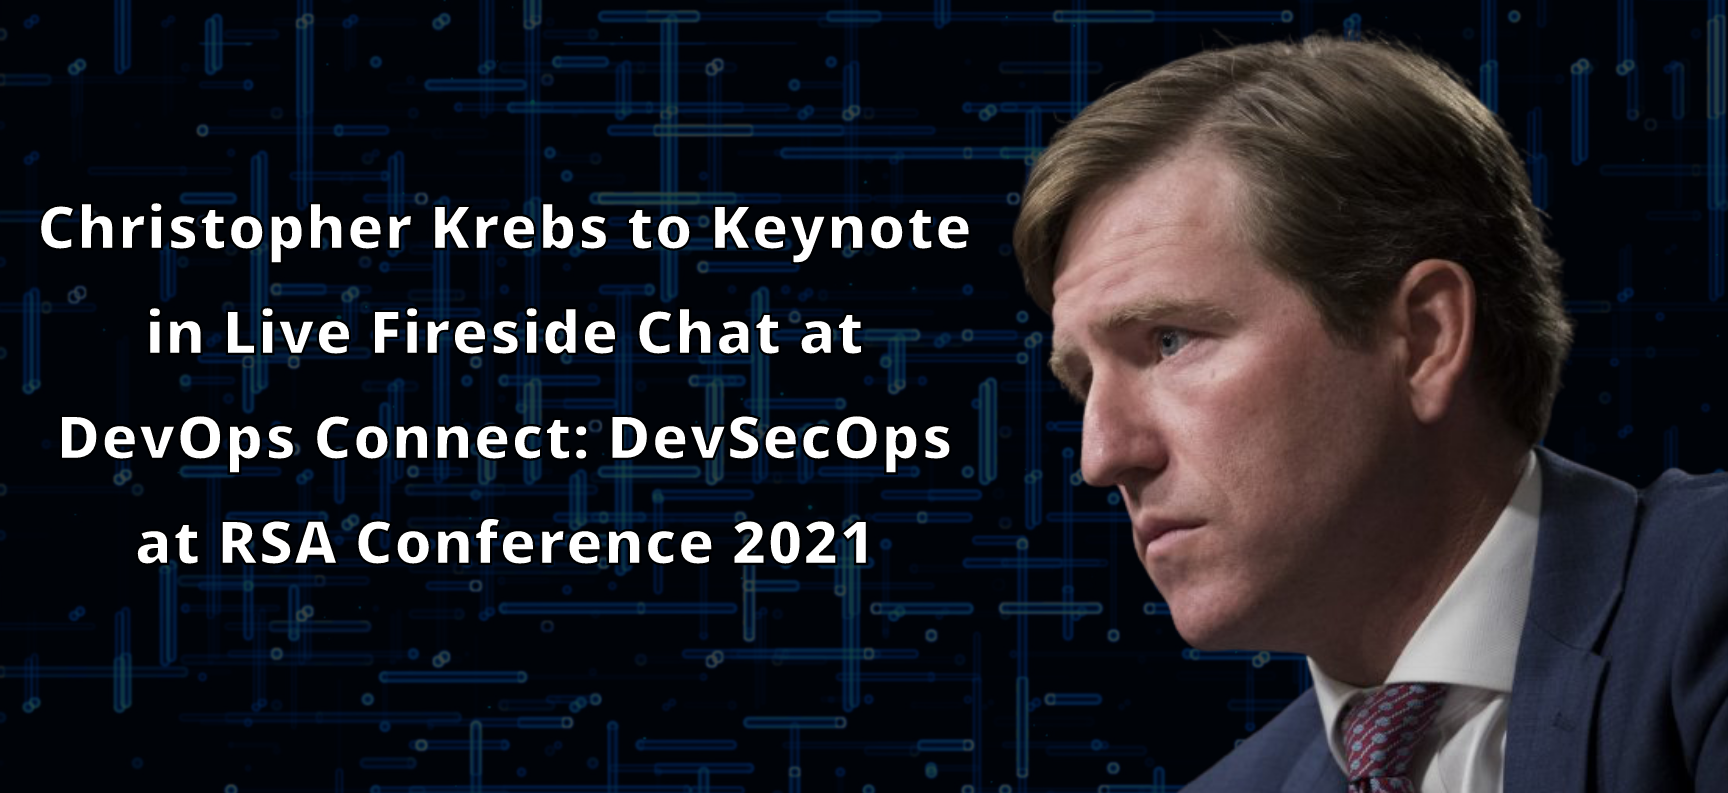
Former Director of Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA) to headline free one-day event Boca Raton, FL, April 26, 2021 — MediaOps, the place to tell your […]
