

Threat actors are exploiting a known security flaw in the SimpleHelp remote monitoring and management (RMM) software to drop two previously unknown pieces of malware that can compromise a broad […]
Bad Actor Drops 36 Malicious Packages in npm, Targets Guardarian Users

The npm code repository is again being used by a bad actor to launch a supply chain attack that includes three dozen malicious packages that appear as Strapi CMS plugins […]
Crates.io Removes Malicious Rust Package Targeting Web3 Developers
A malicious Rust package that was found to be downloading payloads aimed at stealing cryptocurrency was removed from the crates.io Rust package registry, along with another package by the same […]
WhiteCobra Targets Developers with Dozens of Malicious Extensions
A threat group is dropping two dozen malicious extensions into the VSCode and Open VSX marketplaces, targeting developers using the VSCode, Cursor, and Windsurf source code editing tools with the […]
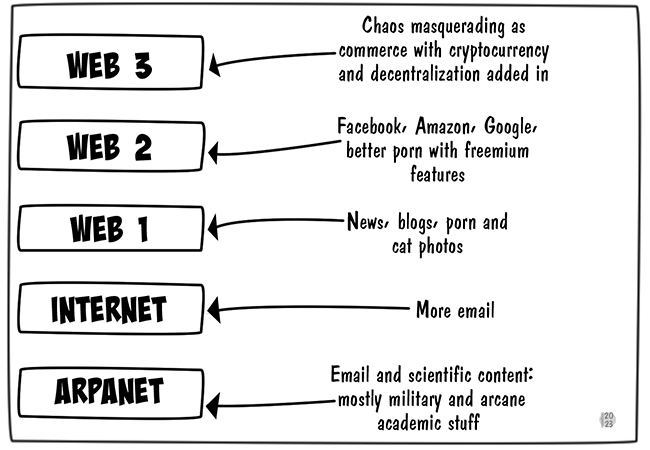
History of the Internet
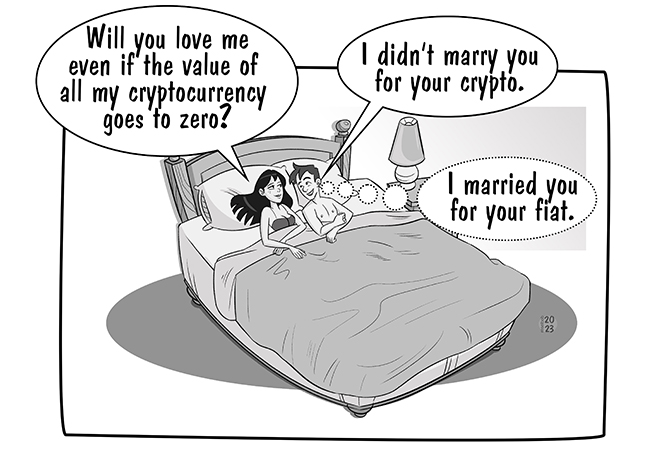
Risk and Speculation
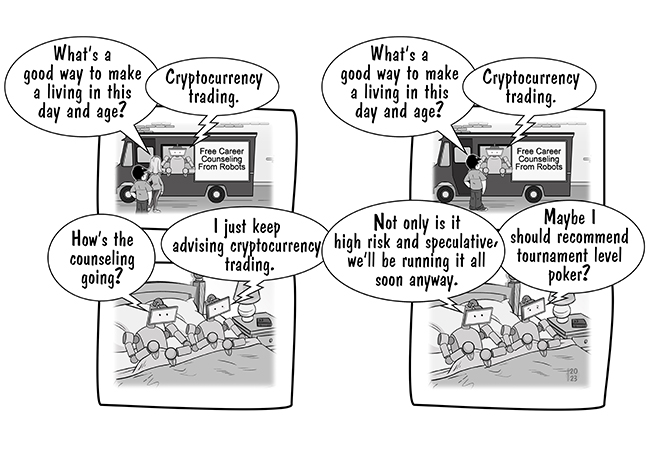
True Intentions
Best of 2022: Trends in Blockchain for 2022
As we close out 2022, we at staging-devopsy.kinsta.cloud wanted to highlight the most popular articles of the year. Following is the latest in our series of the Best of 2022. […]
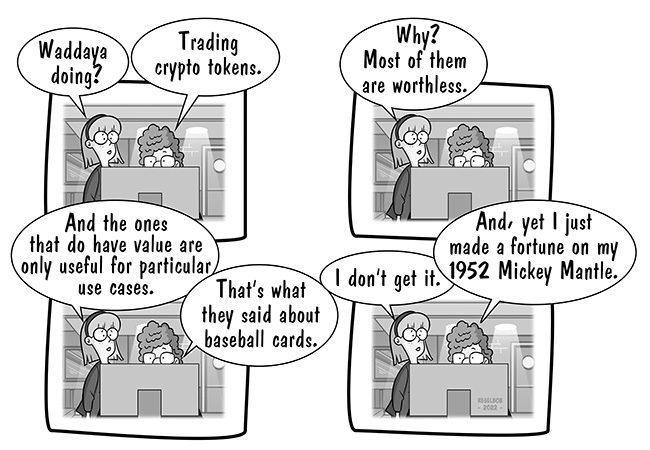
The Value of Commercial Value
Lapsus$ Shames Okta/Sitel | Bitcoin Nukes Climate | EU DMA E2EE FAIL
In this week’s The Long View: Okta and Sitel under fire over Lapsus$ hack, Greenpeace and others call for bitcoin change, and Europe still hates encryption.
