Author: Mike Vizard

  • CloudBees Acquires Neuralprints to Shift Compliance Left

    CloudBees Acquires Neuralprints to Shift Compliance Left

    At the online DevOps World 2021 conference today, CloudBees revealed it has acquired Neuralprints to provide the core technology for CloudBees Compliance, a real-time compliance and risk analysis platform that it will roll out in the first quarter of 2022.

    At the same time, CloudBees has enhanced the feature management capabilities of its namesake continuous integration/continuous delivery (CI/CD) platform to provide greater visibility into and control over feature flags that are now widely used to add new capabilities to applications.

    Prakash Sethuraman, chief information security officer (CISO) for CloudBees, said CloudBees Compliance will make it possible for DevOps teams to continuously enforce compliance policies as part of an effort to better secure their software supply chains. Those DevOps teams will be able to enforce compliance across code, binary artifacts, data, identity and infrastructure environments in a way that provides developers and IT operations teams with instant actionable feedback to enable issues to be addressed long before an application is deployed in a production environment.

    CloudBees Compliance is based on a mix of open source and proprietary technologies developed by Neuralprints and will be made available for on-premises IT environments as well as via a software-as-a-service (SaaS) application. The goal is to enable organizations to manage compliance as code as part of any effort to shift more responsibility for application security further left toward DevOps teams, said Sethuraman.

    CloudBees Compliance

    A survey of 500 C-level executives published today found nearly half (45%) admit that initiatives to secure their software supply chains are halfway or less-than-halfway complete. Nevertheless, 95% claimed their software supply chains are secure (95%), with more than half (55%) posting they are very secure.

    A full 93% said they are prepared to deal with an issue such as ransomware or a cyberattack on their supply chain. However, nearly two-thirds (64%) admitted they are not sure who they would turn to first if their supply chain was attacked; with 58% admitting that, if they experienced an attack, they have no idea what their company would do. An equal percentage (64%) said it would take more than four days to fix the problem if they did experience an issue.

    Almost all C-level executives (95%) said they think more about securing the supply chain now than they did just two years ago, and 92% said a security issue would impact their brand. A total of 83% said security issues cause their developers to drop everything to review code, with 82% noting that caused the organization to spend less time on innovation.

    On the plus side, 95% of executives said container images are checked for high or critical vulnerabilities, while an equal number said automation access keys are set to expire automatically. A total of 92% said their company only accepts commits signed with a developer GPG key, while 90% said dependencies to trusted registries are limited at their organization, while 89% said administrative access to CI/CD tools is restricted (89%).

    Of course, what C-level executives believe and what actually occurs inside an organization are not always one and the same. A series of high-profile software supply chain breaches resulted in a number of organizations reviewing their software supply chains. At the same time, the Biden administration has issued an executive order requiring all federal agencies to conduct similar reviews.

    One way or another, most organizations will soon find themselves embracing a wider range of DevSecOps best practices to ensure the integrity of software supply chains no matter how secure they may think their software development platforms are today.
  • Red Hat Extends Scope of Ansible Automation Ambitions

    Red Hat Extends Scope of Ansible Automation Ambitions

    During the online Ansiblefest, Red Hat announced the availability of a preview edition of Red Hat Ansible Automation Platform 2 that is intended to make it easier to automate IT processes at scale.

    Richard Henshall, senior manager for Ansible product management at Red Hat, said previously most IT teams have been automating individual processes, but as organizations become more adept at creating playbooks to automate processes, they now need to find ways to manage multiple automations that are often dependent on one another.

    Ansible Automation Platform 2 also enables IT teams to automate processes that span both monolithic as well as cloud-native applications based on containers using an automation controller, formerly known as Ansible Tower, that is more tightly integrated with Red Hat OpenShift, an application development and deployment platform based on Kubernetes, using Red Hat Operator tools. There is also an automation mesh capability that connects disparate automation components together and provides status checks.

    Ansible Automation Platform 2 also introduces automation execution environments within Ansible Engine that make it possible to create self-contained automation spaces that can be easily replicated and repeated across an organization.

    Red Hat also includes an automation content navigator to helps teams validate that automation content is working as it should across even the largest environments, along with updates to the Red Hat Insights analytics service that enable issues that might occur with automation controllers to be surfaced and eliminated by automatically applying policies.

    Henshall said going forward, IT teams should expect to see Red Hat focus more on enabling events to be the catalyst for triggering automation. Today, most automated processes begin with an IT administrator triggering the process. However, as digital business transformation initiatives mature, it’s become apparent there will be a need to trigger automation when specific events occur.

    Henshall said while there are still many organizations that are just starting to automate IT processes, there are also many that are entering the next phase of maturity. As such, they now require an automation platform that makes it simpler to manage automation at scale.

    In general, Ansible is designed to make it possible for developers and IT operations teams alike to declaratively create automation without much programming expertise required. However, creating a playbook that works reliably still requires a deep understanding of the processes that are being automated. Most IT teams would be well advised to closely monitor processes when they are first automated to make sure they are performing tasks as anticipated.

    Ultimately, it’s now a question of when rather than if most IT processes will be automated. DevOps teams, of course, have always been at the forefront of automation, but now it’s clear that as IT environments become more complex—with the rise of both the cloud and edge computing platforms—enterprise IT teams need to embrace automation more aggressively. The biggest barrier to automation is simply finding someone who has the passion to automate a process to lead the charge, said Henshall.

    Naturally, most of those efforts will initially focus on repetitive, tedious and manual IT tasks, but the potential to automate IT processes at levels of unprecedented scale has never been greater.

  • LogDNA Previews Streaming Module for Observability Platform

    LogDNA Previews Streaming Module for Observability Platform

    LogDNA is making available on a limited basis the ability to process streaming data to its observability platform as part of an effort to give DevOps teams more control over log data.

    Tucker Callaway, LogDNA CEO, said the data ingestion pipeline that LogDNA already provides can ingest, parse and normalize massive amounts of structured and unstructured log data. LogDNA Streaming adds the ability to automatically send log data to any application or analysis tool.

    That capability also helps reduce storage costs by limiting the number of copies of log data that might otherwise be created, he added.

    LogDNA also expects that DevOps teams will also be able to analyze data in flight as part of an effort to make it simpler to surface issues even before log data is stored, noted Callaway.

    While there are multiple streaming data platforms available, Callaway said LogDNA opted to build one on its own to meet the requirements of an observability platform. Ultimately, the goal is to shift observability left at the data level to provide more granular insights in real-time, he said.

    That capability will also lay the foundation for a wide range of autonomous processes that would be driven by the observability data collected via LogDNA, added Callaway.

    LogDNA

    Observability has always been a core tenet of any DevOps best practice. Most DevOps teams typically focus on some form of continuous monitoring to more proactively manage application environments. However, it can still take days, sometimes weeks, to discover the root cause of an issue. Monitoring tools are designed to consume predefined metrics to identify when a specific platform or application is performing within expectations. The metrics tracked generally focus on, for example, resource utilization.

    Observability combines metrics, logs and traces—a specialized form of logging—to instrument applications in a way that makes it simpler to troubleshot issues without having to rely solely on a limited set of metrics that have been pre-defined to monitor a specific process or function. DevOps teams can more easily employ queries to interrogate data in a way that makes it easier to discover the root cause of an issue. An observability platform correlates events in a way that makes it easier for analytics tools to identify anomalous behavior indicative of an IT issue.

    It’s now only a matter of time before providers of the platform widely employ machine learning algorithms to analyze machine data faster. There may even come a day when so-called “war room” meetings—that today need to be convened to identify the cause of an IT issue via a painstaking process of elimination—are no longer required.

    In the meantime, the percentage of applications that are instrumented in an IT environment needs to increase to achieve that goal. Fortunately, thanks to the rise of open source agent software, the cost of instrumenting applications is starting to decline. At the same time, DevOps teams should expect to see a marked increase in the volumes of incoming data, and they will need to find somewhere to store that data as well as determine the length of time it should be retained.

  • Relyance AI Shifts Compliance Left Using ML Algorithms

    Relyance AI Shifts Compliance Left Using ML Algorithms

    Relyance AI emerged from stealth this week to unveil a namesake platform for managing privacy and data governance in real-time within the context of a larger DevOps workflow.

    Fresh off raising $30 million in seed capital, Relyance AI co-CEO Leila Golchehreh said organizations can now quickly and accurately answer essential privacy questions and ensure compliance and governance by mapping requirements directly to their codebase. The platform provides transparency and visibility all the way down to the source code in real-time using machine learning algorithms, she added.

    Relyance AI co-CEO Abhi Sharma also noted most legal and data protection teams today have limited visibility into digital operations. Developers and data scientists are constantly creating and updating applications. By the time compliance teams gather the data required, it’s obsolete, said Sharma.

    The Relyance AI platform analyzes contractual requirements against the operational reality as determined by data processing in real-time. Compliance teams can then address privacy issues as they arise, added Sharma.

    At the core of the Relyance AI platform are five integrated components that first inventory assets by connecting to application programming interfaces (APIs); generate universal records of processing activities (ROPAs) by scanning code and understanding how data is being processed; share alerts when issues are detected; provide views into data life cycles to highlight data subject access request (DSAR) exceptions and extensions and address vendor life cycle management to ensure third-parties are complying with policies.

    Relyance AI

    Sharma said compliance, much like security, is shifting further left toward application development as organizations look to eliminate issues before they arise in a production environment. The Relyance AI platform is designed to be integrated with continuous integration/continuous delivery (CI/CD) platforms that are the core of modern software development life cycle processes, he added.

    Undoubtedly, as the worlds of compliance and application development collide, there will be cultural challenges similar to what is now occurring with the rest of DevSecOps best practices that require more collaboration between developers and security teams. The challenge is compliance officers tend to be even further removed from application development than their IT security counterparts.

    However, it’s now only a matter of time before compliance becomes code. Modern applications already make use of the Open Policy Agent, for example, to embed compliance rules in applications. AI platforms should make it simpler to identify compliance issues as they arise so that they can be addressed before any infraction ever occurs.

    DevOps teams, of course, have a vested interest in managing compliance as code. It’s not uncommon for DevOps teams to race to build and deploy an application only to encounter a wave of compliance issues that need to be addressed by recoding elements of the application. Not surprisingly, those compliance issues often result in application delivery deadlines being missed. Machine learning algorithms provide an alternative to the current raft of documents that compliance officers create, but not enough other members of the IT team read those, much less understand them.

  • Dell Updates AIOps Platform to Better Automate IT Ops

    Dell Updates AIOps Platform to Better Automate IT Ops

    Dell Technologies this week updated its IT operations platform infused with artificial intelligence, dubbed CloudIQ, to add support for its PowerEdge servers. In addition, Dell pledged to add support for its PowerSwitch networking hardware next month as part of an ongoing effort to extend the reach of its AIOps platform across the entire Dell EMC portfolio.

    At the same time, Dell next month also plans to employ webhooks and a REST application programming interface (API) to both integrate the CloudIQ cloud service with third-party platforms and share notifications and recommended actions via tools and platforms such as ServiceNow, Slack, Microsoft Teams, Ansible and vRealize.

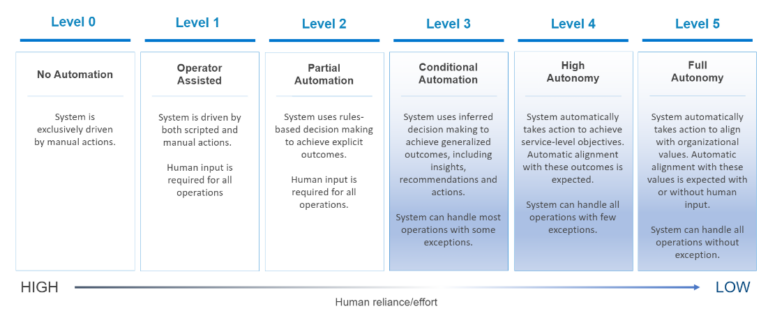
    Dell has also defined an autonomous operations framework that defines the various stages of AIOps capabilities that organizations should be able to take advantage of as CloudIQ continues to evolve.

    Dell AIOps

    Drew Schulke, vice president of product management for Dell Technologies, said CloudIQ currently enables IT organizations to achieve level three of that framework. As Dell continues to update CloudIQ alongside delivering ongoing infrastructure upgrades, additional capabilities will be steadily added, noted Schulke.

    Dell is making a case for standardizing on both its infrastructure and the IT operations platform it provides. Whether acquired and managed by an internal IT team or consumed as-a-service provided by Dell, the goal is to convince IT teams to reduce their reliance on rival infrastructure platforms that are not as tightly integrated with CloudIQ. In effect, Dell is delivering continuous intelligence as an AIOps service, said Schulke.

    Of course, IT operations teams could opt to standardize on an AIOps platform that is integrated with infrastructure provided by multiple vendors. However, Dell is betting that an AIOps framework optimized for its platforms will reduce the total cost of IT in a way that IT organizations will not be able to ignore.

    Each IT organization will need to decide for themselves what path forward makes the most sense for them. However, as more AI capabilities are infused into IT operations platforms, it’s becoming clear that many of the tasks routinely performed by IT teams are becoming increasingly automated. Most organizations will need to make a decision in the months ahead about the degree to which they are comfortable waiting for their existing IT operations platform to be enhanced with AI capabilities versus acquiring a new one that might be more advanced.

    Regardless of the path forward, the level of cultural disruption AIOps will bring to IT teams will be high. DevOps teams, naturally, have always been at the forefront of IT automation. However, most of the recent advances in IT operations have generally been applied in a piecemeal fashion. Platforms such as CloudIQ are designed to be implemented on a more end-to-end basis.

    Thate level of automation will have a profound impact on everything from the number of applications an IT team can support to the roles of the individuals that make up that team. It’s not likely that AIOps will replace the need for those IT teams as much as augment them and redefines the job they are being asked to perform.

  • Clubhouse Becomes Shortcut to Transform Software Project Management

    Clubhouse Becomes Shortcut to Transform Software Project Management

    Shortcut, formerly known as Clubhouse Software, today announced that its project management software for software development teams has been expanded to include additional workflow capabilities.

    CEO Kurt Schrader said team-to-workflow functionality is being added to the software-as-a-service (SaaS) platform and will make it easier to share workflows across software development teams in a more standardized way.

    Organizations can standardize workflows across multiple teams while still giving each team the ability to customize workflows for their own unique processes. As work gets created and assigned, it automatically moves into a workflow without having to manually update processes.

    Shortcut is designed to make it simpler for development teams to collaborate in a way that maintains transparency with other teams working on projects that are part of the same larger initiative, said Schrader. It allows product managers, engineers and designers to plan, track and measure their work without friction as the organization continues to grow in size, he added.

    For example, Shortcut will surface what teams need to focus on as priorities and timetables change within a specific project in addition to allowing users to define sprints using start and end dates, and the tool then sends reminders so the team can reserve time to focus on specific projects.

    Shortcut will also integrate with continuous integration/continuous delivery (CI/CD) platforms via application programming interfaces (APIs) to enable the development of custom workflows that include, for example, integration with real-time conversations occurring via the Slack collaboration service.

    Most of the project management software DevOps teams employ today is too complex and intimidating for the average business executive. Rather than forcing business users to learn how to master these applications, a case can be made for a more intuitive set of project management tools for both software development teams and the product managers they ultimately serve.

    As more organizations realize how dependent they are on software to drive business processes, many of them are reviewing the tools they currently rely on to manage software development. The goal is to not only reduce friction and enable more transparency across teams but also to provide stakeholders outside of the development team with more visibility into the status of any given project.

    At the same time, organizations are simultaneously launching more software development projects that have many dependencies. Many of those initiatives are based on microservices that are being built in isolation from one another before being aggregated to create an application. The dependencies between those microservices require organizations to make sure they are developed and deployed in a way that doesn’t leave one software development team waiting on another to finish a project before they can complete their work.

    Shortcut

    Schrader said that humans, as a species, are bad at organization. Project management applications should make it simpler for companies to understand how projects are not only organized but also all the dependencies that exist between them.

    Regardless of how software development projects are managed the need for greater visibility is obvious to all. Less clear is the best way to go about achieving that given all the communications channels available.

  • Google DORA Report Shows Modest DevOps Gains

    Google DORA Report Shows Modest DevOps Gains

    Google today published the annual Accelerate State of DevOps Report created by its DevOps Research and Assessment (DORA) team that finds 26% of DevOps teams surveyed can now be classified as elite performers. That compares to 20% the last time the study was conducted in 2019.

    DevOps teams, made up of a total of 32,000 IT professionals from around the globe, were evaluated based on their ability to frequently deploy, code, lead time for changes, time to restore service, change failure rates and operational performance. An elite team is expected to be able to restore service in the event of an outage in less than an hour.

    Dr. Dustin Smith, a user experience researcher for Google, said the increased rate suggests steady gains in DevOps maturity continue to be made despite all the challenges the COVID-19 pandemic presented. A full 96% of respondents said that prior to the pandemic they had not worked from home on a regular basis.

    The DORA report finds high and elite performers make up two-thirds of respondents. Elite performers were able to collectively decrease their lead time for changes when compared to previous studies. It’s also worth noting only elite performers have minimized their change failure rate. In previous years, medium and high performers were able to do the same.

    Overall, more than half of respondents (52%) report they have adopted site reliability engineering (SRE) best practices to some degree.

    Elite performers deploy code 973 times more frequently than low performers, who reported deploying less than once every six months. The normalized annual deployment numbers range from 1,460 deploys per year for the highest performers to 1.5 deploys per year for low performers. Not surprisingly, for elite performers, the lead times from commit to deploy are 6,570 times faster than low performers.

    Security practices have also improved with 60% conducting security reviews, with 58% reporting that the reviews include testing. Nearly two-thirds (63%) said they work closely with information security teams. The report finds teams with high-quality documentation were 3.8 times more likely to integrate security throughout their development process.

    Reliance on cloud platforms has also increased, with 56% of respondents indicating they employ a public cloud, a 5% increase from 2019. Only 21% of respondents reported deploying to multiple public clouds. Over a quarter (26%) of respondents did so to leverage the unique benefits of each cloud provider, followed closely by 22% that cited availability.

    Just over a third (34%) report they are using a hybrid cloud, while 29% have a private cloud. A total of 21% still don’t use a public cloud.

    The report also finds elite performers were 3.5 times more likely to have met all essential cloud characteristics defined by the National Institute for Standards and Technology (NIST). Those characteristics are defined as on-demand self-service, broad network access, resource pooling, rapid elasticity or expansion and measured service. Only 32% of respondents who said they were using cloud infrastructure agreed or strongly agreed that they met all five of the essential characteristics of cloud computing defined by NIST, an increase of 3% from 2019. Overall, usage of those characteristics of cloud computing have increased by 14% to 19%, with rapid elasticity showing the largest gain.

    The DORA report makes it clear there is still a long way to go before DevOps nirvana is more widely achieved. On the plus side, however, the number of organizations that have embraced DevOps to some degree continues to steadily increase.

  • OpsRamp Extends AI Reach to Incident Management

    OpsRamp Extends AI Reach to Incident Management

    OpsRamp today extended its IT operations platform infused with machine learning algorithms, also known as AIOps, into the realm of incident management.

    The Summer 2021 release of the company’s namesake platform adds alert predictions for preventing outages and incidents, alert enrichment policies for faster incident troubleshooting and enhancements for automatically ingesting metrics data collected from the Alibaba Cloud environment and open source Prometheus monitoring software as well as Hitachi, Poly, VMware and Dell EMC platforms.

    IT operations teams can now also visualize metric values that can increase or decrease within a fixed range using Gauge charts. IT teams can also now add alert context details to provide more relevant information. There’s also now a mobile app for both Apple iOS and Google Android devices through which IT teams can now respond to alerts and incidents.

    Finally, OpsRamp is also making available a beta release of dynamic Workflows, which enable IT team to maintain a single decision table to address specific operational scenarios.

    Sheen Khoury, chief revenue officer at OpsRamp, said the goal is to leverage artificial intelligence (AI) to increase application availability by enabling IT teams to better predict when there are indicators of an incident caused by, for example, higher volumes of seasonal traffic that could lead to an outage.

    At the same time, IT operations teams can improve overall time-to-value by leveraging the automatic monitoring tools that are embedded in the platform, he added.

    OpsRamp is betting that rather than waiting for incumbent providers of IT operations platforms to add AI capabilities, many IT teams will opt to deploy a new IT management framework altogether. Many of the manual tasks IT operations teams regularly perform today can then be automated faster, noted Khoury.

    Naturally, it takes time for machine learning algorithms to be trained, so the benefits of AIOps are not instantaneous. However, those algorithms will continuously learn the unique attributes of an IT environment in a way that makes it easier for IT teams to manage an IT environment more proactively. The algorithms provide the added benefit of making it easier for new members to join an IT operations team without having to spend months learning all the nuances that are unique to that environment.

    Each IT team will need to decide for itself the degree to which they want to rely on an AIOps platform to manage their IT environment. Initially, most IT teams will need to evaluate the recommendations made by an AI platform. However, as they gain confidence in the recommendations, they will trust the platform to automate more processes in response to events occurring in the IT environment in real-time.

    Regardless of how much faith IT teams put in AI, it has become apparent that enterprise IT environments are only going to become more complex. Many IT teams will not be able to manage some environments without the aid of an AI platform. Many IT professionals may not want to work for organizations that don’t provide some way to augment their skills using AI—the stress level would simply be too high.

    One way or another, DevOps teams that are highly committed to ruthlessly applying automation will be at the forefront of AI adoption in the enterprise.

  • Sentry Integrates Code Observability Tool with GitHub, GitLab

    Sentry Integrates Code Observability Tool with GitHub, GitLab

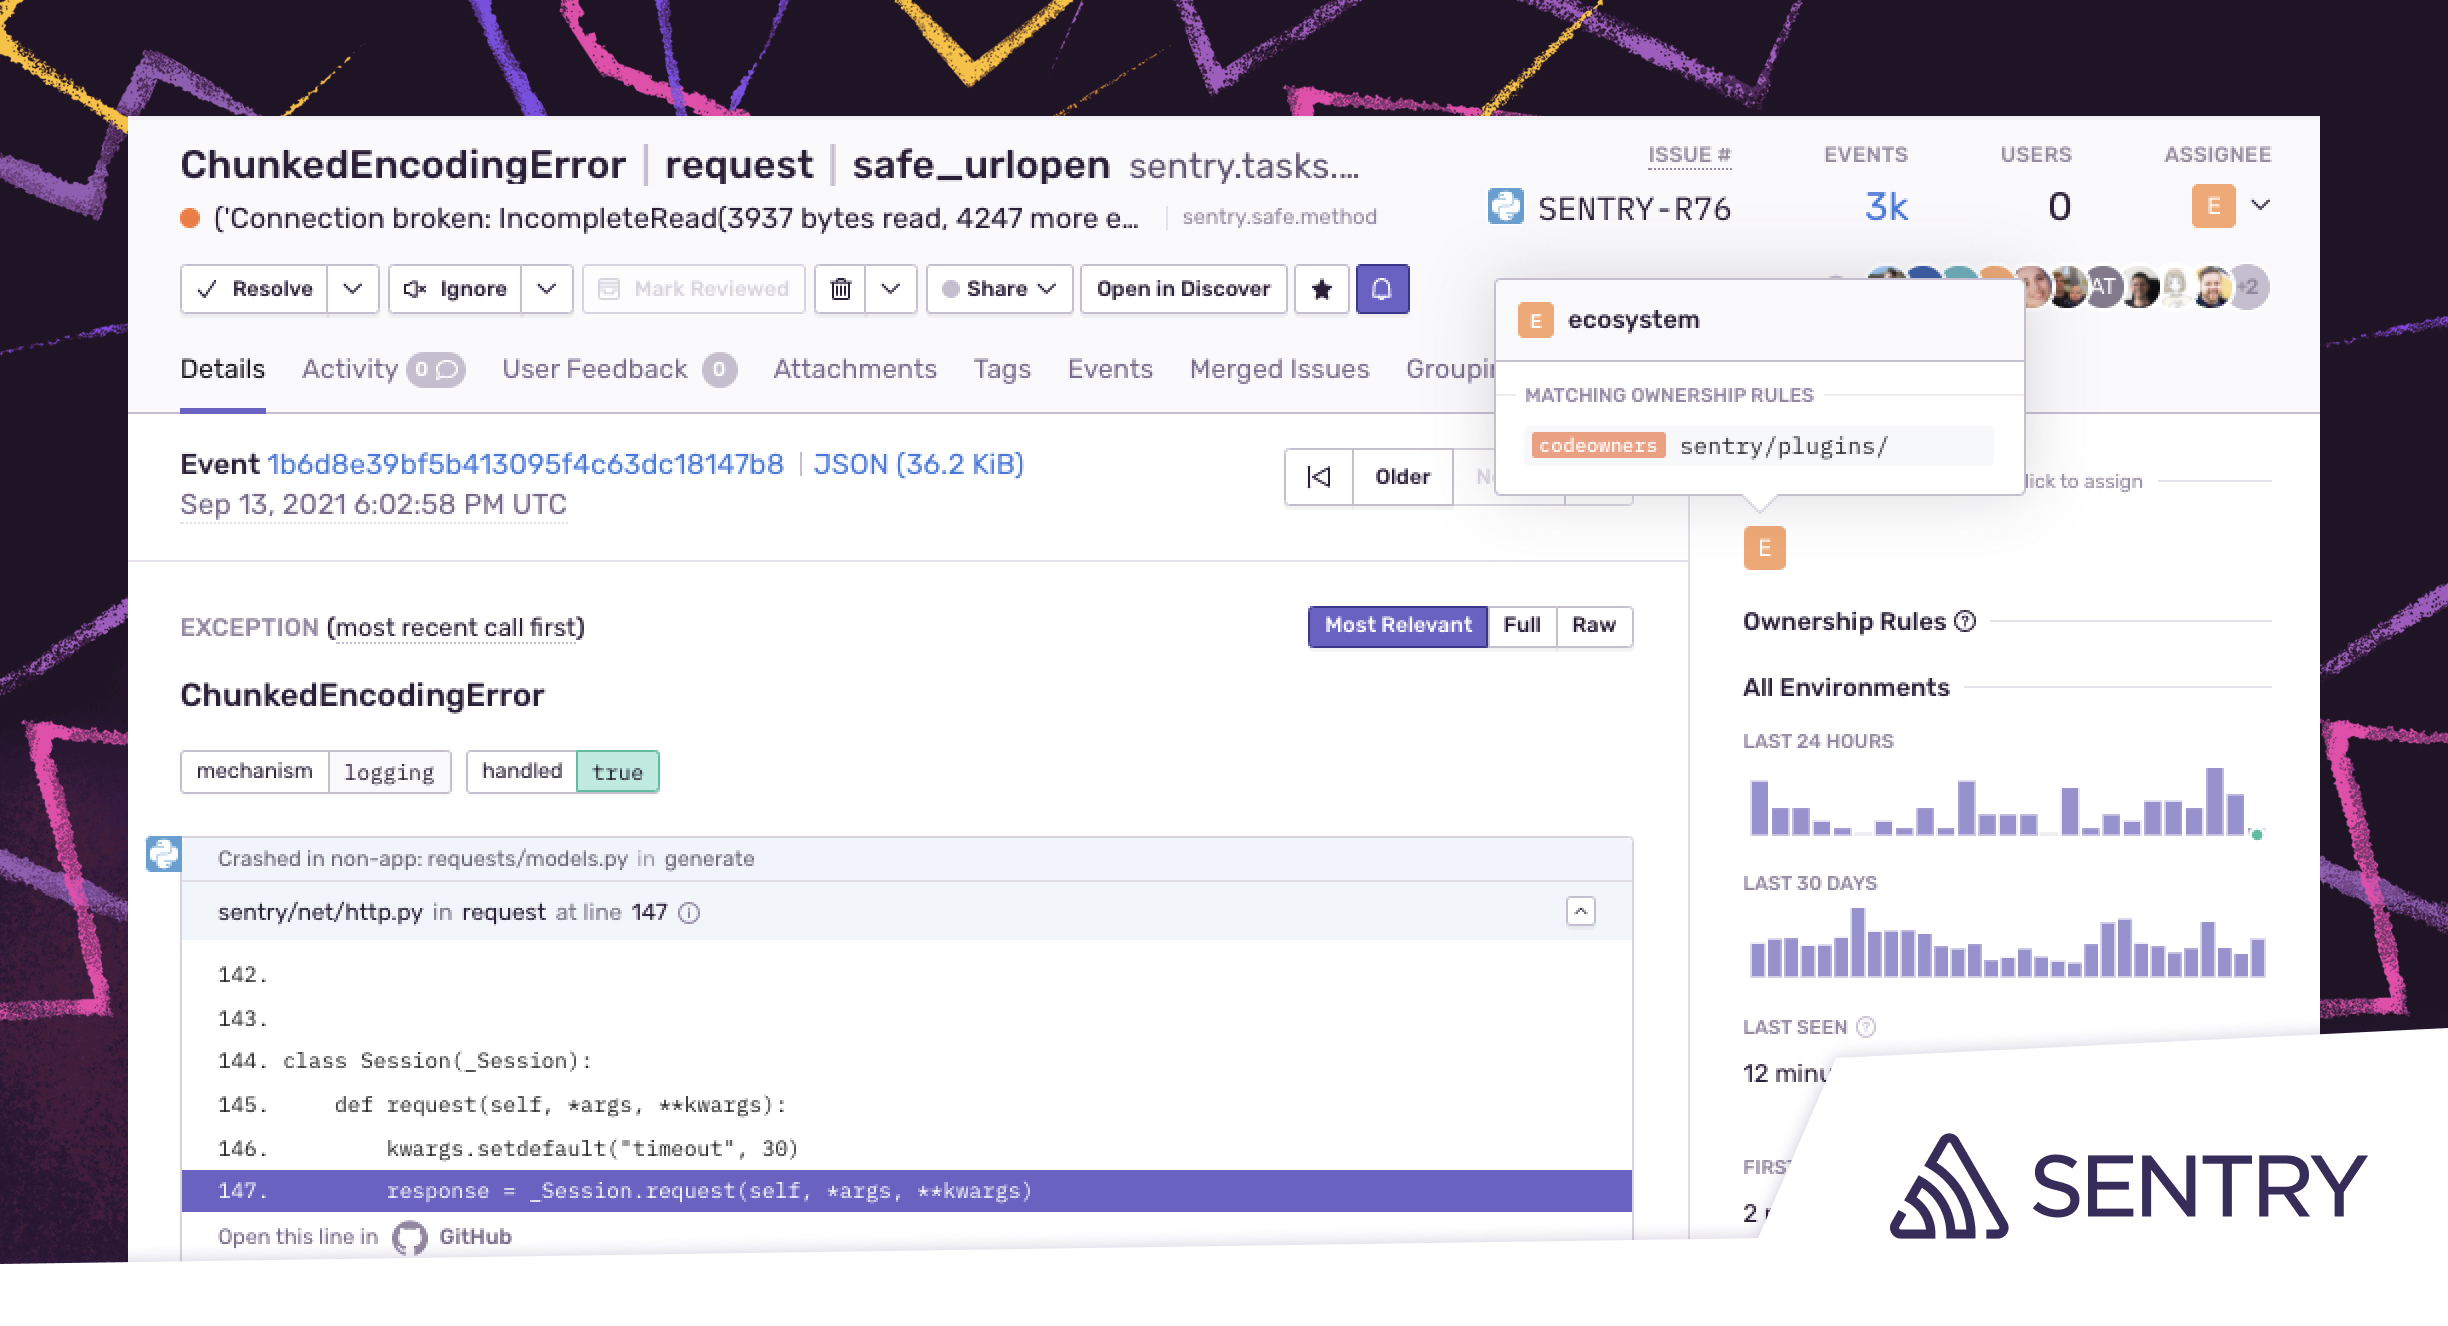
    Sentry this week extended its namesake observability platform for code to provide tighter integration with the DevOps platforms provided by GitHub and GitLab.

    Application development project managers can now assign issues to DevOps teams by integrating directly with the CODEOWNERS file in GitHub or GitLab. Error messages, for example, can now be automatically routed to individuals or teams that own the code via notifications in Slack.

    IT teams can now also identify and prioritize issues based on user impact by setting alerts based on when an issue exceeds a certain percentage of user sessions within a specific amount of time.

    Sentry CEO Milin Desai said that the percentage-based approach to alerts reduces the overall noise being generated in a way that enables DevOps teams to better prioritize their remediation efforts.

    Finally, Sentry has added an integration with the Okta identity management platform to make it possible to automatically provision and de-provision users and teams using the system for cross-domain identity management.

    As more responsibility for managing the application environment shifts left toward developers, there needs to be a way to streamline communications between developers and the rest of the IT operations team, noted Desai. Most developers today already spend less than one-third of their time writing code.

    The Sentry platform is already used by more than 75,000 organizations to enable developers to better observe and analyze code behavior. The company is now moving to bridge the divide between developers and site reliability engineers (SREs) by streamlining communications and workflows, noted Desai.

    As the responsibility for managing applications shifts left, developers don’t necessarily want to use the same tools that IT operations teams have relied on for years. Most developers want to be able to troubleshoot their applications with minimal interaction with IT operations teams.

    Historically, IT operations teams have relied on application performance management (APM) platforms to manage IT operations. Those platforms are now evolving into observability platforms that promise to provide more context by correlating events as they occur across both applications and IT infrastructure platforms. That approach, however, typically requires developers to insert agent software into their applications. Once inserted, that agent software needs to be maintained and updated, added Desai.

    The Sentry approach provides developers with a tool for collecting data from an application in a way that consumes just tens of kilobytes of memory after being embedded directly within an application. That approach eliminates the need to rely on much larger agent software to achieve observability of application code. Developers can then diagnose and possibly remediate issues in code without ever having to create a ticket asking a DevOps team to investigate an issue.

    Regardless of how developers go about instrumenting their applications, most everyone in IT agrees that the current state of observability needs to improve. The issue now is determining how best to achieve that goal in a way the benefits both the DevOps team and the developers that are now being asked to not just write code but also manage the entire application life cycle.

  • Transposit Survey Shows DevOps’ Impact on CIO, CTO Relationship

    Transposit Survey Shows DevOps’ Impact on CIO, CTO Relationship

    A survey of 415 CIOs and CTOs conducted by Transposit, a DevOps process orchestration platform provider, finds that as organizations continue to adopt DevOps processes more widely, friction between these types of senior IT leaders is rising within many organizations.

    As a C-level role, ‘CTO’ first gained traction in the wake of the dot com boom. In more recent years, many traditional enterprises added CTOs alongside CIOs as they realized how dependent the organization had become on software. In the wake of the COVID-19 pandemic, there is now more focus than ever on digital business transformation initiatives that are dependent on the timely delivery of software.

    Transposit CEO Divanny Lamas said that as more organizations’ structures revolve around product teams, there are a lot more CTOs. In some cases, CIOs are reporting to CTOs.

    The majority of organizations surveyed have both roles. A full 83% of CIOs said there is also a CTO at their organization, while 86% of CTOs said there is also a CIO. Just under a quarter of respondents (24%) said they perform both roles.

    At the same time, 98% of survey respondents reported increased focus on digital transformation within their organization in the past three years, with three-quarters (75%) noting that focus has increased since the start of the pandemic. A full 85% report their budget has increased over the last three years.

    Not surprisingly, 92% of respondents said that their responsibilities have changed in the last three years, with over half (56%) reporting their role changed significantly. Both are now graded according to key performance indicators (KPIs) related to managing revenue, with 66.3% of CIOs and 78% of CTOs saying their position is now either directly involved in or required to lead a business strategy.

    But only 34%, or just over a third, said that ownership of most aspects of digital transformation initiatives is a shared responsibility between the CIO and CTO. Specifically, just under a third (32%) noted ownership of software development in their organization is a shared responsibility. A full 88% of respondents apply DevOps practices, and 83.4% believe that DevOps is important to digital transformation at their organization. Almost all (98%) plan to expand their DevOps practice, and 83% already have a plan in place to do so.

    Lamas says software engineering-first principles are changing not just how applications are built but also how IT teams are structured in a way that advances innovation.

    More than a third (35%) of respondents said ownership of software operations developed in-house is a shared responsibility in their organization, while 28% said ownership of managing SaaS or operating commercial off-the-shelf (COTS) software in their organization is a shared responsibility. A third (33%) also noted ownership of the technology for the external customer experience in their organization is a shared responsibility.

    A full 95% of survey respondents also confirmed that the performance of their team is measured by key performance indicators (KPIs) related to revenue, specifically revenue growth (75%), rate of innovation (60%) and uptime (54%).

    It’s too early to say how the relationship between CIOs and CTOs will evolve, but the one thing is clear: The pressure for these roles to collaborate more effectively is on the rise.